Black Hat USA 2026 | Threat Modeling LLMs: The PHANTOM-B model
Source: YouTube · Black Hat · published Nov 17, 2026 · 40:28
Adam Shostack's Black Hat talk introduces Phantom B, a new mnemonic threat modeling framework for deployed LLM systems, arguing threat modeling best secures AI amid rapid disruption 1:01.
Key Takeaways:
• Threat modeling rests on four questions—what are we working on, what can go wrong, what will we do, did we do a good job—and is the "measure twice, cut once" of engineering 2:37.
• Executives are scared as AI disrupts business, while "cognitive debt" grows as developers lose understanding of LLM-generated code 3:50, 5:27.
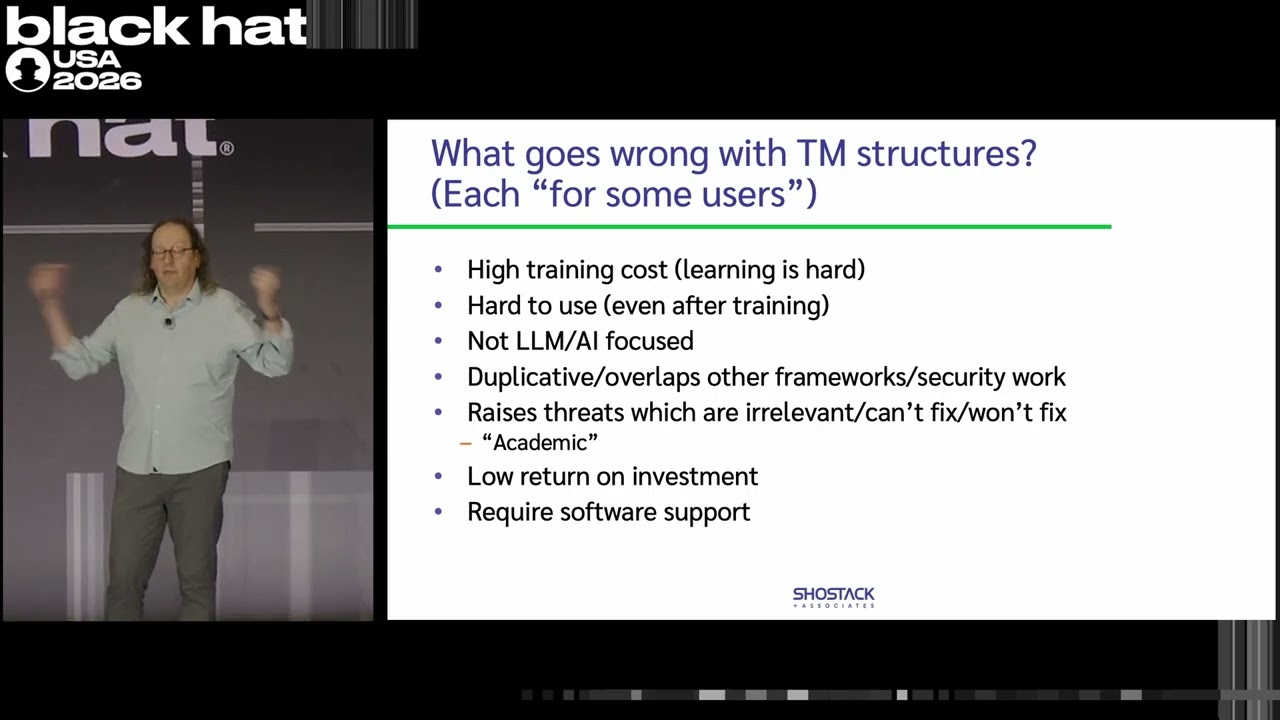
• Phantom B targets business LLM deployments (chatbots, document processing, decision-making) because catalogs like MITRE Atlas, OWASP, and NIST are costly, duplicative, or aimed at model creators; it fits on a wallet card and complements STRIDE 8:51, 13:01.
• Its eight threats: prompt injection (code/data confusion, no deterministic fixes), hallucination, anthropomorphization ("don't do X" prompts backfiring), non-explainability, training issues (unsolved data poisoning via ~250 documents), over-reliance, missing security engineering, and bias 17:42, 24:38, 28:45.
• In practice, apply STRIDE across a data flow diagram and pivot to Phantom B where an element involves LLM/token generation 34:31.
Threat modeling surfaces "what can go wrong" before shipping, giving teams the most options—Phantom B balances coverage and accessibility for LLM risks 32:03.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
[applause] >> The emperor is most displeased with your lack of AI progress. And I'm here today to talk about what we're going to do about it. So, hello. I am Adam Shostack. And what I want to share with you today is every one of our customers feels like Darth Vader is breathing down their neck saying, "When the heck are we going to ship this? How the heck are we going to secure this?" They're not using the word heck, by the way, but I will. Um And so, the way I'd like to organize this is I'm going to share with you some threat modeling context, some level set, so that we're all starting from the same page. Going to talk about how we threat model LLMs. And then I'm going to talk about the Phantom B approach, where it came from, why we think it's a useful addition to your toolbox. So, I'm Ad…