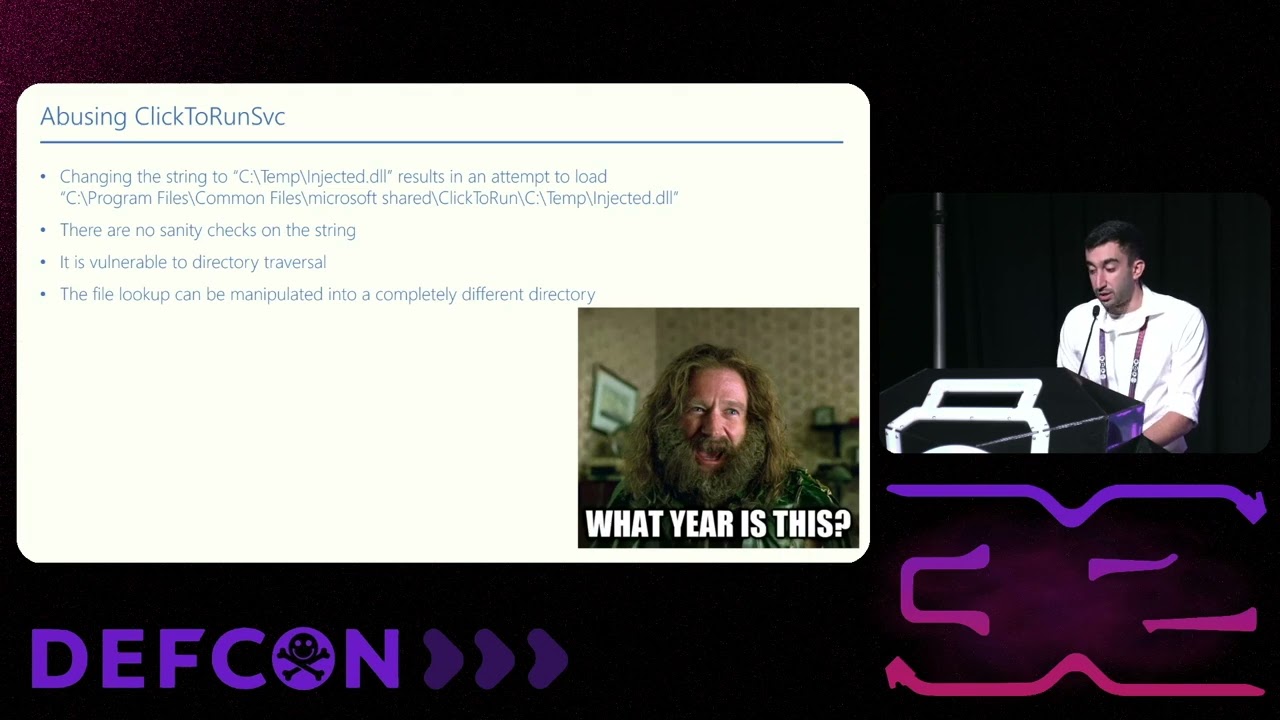
DEF CON 32 - Manipulating Shim and Office for Code Injection - Ron Ben-Yizhak, David Shandalov
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 41:11
The speakers detail a two-part attack on Microsoft Office's app compatibility framework, leveraging RPC, opportunistic locks, and undocumented APIs to achieve code injection and privilege escalation without detection.
Key Takeaways:
• Office's compatibility mechanism allows code injection via RPC in the Click-to-Run service, enabling DLL injection into suspended processes 5:01-7:09.
• By manipulating the App Compatibility Cache using undocumented APIs, attackers can force a process to load a malicious DLL without registry changes or file persistence 18:03-31:09.
• A novel "Fest" attack injects a DLL into a suspended process (e.g., Microsoft Edge Updater) by modifying the process environment block (PIM data), bypassing EDR detection due to early injection timing 33:02-36:59.
• Privilege escalation from admin to system is achieved by targeting scheduled tasks that launch suspended processes, exploiting oplocks to delay process resumption 12:30-19:43.
These attacks evade detection by leveraging legitimate OS mechanisms, avoiding file system changes, and injecting code before EDRs can establish hooks.
Sources:
- 5:01 Discussion of RPC-based DLL injection in Office Click-to-Run service.
- 18:03 Exploitation of anti-AppCompat cache control to trigger DLL loading.
- 33:02 "Fest" attack using PIM data manipulation for fileless, registry-less injection.
- 12:30 Use of opportunistic locks to suspend and delay process resumption for privilege escalation.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hello everyone thank you for coming to our talk shimy what you got manipulating shim and office for code injection we're very excited to be here let's introduce ourselves my name is Ron Ben isak I'm a security researcher at Deep Instinct and this is the third year in a row I'm speaking here at Devcon and my name is David shandalov I'm also a security researcher at Deep ins and this is my first time here this is what this is what we're going to talk about today I'll start with an intro about the app compatibility framework what it is made of and known techniques to abuse it then I'll dive in into our attx surface research on Microsoft Office I'll show how we found an interesting RPC method and combined several manipulations into a single attack that achieves both code injection and privileg…