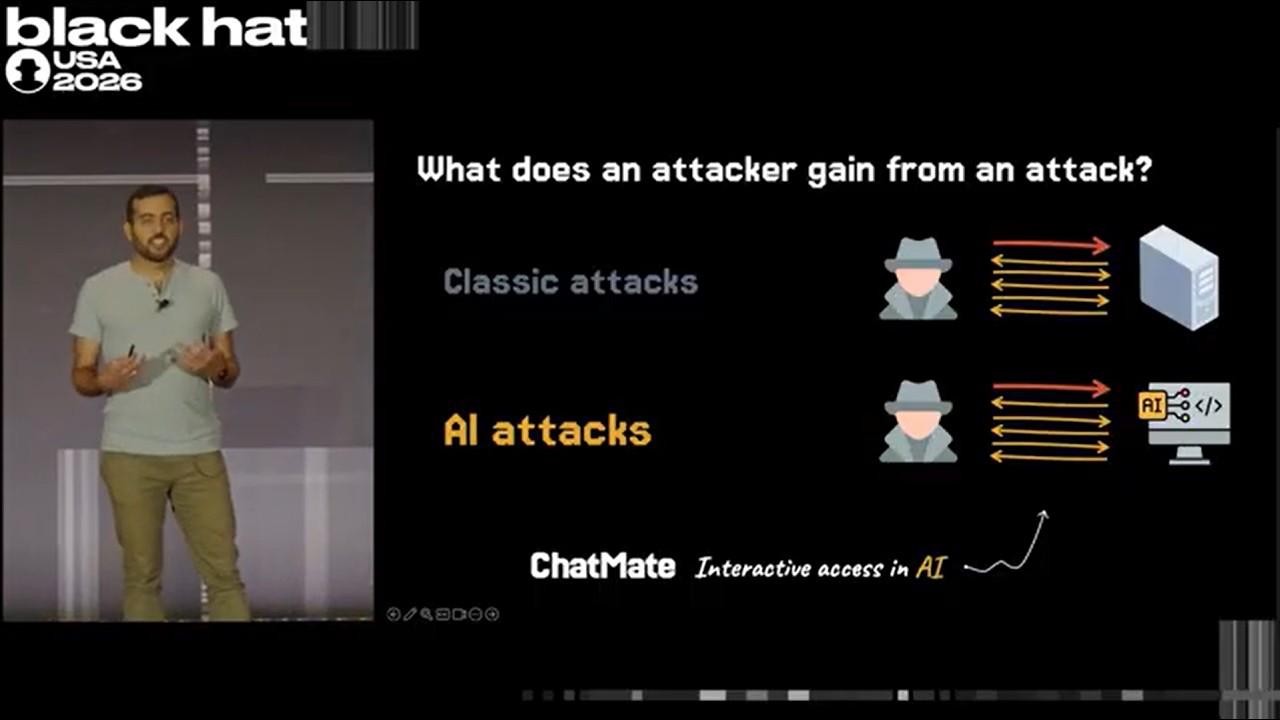
Black Hat USA 2026 | ChatMate: Remote Prompt Execution on AI Assistants through Sandbox Escaping
Source: YouTube · Black Hat · published Nov 13, 2026 · 36:15
A Rubrik Zero Labs researcher chained prompt injection, sandbox code execution, privilege escalation, and an Azure infrastructure bug to gain full interactive access to a victim's Microsoft Copilot 0:14.
Key Takeaways:
• A malicious document hid prompt-injection instructions behind a white rectangle; uploading it to Copilot executed arbitrary Python in its sandbox 9:51
• Gzip-compressed commands with a "benchmark" cover story bypassed Copilot's LLM code review 7:41
• A root-owned but writable entrypoint script enabled root privilege escalation in the sandbox 14:12
• An unauthenticated internal service exposed to the sandbox allowed file writes via directory traversal, confirmed with an AA/BB.AA oracle trick 19:21
• Symlinks, newline injection, and an /etc/ld.so.preload overwrite achieved a sandbox escape with a root shell on the host VM 26:33
• Host internet access enabled a bidirectional attacker-to-Copilot channel—an interactive shell for querying the victim's emails, calendar, and files 30:41
• Five vulnerabilities affecting AKS, Azure Dynamic Sessions, Azure Container Apps, and Copilot earned a CVE and bug bounty from Microsoft 34:25
AI assistants need traditional-grade security: monitor sessions with untrusted input, restrict pod-to-host network access, and hold internal cloud services to external-exposure standards 35:12.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So, hello everyone. Today, I'll show you how we hacked Microsoft AI assistant vulnerability in Azure infrastructure. So, let's say an attacker attacked the system. Usually, the attacker gets an interactive access to the system, for example, an interactive shell. In AI, however, attacks usually only end up in one-time data exfiltration. Up until now, we've successfully demonstrated an interactive shell, an interactive access to an AI assistant. So, what do I mean by an interactive access to an AI assistant? Let's imagine for a moment. Imagine you're John, and it's Friday evening, 5:00 p.m., and you're already planning your weekend. But then, you get an email from that company you're signing a contract with, and they ask you to fill a very, long details, a list of details in some document. N…