Extending Attack Path Management into Okta, GitHub, and Mac Environments
Source: YouTube · SpecterOps · published May 18, 2026 · 50:15
SpecterOps announces new enterprise extensions for BloodHound Enterprise, enabling cross-platform attack path analysis across GitHub, Okta, and Jamf to identify complex privilege escalation vectors 0:08.
Key Takeaways:
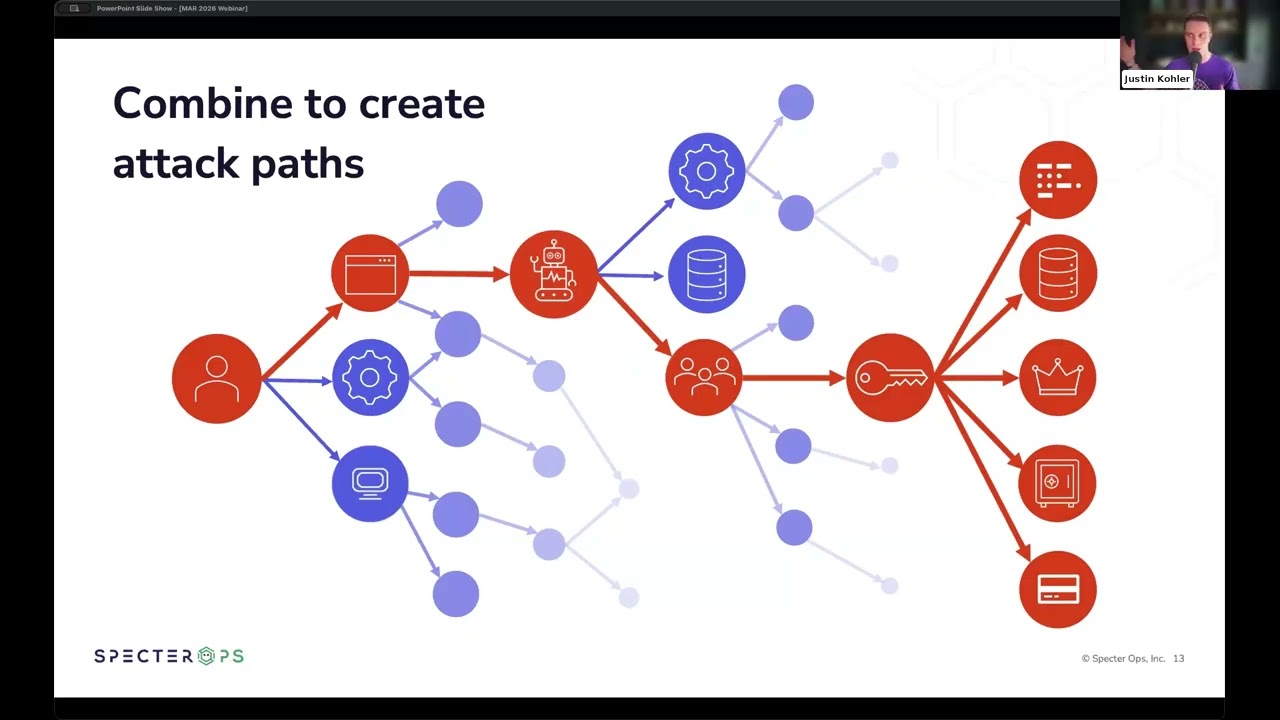
• Justin Kohler (CPO) and Jared Atkinson (CTO) introduce extensions for GitHub, Okta, and Jamf, highlighting the "messy middle" of interconnected identity systems 0:18
• Attackers leverage cross-platform dependencies (e.g., AD to GitHub) to bypass siloed security controls, with 70% of privileged identities often exposed via attack paths 10:23
• New enterprise features include automated findings, remediation tracking, and Environment Targeted Access Control (EAC) to manage risks across multiple environments 35:45
BloodHound Enterprise empowers defenders to visualize and remediate these cross-platform risks before they are exploited, with official collectors releasing in mid-April.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right, Jared, I think we're two minutes after. We could probably get started. Um, >> yep. >> So, uh, we're really excited to talk to you about some new extensions and announcements in Blood Hound Enterprise today. U, my name is Justin Kohler. I'm the chief product officer at Spectre Ops. >> And I'm Jared Atinson. I'm chief technology officer. Maybe a way to distinguish between Justin and I, I'm mostly in charge of our research and development team. And so if you have issues with the graph model or the collector, that's probably in my domain. If you have uh kudos or concerns or thoughts about the actual application and the way that you interact with it, that's uh kind of more in Justin's domain. So just kind of opening ourselves up for uh that feedback, whether it's positive or negative…