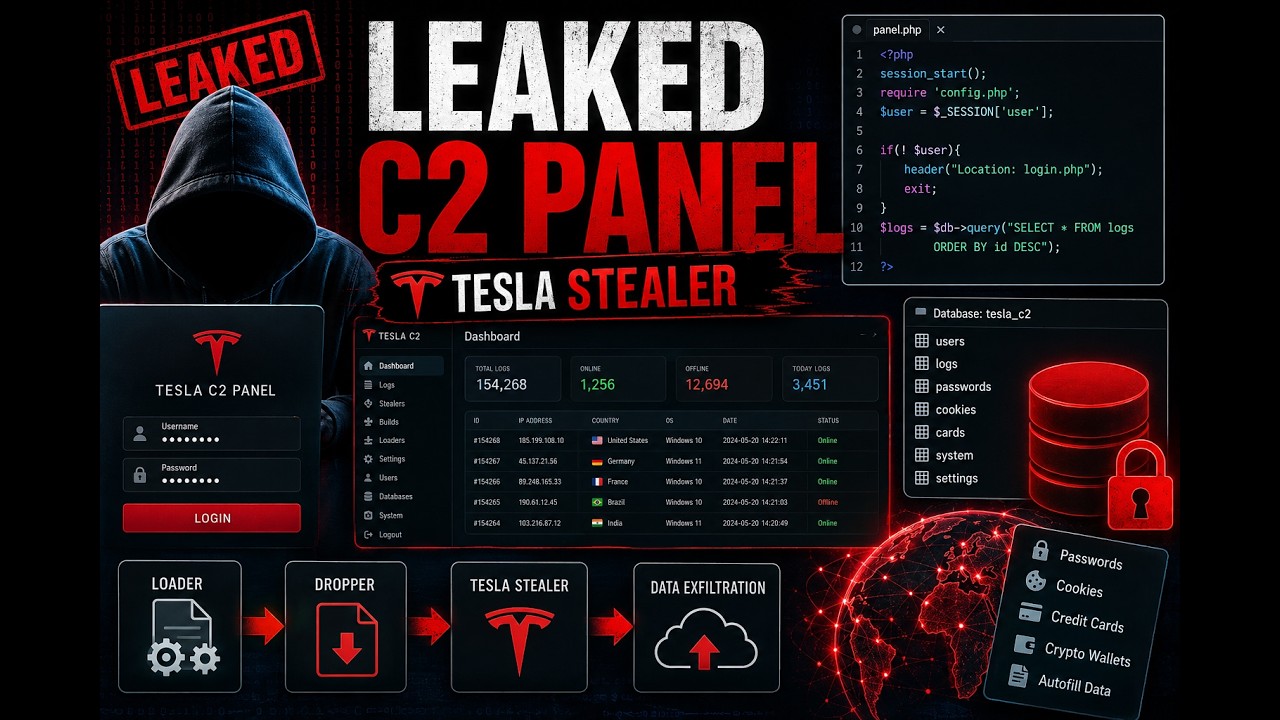
Inside a Tesla Stealer C2 Panel | Reverse Engineering the Malware Ecosystem
Source: YouTube · Malware Research Diary · published Jun 5, 2026 · 1:04:56
A researcher analyzed a publicly accessible, misconfigured Tesla C2 server panel exposed via an open directory, revealing significant data on 98 infected hosts and over 600 stolen credentials 2:15.
Key Takeaways:
• The C2 server was inadvertently exposed through an open directory configuration, allowing unauthorized download of sensitive files 0:30.
• The dataset includes 921 screenshots, 625 stolen credentials, and malware samples including driver ransomware and click fraud tools 0:55.
• The exposure highlights critical security failures in C2 infrastructure management and the risks of accidental data leakage 1:21.
This incident underscores the importance of securing command-and-control infrastructure to prevent large-scale data breaches and credential theft.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Today we're going to take a look at this um C2 um just analyzing some data from a C2 server. So this morning I saw this um user um on Twitter um shared the C2 panel um from Tesla C2. So um basically the C2 was configured with the open directory and allow you know um people to um download pretty much mo a lot of the files in their server. So some um interesting um overview by this user is um there are 98 infected host um 625 stolid credentials and 921 um screenshot um it contain variety of files in there with the um driver ransomware X minor click fix and last dumb right And yeah, here's here's a here's what the screenshot in the post. Pretty pretty cool. So, thanks for sharing. So, I took a look at this and download the files and let's take a look and see what we what they …