From LinkedIn DM to DLL Sideloading | Inside a Fake Job Interview Malware Part 1
Source: YouTube · Malware Research Diary · published Jul 22, 2026 · 1:06:55
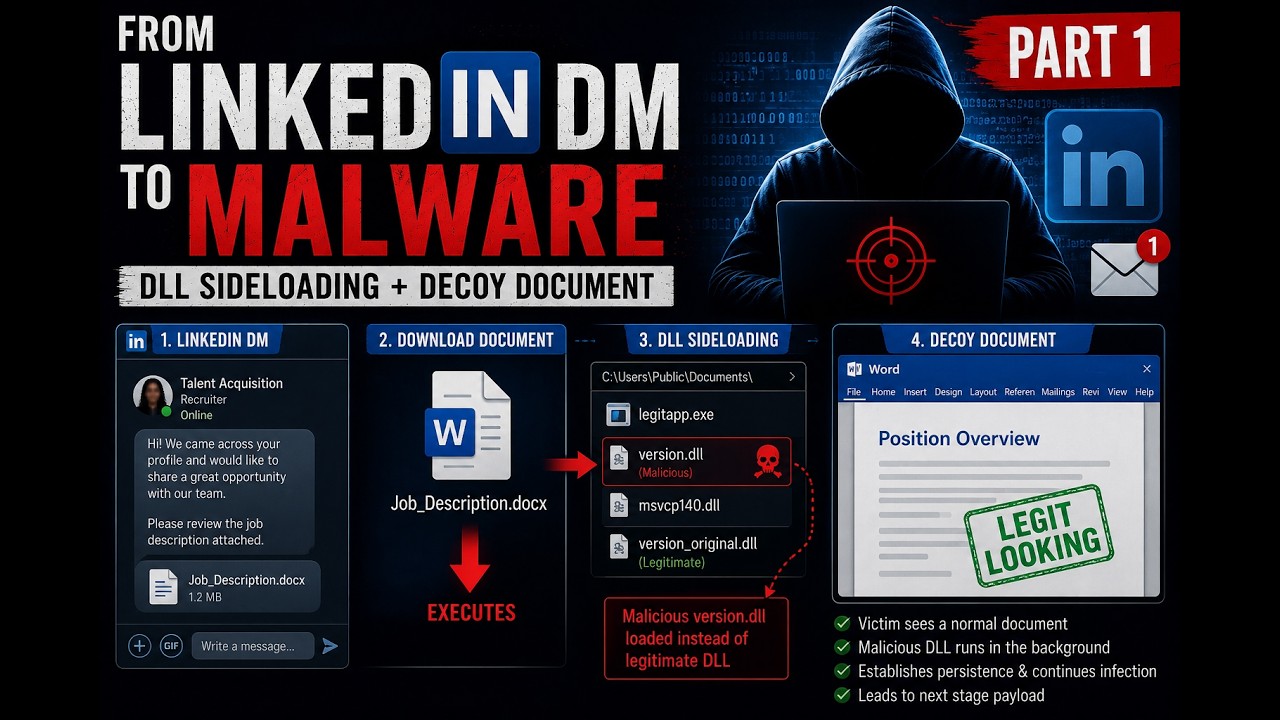
This video analyzes a LinkedIn-targeting phishing campaign that delivers malware through a fake document review site, using DLL side-loading and a Node.js-based second stage 0:09-0:37.
Key Takeaways:
• Victims download an archive containing a legitimate Word document and a malicious DLL that exploits Windows' directory search order to perform DLL side-loading 1:43-3:34
• The DLL modifies the read-only .text section to write-execute, injecting a jump instruction (E9) to redirect execution to the malware's entry point 5:04-7:00
• The malware searches for "decoy" in its binary, extracts an embedded PDF, and displays it for 60 seconds as a distraction 13:00-15:04
• A second-stage Node.js executable embedded in the archive contains WebAssembly and HTTP libraries indicating C2 capabilities 21:16-42:53
• The payload uses a modified Sea packer that hides JavaScript in a non-standard location, evading standard extraction tools 47:05-1:06:21
The analysis is ongoing, with plans to locate and extract the hidden JavaScript payload from the modified Sea packer.
Sources:
- 0:09-0:37 Campaign overview and delivery
- 1:43-3:34 DLL side-loading technique
- 5:04-7:00 Shellcode injection via .text modification
- 13:00-15:04 Decoy PDF extraction and display
- 21:16-42:53 Second-stage Node.js payload
- 47:05-1:06:21 Modified Sea packer analysis
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone, welcome back. Um, today we're going to analyzing a document that might be interesting. Um, so um my connection, network connection on LinkedIn, share me with um a campaign that targeting LinkedIn um user. Um so what happened is they redirect the user into this um website um this um um profile type of like document you know sign up type of activities and they ask the user to go to this URLs to um review the documents and when you review the document they basically download a file um a word documentsish um that look like this. So this the final um um display of the website, right? Where um pretend that there's the it's not a virus um there's no threats detected um is a documents with the word here and it's um encryption and everything. So look really well done, right? Um but …