DEF CON 33 - Real Exploits, Testbed Validation, Policy Gaps in Maritime Connectivity - Juwon Cho
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 24:39
Summary: Maritime Cyber Attack Chain Exploiting VSAT Systems
This presentation demonstrates a real-world maritime cyber attack using VSAT satellite systems to breach ship networks, showing how RCE vulnerabilities can lead to physical damage.
Key Takeaways:
• Modern vessels rely on VSAT communications, yet ACU web interfaces are frequently exposed online with default credentials or unpatched vulnerabilities.
• Researchers used firmware rehosting on QEMU to analyze ACU software without physical hardware, identifying critical RCE flaws in Cobham devices.
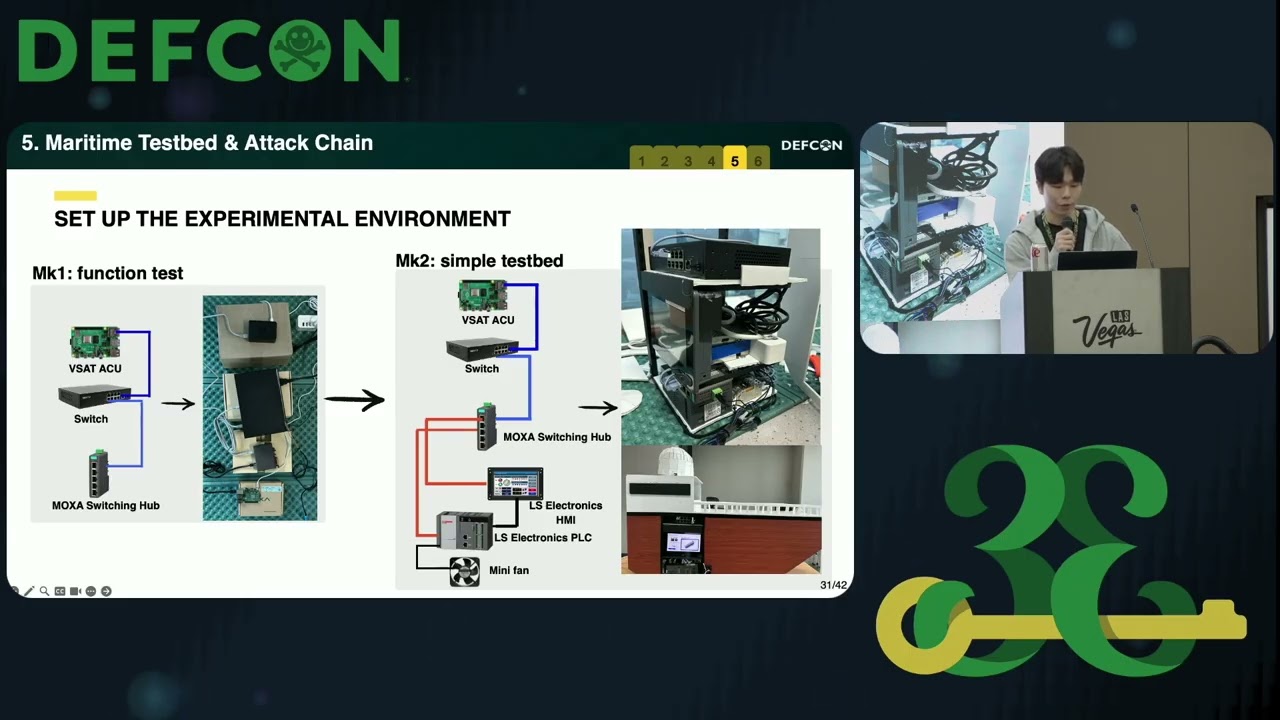
• The attack proof-of-concept involved compromising the VSAT interface, exploiting zero-day vulnerabilities in network switches, and accessing HMI/PLC systems to manipulate propulsion controls.
• A live demonstration showed an attacker gaining root access, navigating the internal network, and forcibly stopping a fan connected to a PLC to simulate physical sabotage.
• Current maritime security regulations focus too much on individual equipment; the industry must adopt system-wide threat modeling to address blurred IT/OT infrastructure lines.
As ships digitize, security requires moving beyond compliance to comprehensive penetration testing.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hi everyone, thanks for waiting around. Now we started. Today we are presenting the boarding the voice set real world exploit um test bed validation and policy gap in runtime connectivity and we are thrilled to be here. Okay, let me kick things off with a recent case. On March 80, 2025, a hacker group called Dr. gun claimed they launched a massive cyber attack against two major iron shipping companies. This incident is considered one of the largest maritime cyber attack paralyzing the communication network at 116 iron vessels. Labagan is an iron anti-government hacking group active since around 2090. In this artic they exploited vulnerabilities in ship's preset to not only disrupt ship-to- ship communications but to completely shut down our external link including port connections. This in…