DEF CON 33 - Crossing the Line: Advanced Techniques to Breach the OT DMZ - Christopher Nourrie
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 17:19
The video demonstrates how OT penetration testers bypass security controls to pivot from IT to operational technology networks using various attack techniques, and provides defensive strategies to prevent such unauthorized access 0:00-0:09.
Key Takeaways:
• Domain admin access in the enterprise network is typically the starting point for OT attacks, making the pivot easier but not always required for success 0:05-0:09
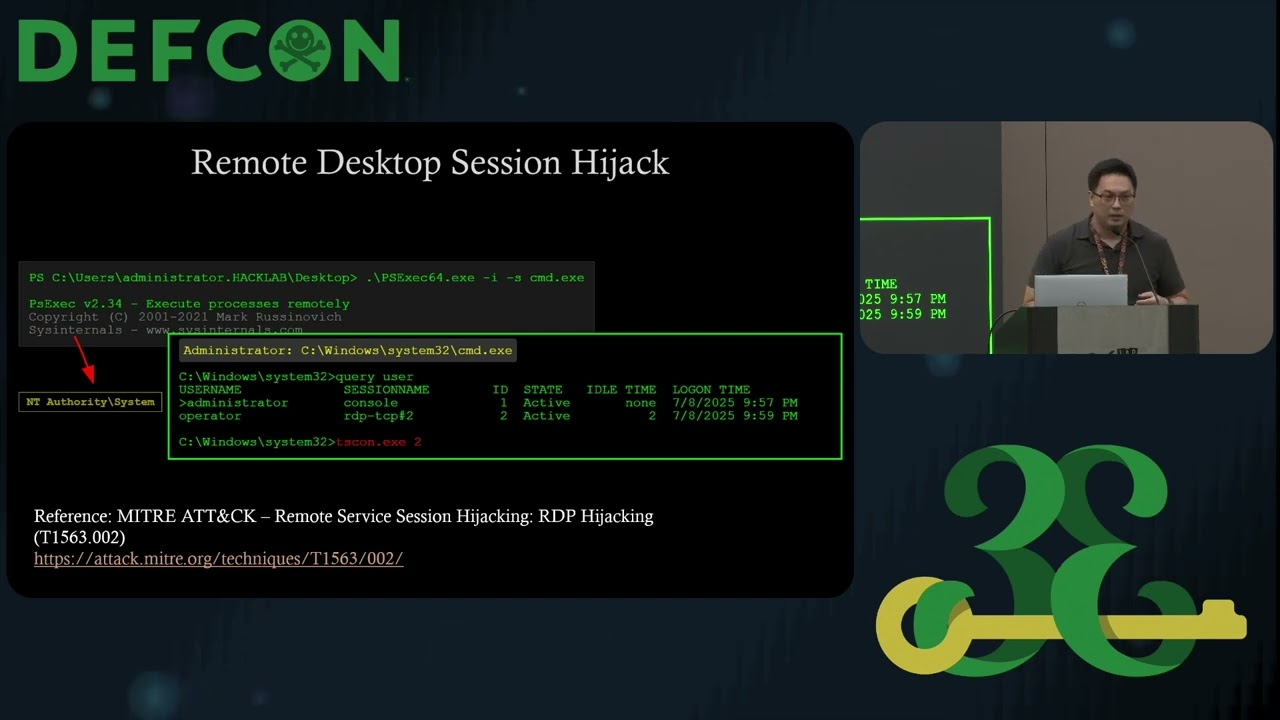
• Remote desktop session hijacking using tscon.exe allows attackers to "bump off" legitimate users and take over their authenticated session, bypassing multifactor authentication 4:30-5:26
• Hidden desktop (HBNC) attacks are particularly stealthy, enabling attackers to view and control a session without the legitimate user's awareness, while bypassing two-factor authentication 7:24-8:31
• Network infrastructure often contains vulnerable paths like implicit firewall rules, SSH access, or BMC devices that can be exploited to bypass the intended remote access controls 8:45-10:11
• Jump servers can be bypassed using alternative services like WinRM or SMB when organizations only secure RDP access but leave other ports open 10:19-11:24
Organizations must implement proper segmentation, multifactor authentication for all services, and enhanced monitoring to detect suspicious activities like tscon.exe or shadow.exe usage 11:30-13:34.
Sources:
- 0:00-0:09 Introduction to OT penetration testing and the value of domain admin access
- 4:30-5:26 Remote desktop session hijacking technique using tscon.exe
- 7:24-8:31 Hidden desktop (HBNC) attack explanation and advantages
- 8:45-10:11 Network infrastructure vulnerabilities and exploitation methods
- 10:19-11:24 Jump server bypass
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
that we leverage as OT pentesters. Um assuming that we compromise the enterprise environment, we get domain admin. Domain admin is not always the the key or um dependent on success. It just makes things easier. So first thing we get domain admin and oh let me go back. Okay, that's thank you. Uh cool. Yes, much better. Uh well I'm actually a little bit ahead. So here's the the remote access architectures. So um just going back slide you have RDP jump servers, you have uh remote access proxy or VPN gateway. So these are the most three common types of remote access. Like I said there could be a jump server in the OTDMZ. Sometimes it's double hopped. But this is kind of key as a OT pen tester to know what type of remote access people are using to get in because that will change our tactic. Oka…