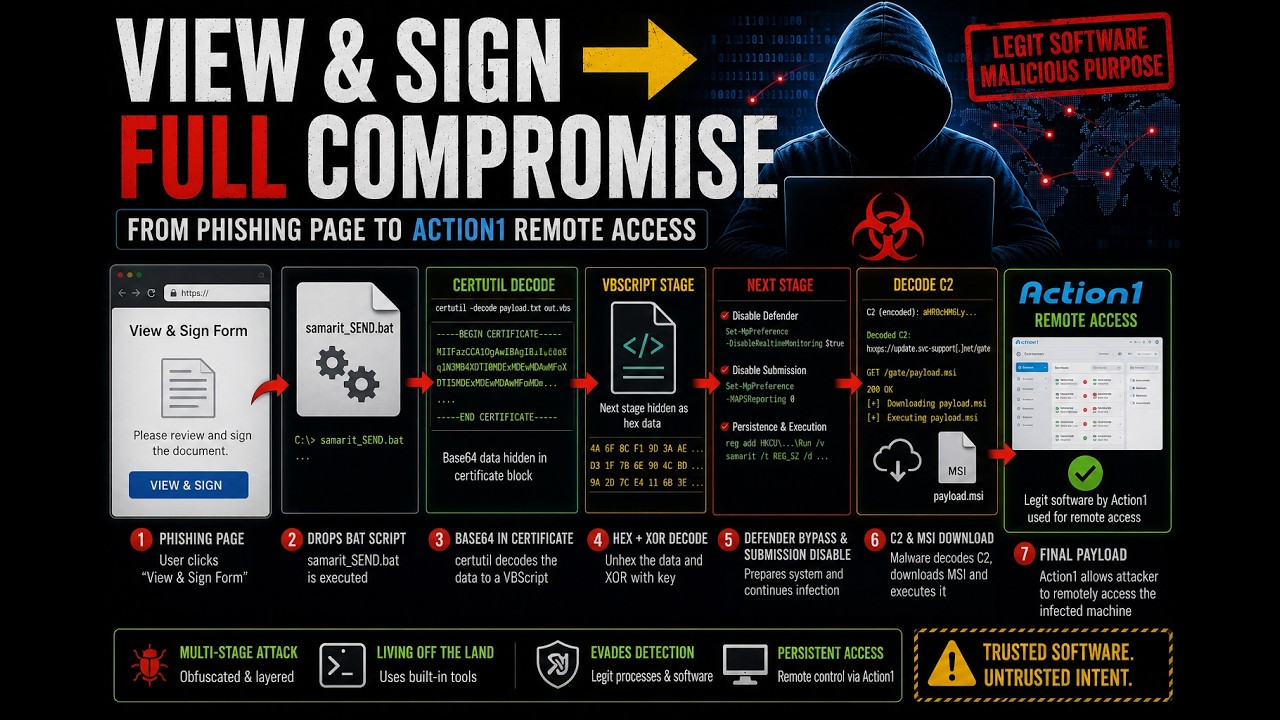
Reverse Engineering a Phishing Chain | From BAT Script to Action1 Remote Access
Source: YouTube · Malware Research Diary · published Jul 20, 2026 · 35:01
The video demonstrates the reverse engineering of a phishing campaign that lures victims with a "view signed documents" theme, ultimately delivering a commercial remote access backdoor through multi-layered obfuscation 0:24-0:31.
Key Takeaways:
• The initial payload uses OS detection to redirect non-Windows users and tracks victims via Telegram 0:36-0:59
• Attackers leverage LOLBins (certutil) to decode base64 embedded within a fake certificate file, bypassing detection mechanisms 2:41-4:44
• The decoded VBScript gathers system information (computer name, username, drives) and uses hex XOR decoding (subtract 127) to decrypt the next stage 9:46-11:15
• Obfuscation is enhanced by using a unique decryption key for every string, requiring analysts to translate VBScript algorithms to Python for efficient decoding 20:51-21:24
• The final payload is a legitimately signed MSI from "Action 1 Corporation," a commercial remote access tool similar to Screen Connect, with an active C2 server identified 30:43-32:07
• The malware establishes persistence via the registry and disables Microsoft Defender's sample submission consent 14:47-14:59
The analysis highlights how threat actors abuse legitimate signed commercial software as backdoors while employing per-string key obfuscation to complicate reverse engineering efforts 34:01-34:38.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back. Um it's been a while. So um today we're just going to take a quick look at a variety of different things. Maybe do some um huntings on um on AppAnnie. But I recently, yesterday, found this site um on URLScan and I thought it might be interesting to take a look. What triggered this is um some type of um service phishing type with the viewing sign form. Um Okay, so the script they got the OS detection device. So some type anti-um view here. Um if it's not window or desktop, then it's going to redirect to the view and I think this is what we're seeing. Um they're also tracking um through Telegram. Right? But what triggered um is this guy. So they're hosting with the um samarit.send.bat. So let's take a look. So because this is target on window um machine, um I'm …