DEF CON 33 - How malicious packages on npm bypass existing security tools - Paul McCarty
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 32:41
Open source malware is increasingly targeting npm packages and JavaScript dependencies, exploiting security gaps in developer tools and CI/CD pipelines, while traditional security tools fail to detect these threats effectively 1:54-1:57.
Key Takeaways:
• 98.5% of malicious packages exist in npm due to its inherent design flaws, lack of security controls, and JavaScript's "no batteries included" philosophy creating massive dependency chains 9:24-9:27, 4:08-4:36, 10:31-10:43.
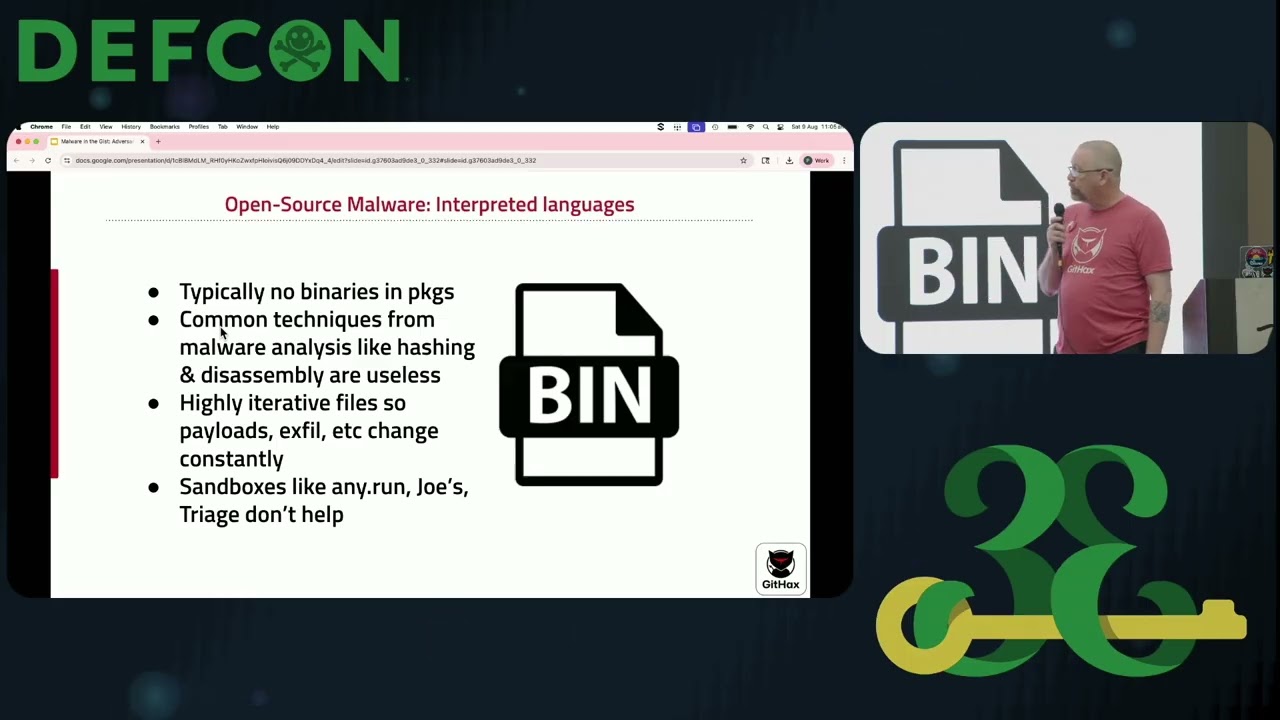
• Open source malware evades detection through code obfuscation, rapid iteration, and operating as interpreted JavaScript rather than binaries, making traditional security tools ineffective 11:18-11:47, 12:12-13:13, 13:39-14:36.
• Attackers target developers and CI/CD pipelines where security monitoring is limited, using techniques like dependency confusion, typo-squatting, and self-removing malicious packages to evade detection 2:21-2:28, 22:16-22:43, 20:28-21:43.
Organizations need specialized solutions like package firewalls and expertise to address these evolving threats that traditional security tools miss 31:26-31:47.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
My name is Paul McCarti. Um I am um currently the head of safety, sorry, head of research at Safety. Safety is a small supply chain um security company based in Vancouver. That's not why I'm here though. I'm here to talk about um open source mailware and why uh it's invading our security toolings. I have worked for a lot of large organizations. I've worked for a lot of startups and the problem is the same for both of those sizes regardless um just a different scale. Um so I like to write I like to write a lot of open source tools. I'm a very prolific um uh yeah anyhow I do a lot of open source stuff. So the stuff on the left is all my tooling. These are things I've written. Um I'm actually really super excited about Gimme Pats. super confused. And um Malice, I haven't even dropped Malice y…