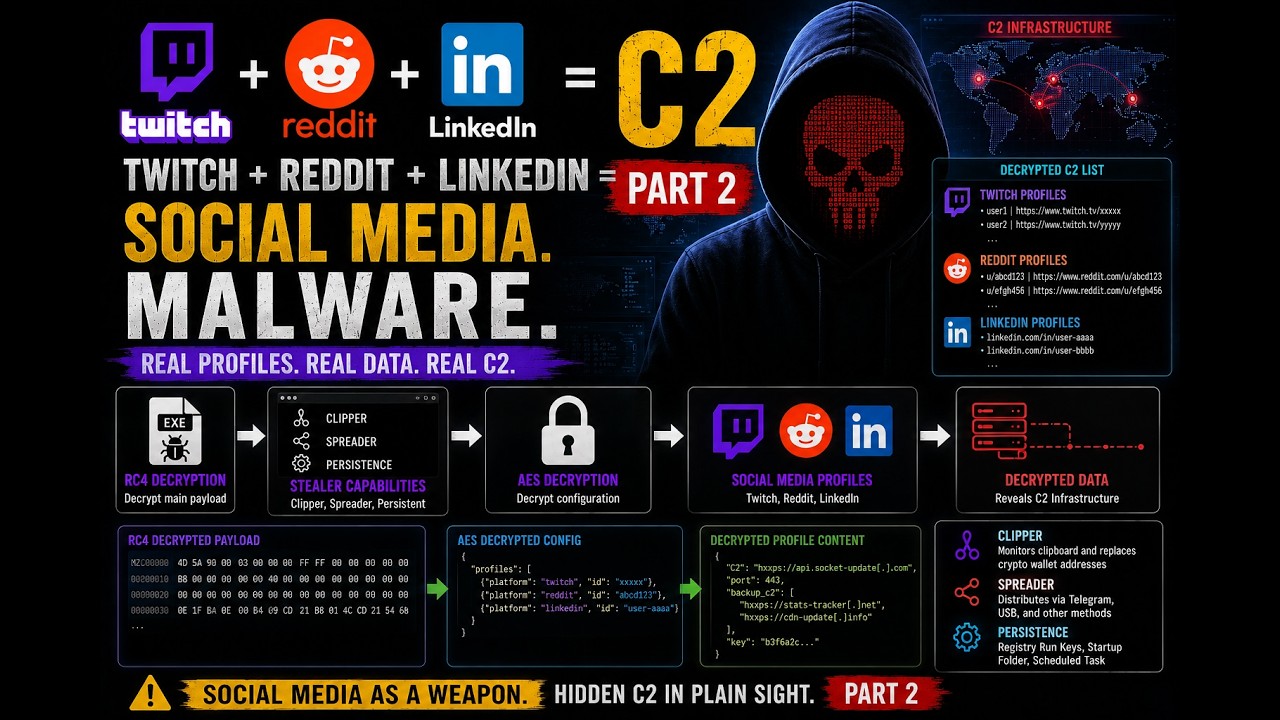
Reverse Engineering a Social Media Malware | Twitch, Reddit, and LinkedIn as Malware C2? Part 2
Source: YouTube · Malware Research Diary · published Jun 19, 2026 · 53:47
The video analyzes a malware sample that downloads a payload from GitHub and embeds a runner DLL within its resources to execute malicious modules 0:22.
Key Takeaways:
• Initial analysis on VirusTotal revealed the malware downloads a payload from GitHub 0:28.
• The malware embeds a runner DLL in its resources, which acts as a plugin to run various malicious modules 0:41.
• The embedded executable is extracted and analyzed in IDA Pro to identify standard loader functions 0:50.
This breakdown highlights the malware's use of resource embedding and external downloads to facilitate its execution chain.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello, welcome back to the second day for analyzing this um interesting malware. Um so just to to recap um we have um initially a mware we saw on v total it seemed to be interesting and when we um noticed that it download a payload from GitHub and after reviewing the code um we noticed that they embedded one of the sample or or not sample but one of the data um executable in the resource. So as you've seen here once we um extract this and open it in DN Spice this is what we have which is a seem to be a runner um a runner DL which is a um a plug-in um for the malware. So they using um some standard loader right to to load it up and here's as you seen the plugin contain um different module um to run the malware and one of the function um standard function that we seen is the run um function.…