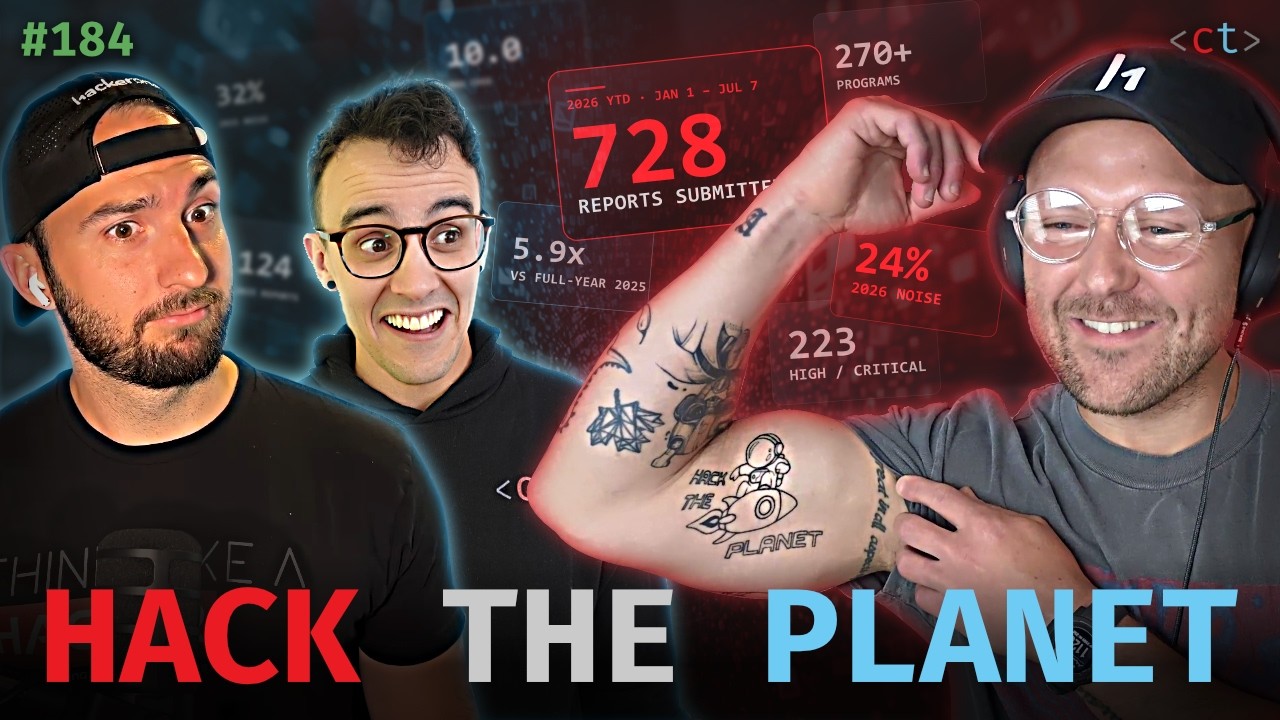
Ads Dawson - 750+ Bugs in 2026 - Destroying Hackbot Era (Ep. 184)
Source: YouTube · Critical Thinking - Bug Bounty Podcast · published Jul 23, 2026 · 1:13:16
BLUF:
Hacker Ads Dawson demonstrates how to build a high-volume bug hunting system using open-source models and modular skills, achieving an 80% reduction in report noise and submitting over 700 vulnerabilities in half a year 11:34. The discussion highlights that durable advantage in AI-assisted hacking comes from custom harnesses and verifier designs rather than just model capability 29:53.
Key Takeaways:
- Open Source Efficacy: Dawson successfully uses smaller, open-source models combined with strong orchestrating harnesses to find critical bugs, arguing that the "B student" models are improving rapidly and reducing the need for expensive frontier models 17:35.
- Modular Skills & Feedback Loops: By creating ~65 specific skills and using a "reflection" tool where a secondary model assesses confidence, Dawson significantly reduced false positives and noise, turning raw AI output into high-quality reports 53:20.
- Report Automation: Approximately 80% of his bug reports are AI-generated, but he uses program-specific rubrics and verifier loops to ensure quality, noting that Meta even integrated his automation tool (FBDL) to offer bounty bonuses for standardized reporting 37:11.
- Targeting Strategy: Instead of spraying across many targets, he focuses intensely on one program for a few days to build context and expertise, leveraging new scope unlocks to maintain high signal-to-noise ratios 06:47.
- Cost vs. ROI: While running his system costs thousands in API fees, the return on investment is massive compared to subsidized subscriptions, proving that custom-built, scalable harnesses are the future of competitive bug bounty hunting 20:39.
Closing Statement:
The episode underscores a shift in bug bounty hunting from manual exploitation to system engineering, where the researcher's primary value lies in building robust, self-improving AI agents. As models become more competent, the competitive edge will increasingly belong to those who can effectively design the verification and feedback layers around them.
Sources:
- 11:34 Discussion of Ads' massive submission velocity and vulnerability count in 2026.
- 17:35 Analysis of using open-source models versus frontier models for hacking.
- 29:53 Explanation of the "researcher builder loop" and durable advantage.
- 37:11 Details on AI-generated reports and Meta's integration of his tool.
- 53:20 Breakdown of modular skills and confidence assessment mechanisms.
- 20:39 Cost analysis of running the hackbot infrastructure.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
his hackbot I think is um like skillfully built with like a bunch of like smaller models or [laughter] or open source models. What? >> Screw you, Reszo. Screw Rezo's like, "Yeah, Justin. You know, the reason you don't feel it is because uh you're bad." [music] >> Best part of when you can just, you know, critical think, right? [music] Yeah, [gasps] dude. [music] [clears throat] I'm not sure y'all know this, but two of the most respected hackers in the CTPB community, Bus Factor and XSS Doctor, are now running monthly hackalongs on the CTB Discord. Okay, you've got to check this out. ctbb.show/ show/isord. We find bugs almost every time we hack. It's crazy. And and oftentimes it's not even the people running the hackalongs. It's the the community members that are hacking along with us. It y…