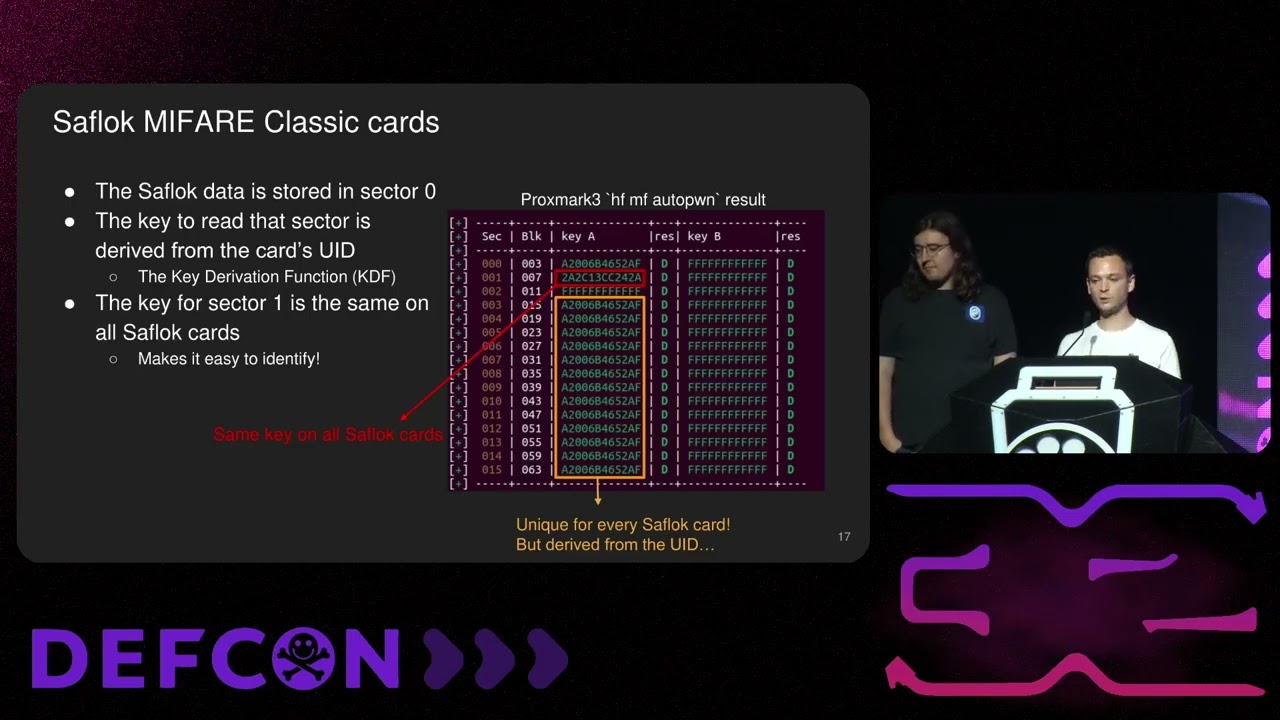
DEF CON 32 - Unsaflok: Hacking millions of hotel locks - Lennert Wouters, Ian Carroll
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 41:32
[BLUF: A vulnerability in Dorma Caba Saf Lock hotel door systems allows attackers to clone and resequence locks, enabling access to any room in a property using just one stolen card, with the attack exploiting weak encryption and hardcoded keys.]2:43
Key Takeaways:
• Saf Lock systems use a hardcoded substitution cipher for card encryption, shared across all properties, making decryption trivial 12:03.
• Attackers can resequence a lock using a forged resequencing card, invalidating previous guest keys and granting access to all doors in the property 17:00.
• The vulnerability stems from weak key derivation and lack of unique per-property encryption, with the system being vulnerable since 1988 27:41.
• A new enhanced security mode uses AES encryption and Myer Ultralight C cards, with secure elements in new encoders to mitigate risks 22:47.
The attack highlights long-standing security flaws in legacy hotel lock systems, now being addressed through firmware updates and hardware upgrades, though adoption remains slow due to integration complexity and cost 33:55.
Sources:
- 2:43 Discussion of the vulnerability’s core and initial motivation.
- 12:03 Explanation of the shared substitution cipher and its implications.
- 17:00 Description of the resequencing attack and its effectiveness.
- 22:47 Details on the enhanced security mode and improved encryption.
- [33:55](https://www.youtube.com/watch?v=4cx0RUV7i0s&t=2
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
[Applause] thanks everyone uh Welcome to our talk titled unsa loock unlocking millions of Hotel locks I'm Leonard I'm a Hardware security researcher at the K Loven University in Belgium I typically do research related to um voltage glitching and other Hardware attacks uh I'm Ian I'm a application security researcher uh I was formerly at the red team at Robin Hood and now I run a point search engine called C uh we got sued by our Canada so as you can probably tell from the first slide neither of us is really working on locks or RFID stuff all of the time so when we started working on this it was all relatively new to us and the reason we started looking at these locks is that a group of us got invited to hack some Las Vegas hotels back in 2022 and they were running a bug Bounty program and …