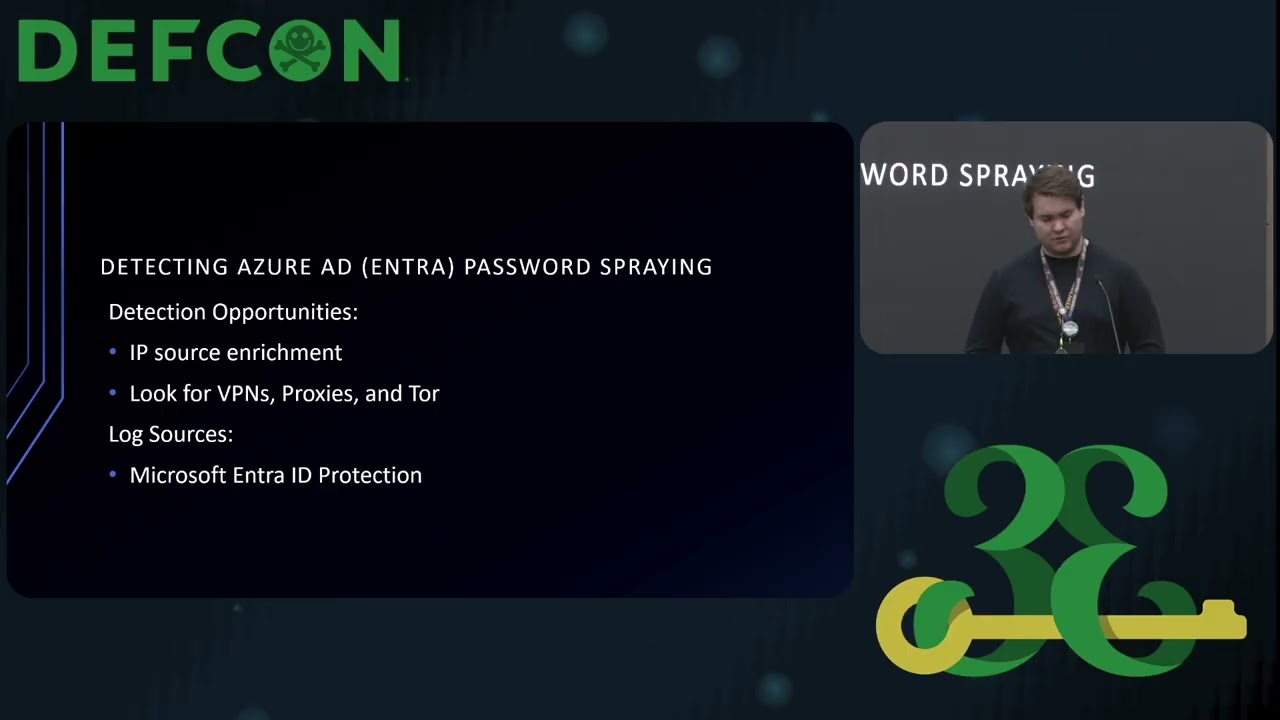
DEF CON 33 - Red Russians: How Russian APT groups follow offensive security research - Will Thomas
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 24:19
Based on the transcript and feedback indicating the original summary "failed," here's a significantly revised version that more accurately captures the core message, evidence, and urgency of the talk:
Summary: Russian intelligence services (GRU, SVR, FSB) systematically monitor public offensive security research and rapidly weaponize red team techniques—often within days or weeks of release—for espionage campaigns. This predictable pattern enables defenders to proactively build and deploy detections based on newly published research before adversaries weaponize it. Offensive researchers must provide defensive guidance alongside tool releases to mitigate exploitation.
Key Evidence & Examples:
(Directly from the transcript)
• M365 Device Code Phishing (SVR): Weaponized within months of Black Hills' 2023 public disclosure. Detected via /device login monitoring in web proxies/email logs (e.g., "WhatsApp" lures targeting governments/NGOs).
• RDP Config Phishing (GRU): Exploited in 2024 after Black Hills' February 2022 research. Detected via RDP attachments in email gateway/Windows event logs (targeted Ukrainian/UK/US entities).
• Team City Exploit (SVR): Operationalized within one week of Rapid7's public release in October 2023. Detected via suspicious commands (e.g., wget, cloudflare.com requests) on Team City servers.
• HTML Smuggling (FSB): Used in 2021 campaigns, despite public red team detailing since 2018. Detected via ISO mounting by explorer.exe and Adobe Acrobat DLL sideloading.
• ClickFix (GRU): Deployed rapidly after John Hammond's GitHub release in September 2024. Detected via PowerShell script block analysis and clipboard monitoring.
• Microsoft Teams Phishing (SVR): Exploited immediately after feature announcement. Mitigation: Disable external Teams access.
Critical Insights:
• Speed Spectrum: Weaponization ranges from 48 hours (Team City/ClickFix) to **yea
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Great. Right now we're off to the start finally. I thought I wasn't going to give a Defcon talk then for a bit. Right. Cool. Okay. Right. So we're uh going to get started now as because we're behind in time. Um so my talk today is some research that I've done over the last three or four years. I used to work at a large company uh with a global presence and based on some of the assets and facilities that they owned the sort of Russian AP groups were a bit of a were a large focus of my research in that time. So that's the bas basis of the talk. So it's about red Russians how Russian AP groups are following red team research which was a trend I identified when tracking these threat groups. So a little bit about me. Um so I'm a senior threat intelligence adviser with team Camry which is a sort…