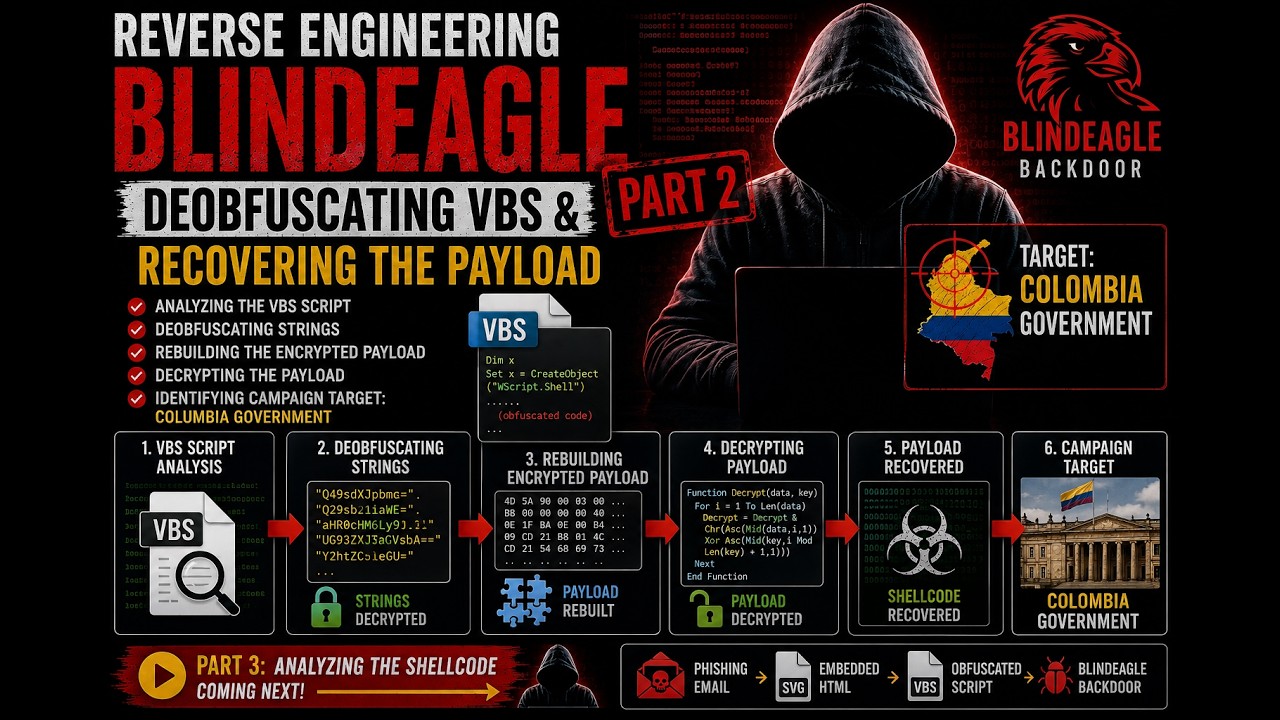
Hunting BlindEagle | Deobfuscating VBS & Recovering the Shellcode Part 2
Source: YouTube · Malware Research Diary · published Aug 17, 2026 · 1:09:34
This video walks through reverse engineering a multi-layered malware dropper targeting organizations in Colombia, showing how the analyst deobfuscates VBS and PowerShell scripts to reveal AES-encrypted payloads. 0:30
Key Takeaways:
• The VBScript dropper uses string obfuscation and junk conditional logic to build a decryption routine, so analysts must understand code structure rather than rely on specific tools. 1:15
• Strings are split across multiple variables and executed via dynamically constructed PowerShell, complicating static analysis. 5:20
• The analyst identifies AES in ECB mode with PKCS7 padding, then locates the key and IV to decrypt each layer. 12:00
• A fake notification image targeting the Republic of Colombia distracts users while the malware runs in the background. 33:30
• Each layer decrypts the next via Base64 or custom encoding, ending in a final shellcode loader to be analyzed in a future video. 42:00
The analysis underscores the flexibility and patience needed as malware authors constantly evolve techniques to evade detection.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to the second part of the video. Um let's keep going um since the last time we look into this. Um so just just for a quick um overview um we was hunting on any run. Um and we was identified for look into one of the campaign of malware targeting some organization. I think is South America likely. Um and we work through the decryption of of the um the drop point, right? So how the malware basically um extract out the payload from here and generating the final um malware, right, which is a VB um VBS um or VB script um dropper. So that's where we at. So let's keep going. So here's the file. Um from here you see what is this 34 generate 34. So is this is I believe this is a um a comment right here. So the s is a comment. So they building some type of strings. Um so …