Flipping Locks - Remote Badge Cloning with the Flipper Zero and More - Langston Clements & Dan Goga
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 37:02
RFID Badge Cloning: Evolution and Modern Techniques
BLUF: RFID badge cloning has become significantly more accessible with tools like Flipper Zero, enabling security testers to bypass physical access controls through various covert methods that exploit vulnerabilities in both low and high-frequency badge systems.
Key Takeaways:
- RFID badges use either low frequency (125kHz, less secure) or high frequency (13.56MHz, more secure) protocols, both vulnerable to cloning with proper tools
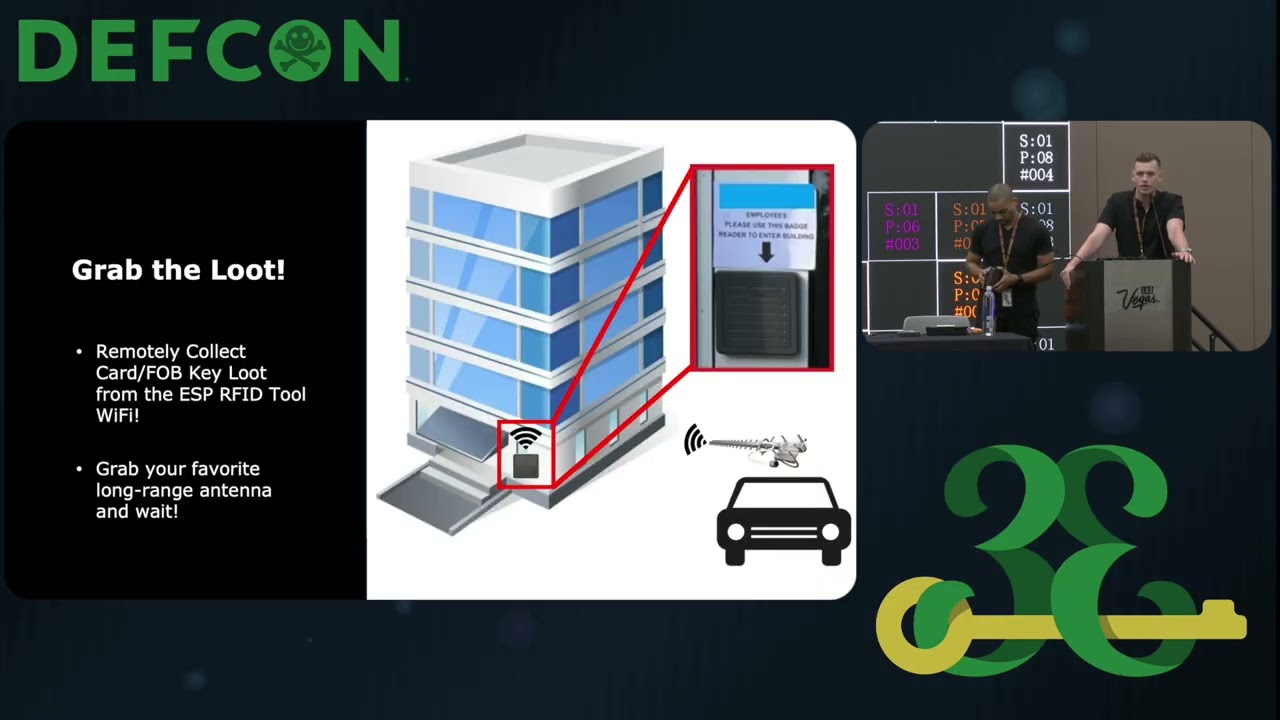
- ESP RFID tool enables creation of covert badge readers that can be deployed as wall implants or clipboard cloners to capture credentials remotely
- Long-range "gooseneck" readers disguised as parking pedestals can capture badge data from up to 3 feet away without user interaction
- Binary data from captured badges must be converted to hex format to work with Flipper Zero, which can then emulate or write cloned credentials to blank cards
- Multiclass readers are particularly vulnerable to downgrade attacks where high-frequency encrypted data can be cloned onto low-frequency unencrypted cards
- Real-world testing demonstrates how these techniques allow unauthorized access to secure facilities, often enhanced by simple social engineering tactics
The presentation concludes with real-world stories demonstrating how these techniques allow security testers to gain unauthorized access to secure facilities, emphasizing the importance of proper security measures to prevent such attacks.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Penetration Testing. Commonly maps to: Security Assessment and Testing, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Well, thank you all for coming. That was an amazing line. We really appreciate it. Uh, and I'm glad you all are the the last survivors of that line. Uh, I'm Langston Clement. Uh, I've been in the industry of red teaming, pentesting for over 15 years. Uh, and had the pleasure of working with this guy, uh, for seven of those years, uh, doing red teaming and we were lucky enough to do a lot of physical engagements. Uh, so we're very excited to share some of these techniques with you. >> Hi everyone, my name is Dan Goa. I've been working with Langston for the past six years doing all types of penetration tests and physical red teams. So, um this is this presentation is a culmination of of our experiences over the past few years and how it's been changing and it really changed a lot with the fl…