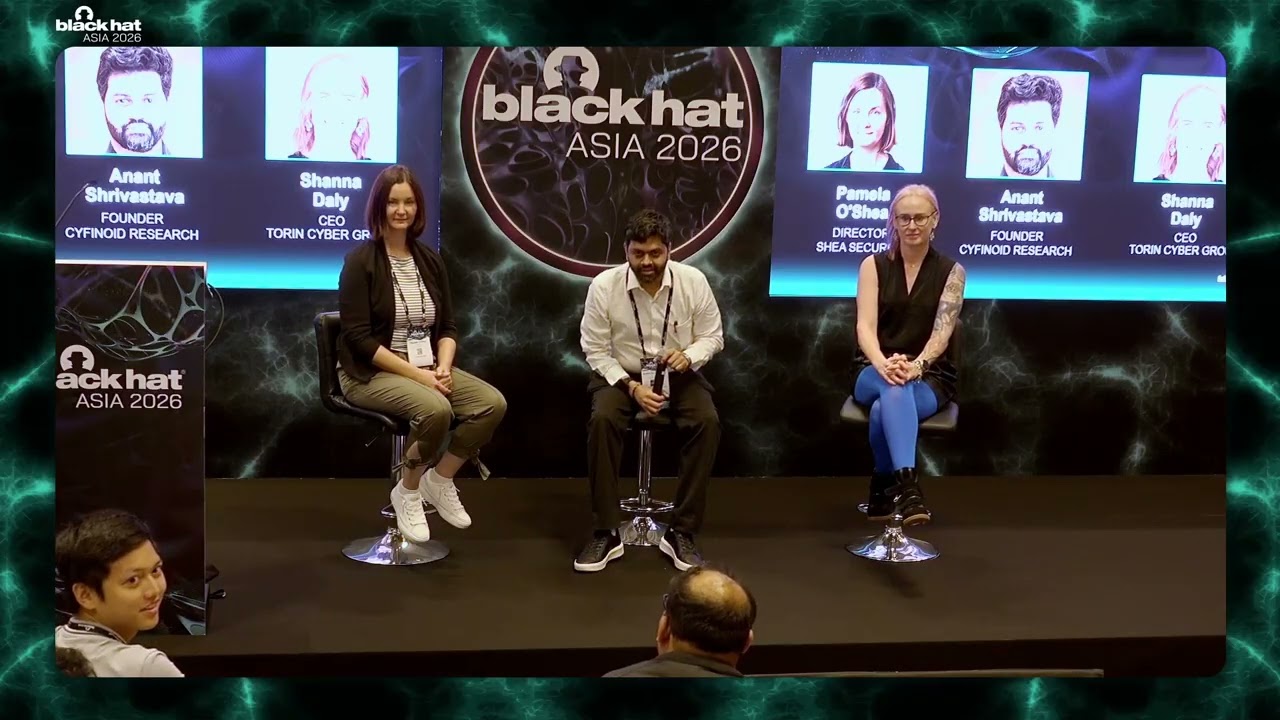
Black Hat Asia 2026 | Mobile Track Spotlight
Source: YouTube · Black Hat · published Sep 3, 2026 · 24:43
A Black Hat mobile track panel of three security practitioners (Anant Shastav, Shana Dailyaly, Pamela O'Shea) answers audience questions on mobile security trends, AI in pentesting, and hardware-backed protection 0:09.
Key Takeaways:
• AI-generated code bloat is a dominant mobile trend; unlike web, mobile apps have hard size limits, forcing teams to claw back code 2:05
• React Native with Hermes is beating PWAs; unified codebases make blackbox reversing hard, so pentesters should request source code 3:29
• AI finds low-hanging fruit fast but fails on undocumented business logic—good documentation makes AI-assisted pentesting effective 5:50
• Hardware security (secure enclaves, StrongBox) is improving via containerization, but implementation flaws persist; mobile radio stacks remain fruitful research targets 8:17
• Assume every mobile app runs in hostile territory—compromise can't be reliably detected, so validate critical logic server-side 9:23
• Mobile flows (payments, facial recognition, varying aspect ratios) resist automation, so human pentesters still add unique value 13:11
Closing advice: threat model mobile apps as more than web apps—they interact with a wireless ecosystem of Bluetooth, GPS, and watches—and match security controls to the asset's value 23:42.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right, good afternoon everyone. Thanks for being here just after lunch. I understand how painful that could be, but all right. So, we're here for the mobile track spotlight. All three of us have been the judges or rather the review board members for the mobile track. So we wanted to have a quick chat with everyone in the audience around mobile security and if there is anything that you wanted to ask about mobile. We're here at black hat. There are offensive questions, there are defensive questions. Not offensive in the sense of offensive but more of offensive security questions. So we wanted to open this stage firstly. So I'll do a quick introduction of all of us and then we'll ask you if you have any burning question we can start with answering that otherwise if there's no other quest…