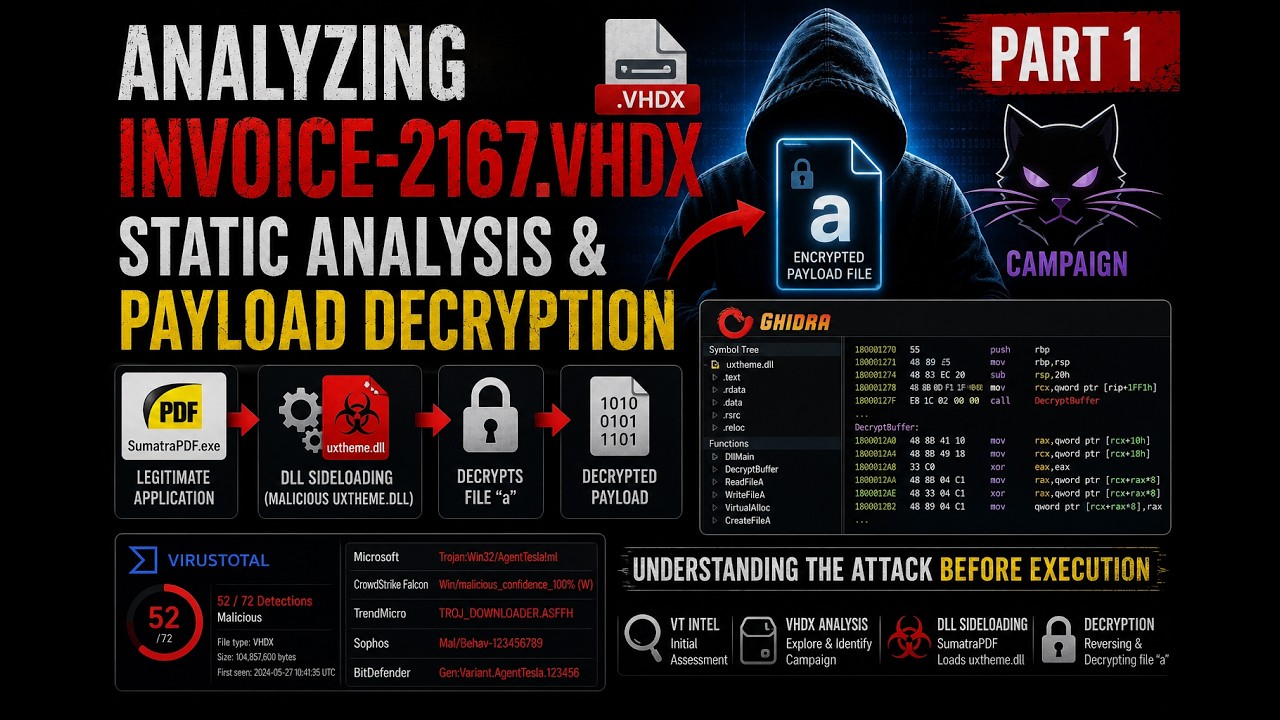
Reverse Engineering Invoice-2167.vhdx | DLL Sideloading & Payload Decryption Part 1
Source: YouTube · Malware Research Diary · published Jul 29, 2026 · 56:12
[BLUF] Analysis of a zero-detection VHDX file reveals a DLL side-loading attack where the signed legitimate executable SumatraPDF.exe loads a malicious uxtheme.dll to evade antivirus detection 0:30.
Key Takeaways:
• The malware is distributed via an ISO/VHDX image containing "invoice.pdf.exe," a masqueraded executable that relies on the legitimate Sumatra PDF signature to bypass static analysis 3:42.
• The attacker utilizes DLL side-loading by placing a malicious uxtheme.dll in the same directory as the legitimate binary, exploiting Windows' library search order 6:42.
• The campaign targets Southeast Asia, specifically Vietnam and Korea, indicating a regional threat actor leveraging social engineering via fake invoices 9:02.
• The malicious DLL dynamically resolves APIs using a custom hash algorithm to avoid static signature detection and hide its functionality from analysts 27:33.
• Inside the DLL, a file named "A" is decrypted using a 6-byte XOR key, revealing shellcode that likely executes further malicious payloads 46:52.
This technique highlights how attackers leverage trusted software signatures and dynamic API resolution to deliver malicious code, making detection difficult without deep behavioral analysis.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Good morning, everyone. Um welcome to another session in hunting for malwares. Um today um we're going to analyzing a file called invoice -2167. um vhdx. Found this yesterday on App Annie, but couldn't find it today. But um looking it through the VirusTotal, um the there's zero detection, right? And um the file is a ISO um Windows image um extension. Um and it was first submitted on the 25th, so a few days ago, pretty brand new. Um let's see. So, from here it's dropping PowerShell, maybe. Let's see the behavior of this. Um nothing stand out um just from the quick look. The script as we see open, okay. Um Yeah, not nothing stand out. So, let's check it out and see what it is. Um actually from the community, um oops. From community, um the detection from Joe Sandbox is one out of 100, so it'…