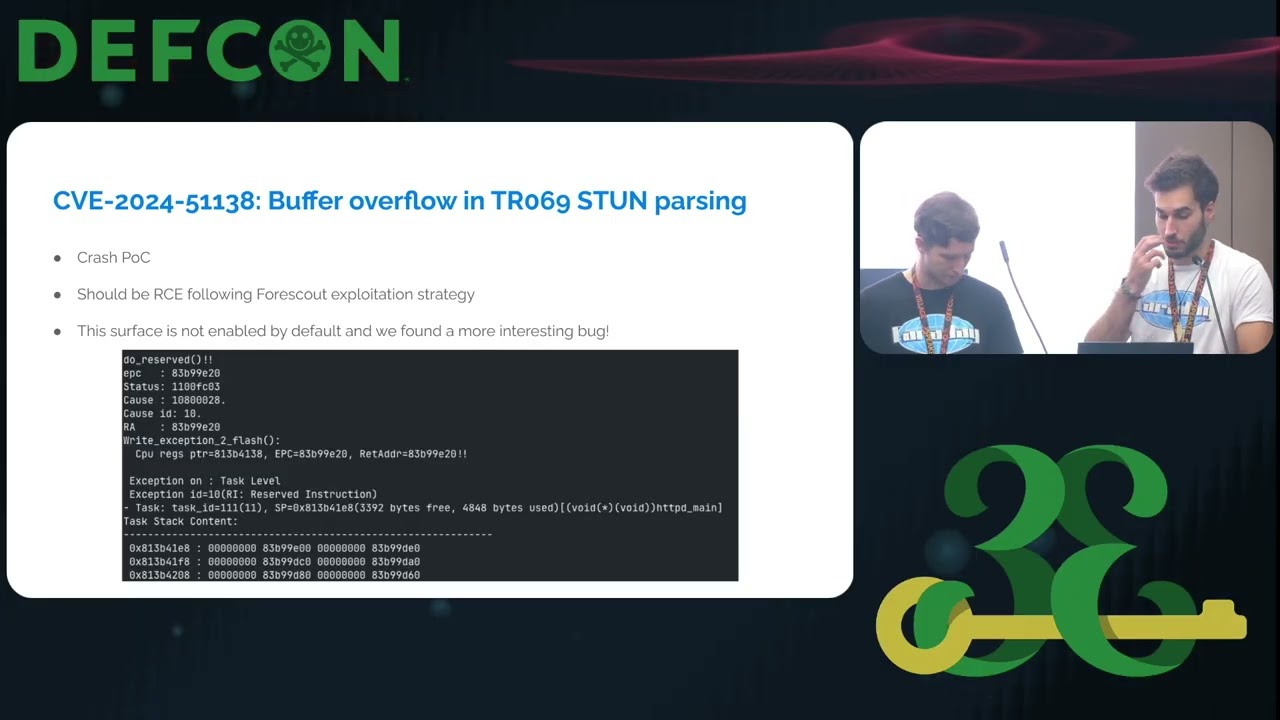
DEF CON 33 - The Missing Link: Draytek’s New RCEs Complete the Chain - O. Gianatiempo & G. Aznarez
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 24:50
[BLUF: Researchers reveal a complete attack chain from internet to persistence on routers via buffer overflows and kernel module manipulation, with vulnerabilities including TR69 and CGI parsing flaws, enabling remote code execution and long-term access.]2:13 3:47 5:01 8:48 12:05 14:23
Key Takeaways:
• A buffer overflow in the TR69 STAND parser allows remote code execution via malformed queries 5:01.
• An integer overflow in CGI parsing leads to heap corruption and arbitrary memory write, enabling code execution 10:51.
• Kernel-level persistence is achieved via modified DLMs (dynamically loadable modules) that survive reboots and firmware updates 16:36.
• The attack chain combines password reset, shellcode injection, and DLM exploitation to achieve silent, persistent access 18:33.
• Router reboots observed in March 2024 may stem from failed exploitation attempts, with silent successes remaining undetected 20:50.
[Closing statement: The research highlights deep vulnerabilities in router firmware, emphasizing the need for users to update firmware and researchers to adopt complementary approaches for comprehensive security analysis.]
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hi. Hello everyone. H welcome to the missing link dry new RCS complete the chain. I am Gastonas Narees and my partner here is Octavo. We are security researchers at at Faraday. We mostly focus on firmware and embedded and low-level stuff. Okay. what we are going to see today. First, we are going to do an introduction and a recapitulation about our previous work and what we are doing now. We are we are going to show new vulnerabilities and with the vulnerabilities that we found now and the old ones we are going to show the full chain exploit from the internet to persistence. We also are going to check the the wave of routers reboots that we saw we saw on March and we are going to give some conclusions and takeaways. Okay, so let's start with the introduction. Yes, it's not our first time wi…