DEF CON 32 - Breaking Boundaries: Popping Shells in the Airgap w $10 & Arduino Magic - Daniel Beard
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 24:19
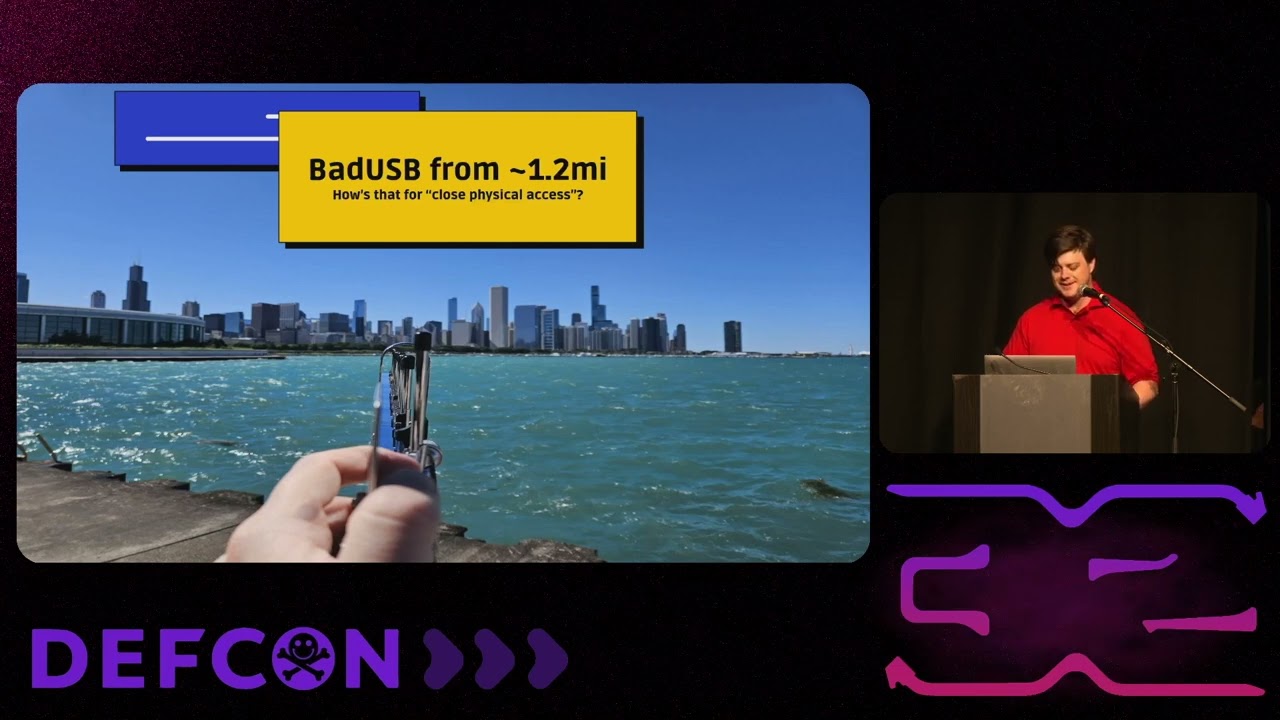
The video demonstrates that bad USB attacks on medical devices are feasible without requiring extended physical access or internet connectivity, using a $10 RadioJack T dongle to gain remote shell access via Wi-Fi or long-range radio (LAURA).
Key Takeaways:
• Bad USB exploits are viable in medical devices with Windows or Linux frontends, requiring only minutes and a few dollars 0:55-1:00.
• The RadioJack T dongle emulates USB devices, drops payloads, and provides a remote PowerShell shell over Wi-Fi or LAURA 2:01-3:47.
• Attacks can operate over distances of up to 1.5 miles using LAURA, enabling remote shell access without direct physical presence 11:00-11:59.
• Devices are vulnerable even with air-gapped networks, as the attack only requires a short physical access window and user login timing 3:30-4:00.
• Mitigations include covering unused USB ports, disabling USB stacks by default, and only enabling them during explicit user actions 12:45-13:30.
This attack highlights critical vulnerabilities in medical device security and underscores the need for stronger physical and software protections.
Sources:
- 0:55 Discussion of medical device architecture and bad USB risks
- 2:01-3:47 Demonstration of RadioJack T functionality and payload delivery
- 11:00-11:59 Proof of concept using LAURA for long-range shell access
- 3:30-4:00 Disproof of extended access requirement and persistence needs
- 12:45-13:30 Recomm
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
all right welcome everyone to popping shells with $10 and a bit of Arduino magic or AKA let's redefine physical access first off who am I I'm Dan beard I'm a software engineer at medcrypt used to direct Med ISO previously CTO of prominade software where we um worked on medical devices as a contractor so worked with a lot of different companies I personally coded on at least 10 different medical devices and collaborated on so many more um mostly in vitro diagnostic instruments so that's like lab equipment um some implantables some therapeutic devices infusion pumps you name it uh the ivd and therapeutic are bolded cuz that's mainly what this attack is going to be against um not so much implantables uh All Views expressed are my own my company is making me say this uh does not reflect the op…