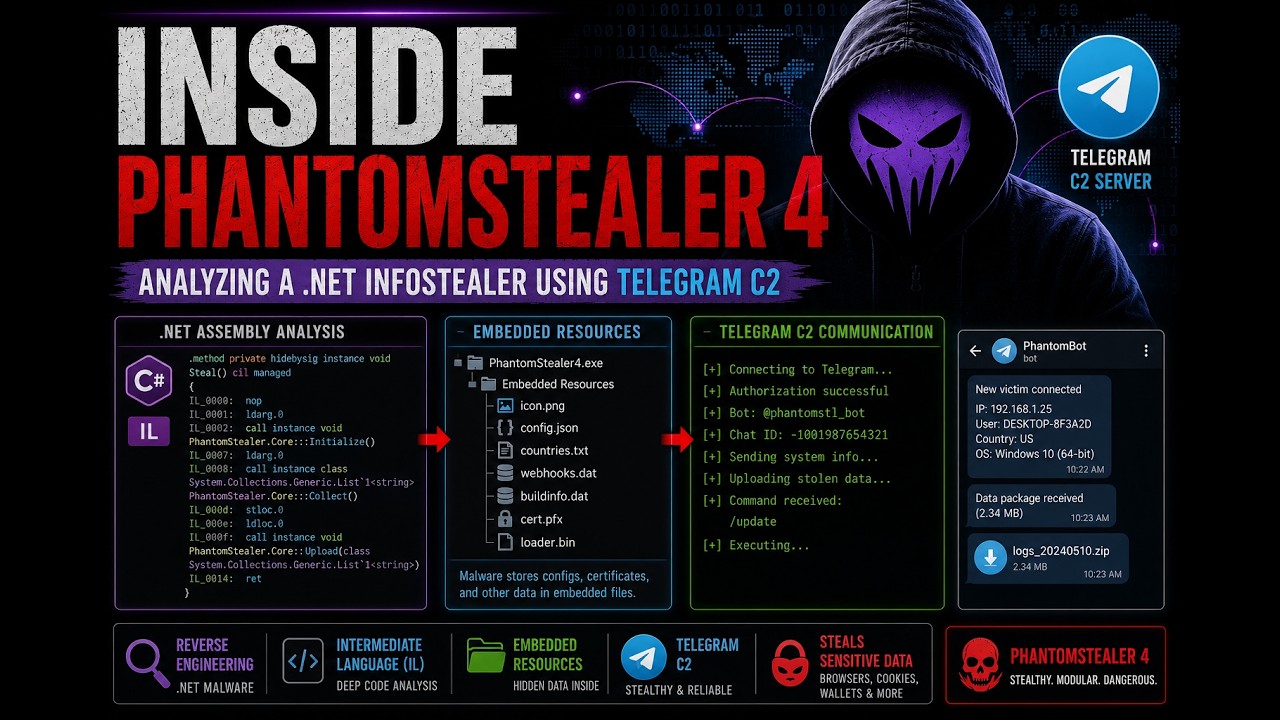
Reverse Engineering PhantomStealer 4 | Inside a NET Infostealer Using Telegram C2
Source: YouTube · Malware Research Diary · published Jul 20, 2026 · 33:27
This video provides a technical reverse engineering analysis of Phantom Stealer version 4, detailing its malicious capabilities including browser credential theft, keylogging, and ransomware functionality 0:50.
Key Takeaways:
• The malware utilizes embedded resources to extract and decrypt browser secrets from Chromium-based browsers like Chrome, Edge, and Brave 2:42.
• It employs extensive anti-analysis techniques, checking for specific usernames, PC names, and sandbox processes to evade detection 11:13.
• Phantom Stealer 4 organizes stolen data into HTML files for exfiltration via Telegram, a notable deviation from standard text-based dumping 17:06.
• The malware includes clipboard monitoring, keylogging, and password recovery features to maximize data theft 16:05.
• While it contains ransomware code using AES encryption, the analysis suggests the decryption keys are not hardcoded, indicating a modular or external dependency for encryption operations 20:01.
• Reverse engineering requires analyzing the intermediate language due to obfuscation, as standard static analysis is hindered by these protections 23:05.
Phantom Stealer remains a significant threat due to its robust feature set and evasion techniques, requiring careful handling in sandbox environments.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to another video. Um, today I'm just gonna I download a few files earlier today. Let's take a look and see if there's anything interesting. So, okay, let's go with the first one is a net files. Okay, so strings dragon. Never seen this before, so this might be something brand new. Um, got some uh using the strings saw some here's a interesting um print out decryptting data. So is this a ransomware and initialize low module find the JSON decoded. Okay. Um let's do bin work. So there's two one embedded files, two embedded files in here. Let's open up VMware [snorts] and refering. So let me actually check once total first. Okay. [snorts] See if there's anything interesting on V total. Generic dumpers. Um browser stealer. Clipper banks dealer telegram so it's sendin…