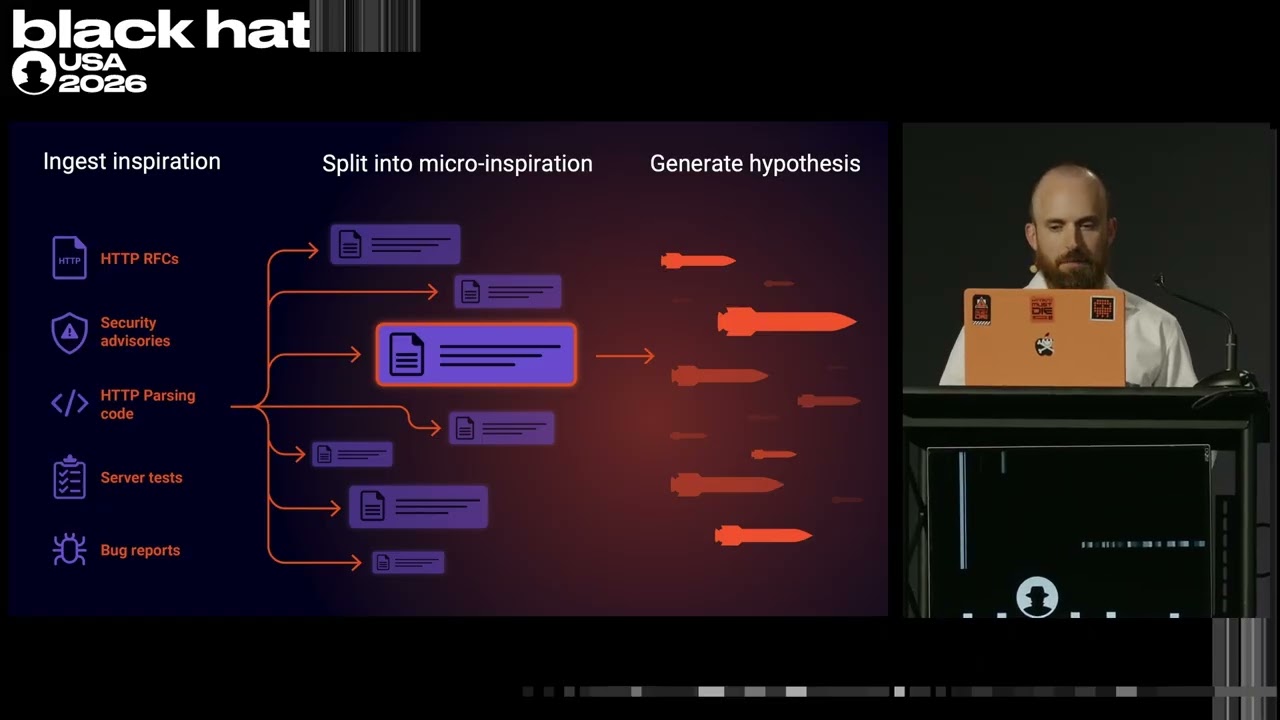
Black Hat USA 2026 | Can AI Do Novel Security Research? Meet the HTTP Terminator
Source: YouTube · Black Hat · published Nov 18, 2026 · 37:36
The speaker built "HTTP Terminator," an autonomous AI that invented novel HTTP desync techniques, exploited live bug bounty sites, and cascaded findings—including a stolen bank API key and a new meta attack class 0:29.
Key Takeaways:
• Four phases: ideation, evaluation on ~30,000 bug bounty sites, weaponization, and cascading discoveries 5:09
• "Micro inspiration"—splitting 138 RFCs into ~15,000 fragments—generated ~30,000 unique desync vectors 9:42
• First major finding (HTTP/1.0 + gzip) caused desyncs widely, exposing an airport's internal staff panels via F5 Big-IP 13:35
• Weaponization improved by controlling the agent's perceived reality (e.g., renaming tools) and moving orchestration/validation to deterministic code 17:56
• Cascades revealed response forking via HTTP/0.9, an Apache Traffic Server zero-day, and "shared parser confusion"—a major new meta attack class 25:00
• Conclusion: AI can do novel autonomous security research, but humans in the loop are a "massive power amplifier" 36:55
Source code and white paper are being published, though the system is a research factory unsafe for commercial use 35:29.
Sources:
- 0:29 Project origin and stolen bank API key
- 5:09 Four-phase system architecture
- 9:42 Micro inspiration generating 30,000 vectors
- 13:35 First gzip desync finding
- 17:56 Fake reality framing and deterministic validation
- 25:00 Cascade discoveries
- 35:29 Open-sourcing tools, commercial warning
- 36:55 Final conclusions
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Penetration Testing. Commonly maps to: Security Assessment and Testing, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Good afternoon and welcome. This talk exists because I had an idea that was so bad, I just had to try it out. I'd seen AI finding vulnerabilities and started to wonder how far I could push it. Could I build a completely unsupervised system that invented original hacking techniques and then applied them for mass compromise of live sites? And then used those hacked sites to discover new techniques and compromise more targets indefinitely? And just how far beyond the state of the art could this system go before it imploded? One morning a few months later, I opened my laptop and I saw that it had a message for me. It had spotted an anomaly. Overnight, it had taken a novel desync technique it had invented itself, discovered it worked on most of the public infrastructure of a particular bank, an…