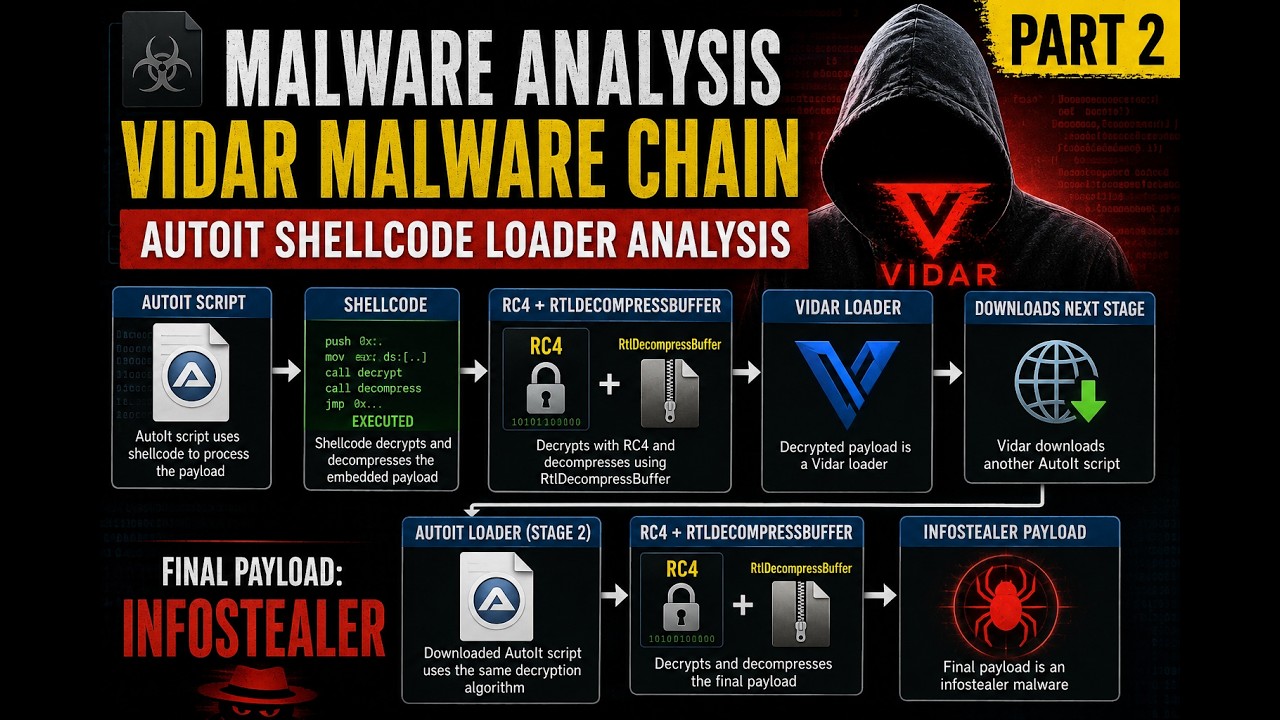
Reverse Engineering a Multi-Stage Vidar Malware Chain | AutoIt Shellcode Loader Analysis – Part 2
Source: YouTube · Malware Research Diary · published May 21, 2026 · 1:08:09
This video continues the analysis of a malware sample delivered through a YouTube channel, focusing on unpacking an AutoIt-based executable hosted on Proton 0:02.
Key Takeaways:
• The malware was initially identified on a YouTube channel and downloaded as an executable file 0:07.
• The malicious payload is hosted on Proton and packaged as a setup executable 0:27.
• Extracting the setup file reveals a hidden AutoIt script designed to run automatically when the malware is executed 0:44.
• As discussed in the previous video, the AutoIt script uses obfuscated strings that must be decoded for full analysis 1:19.
This breakdown highlights the common evasion technique of using AutoIt wrappers and obfuscated strings to hide malicious intent.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello. Hello everyone. Welcome back to the part two of um analyzing um this malares. So just for recap um we um identify the one of the file malares been delivered on YouTube channel and from here we download it and um get to the executable. So another layer here contain the um the malware is hosted on proton. Um and the malware is a executable that is um is a um I express setup file which when we using the um extractional we obtain the um the the auto it um sample. So the the so the malware when it run it would executing the auto it. So the auto it is um a scripting thing that allow user to you know developing interfacing with everything that they wanted. So in the last conversation we saw that um the malware was um offiscate all the strings and we go through the process of decoding the s…