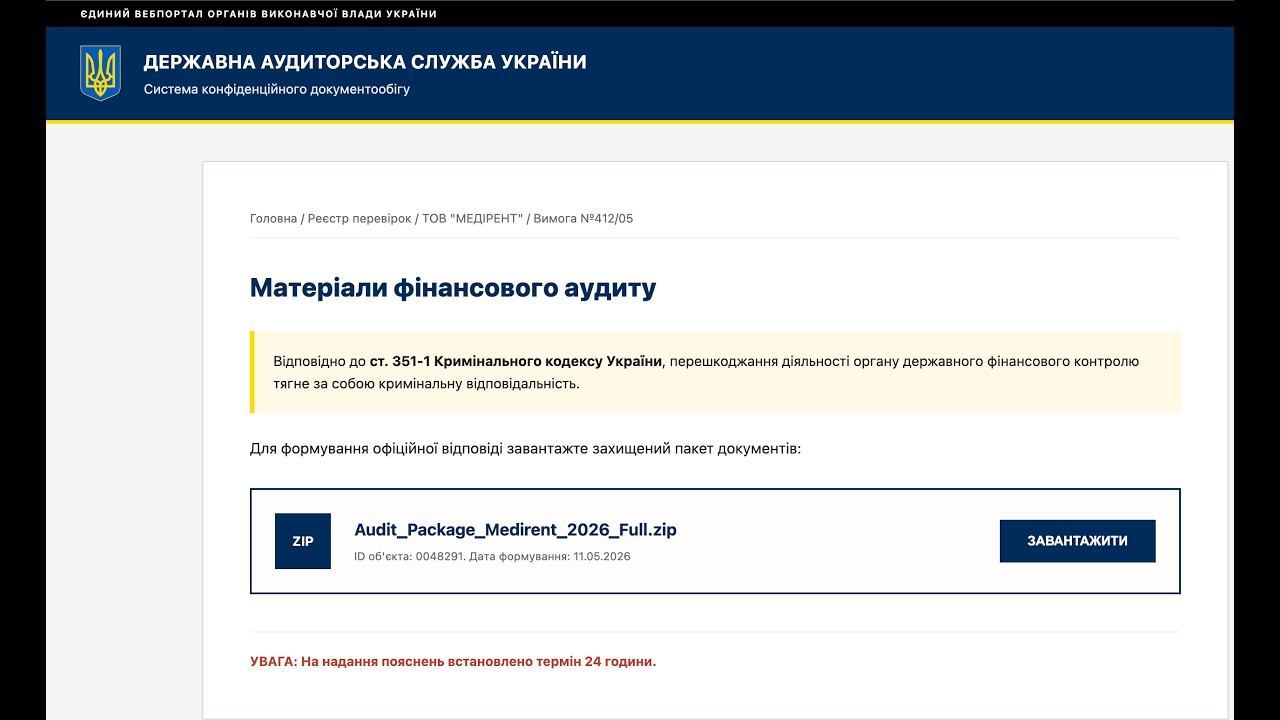
Inside a Golang Malware Campaign Targeting the Ukrainian Government
Source: YouTube · Malware Research Diary · published May 13, 2026 · 26:43
BLUF: A new malware dropper targets Ukrainians via a fake "Unified Web Portal for Security Ukraine" site, using a recently created GitHub account to host the payload 0:15.
Key Takeaways:
• The malware specifically targets Ukrainian users by impersonating a government security portal 0:15.
• The landing page uses Google Translate to disguise the malware's purpose as a legitimate military package download 0:22.
• The malicious payload is hosted on GitHub, leveraging the platform for distribution 0:49.
• The GitHub account used to host the malware was created only three days prior to the detection, indicating a rapid deployment 0:59.
This case highlights the use of social engineering and legitimate platforms like GitHub to distribute targeted malware.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello. Today, we're going to take a quick look into a Go lang malwares. Um I obtained this um website or detected this malware dropper website yesterday. And from what it seemed is um targeted correct Ukrainians. So, let's do a quick Google Translate here. And as uh um using Unified Web Portal for a security Ukraine code of um arms. And they're requesting to downloading a package, which is all the package military um full. So, um when we review the source code of the website, um the payload is hosted on GitHub. And this is um the user that hosts in it, I believe. Yeah, they was um creating that account 3 days ago. So, no other activities, just um uploaded sample from here. So, here's payload for it. Um when the the payload is encrypted with a password, and I believe the password is in here…