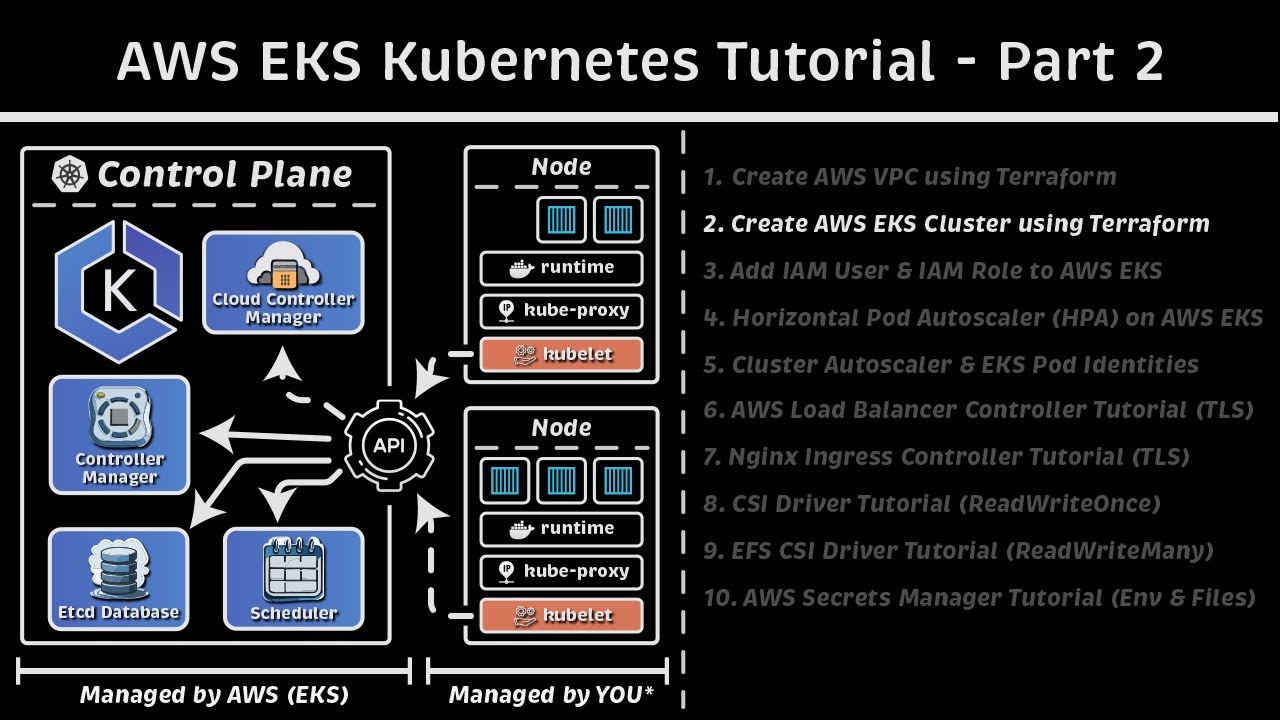
Create AWS EKS Cluster using Terraform: AWS EKS Kubernetes Tutorial - Part 2
Source: YouTube · Anton Putra · published May 20, 2024 · 19:04
This video is the second part of an Amazon EKS tutorial, covering Kubernetes architecture, IAM permissions, and provisioning the control plane and worker nodes using Terraform 0:00-7:46.
Key Takeaways:
• Kubernetes relies on core components like etcd for state storage and the scheduler for assigning pods, while cloud-specific logic is increasingly handled by external controllers like the AWS Load Balancer controller 0:13-1:51.
• EKS requires specific IAM roles and policies, such as AmazonEKSClusterPolicy, which use temporary security tokens to enhance security compared to long-term credentials 3:56-5:04.
• Using Terraform, the tutorial guides users through creating a highly available control plane with a public endpoint but deploying worker nodes in private subnets to minimize security risks 7:46-9:43.
• EKS-managed node groups are recommended over self-managed groups for simplified lifecycle management and automatic upgrades, although self-managed groups offer more customization for specific requirements 12:19-13:00.
After provisioning, the video demonstrates verifying the cluster resources in the AWS console and connecting via kubectl to confirm administrative access and functionality 16:54-18:57.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cloud Security. Commonly maps to: Security Architecture and Engineering, Communication and Network Security. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
This is the second part of the Amazon EKS
tutorial. Before we start creating EKS itself, let’s go over the main Kubernetes components. It’s going to be important later in terms of the
IAM permissions we need to grant to EKS. First of all, we have an etcd database.
Kubernetes uses it to store all its state, such as deployment specifications, how
many replicas of each pod it needs to run, and stuff like that. So, it’s
important to regularly back up etcd and be prepared to recover
in case something happens to it. Then we have the scheduler. Its main
job is to watch for newly created pods and assign them to the nodes based on
available CPU and memory and pod requests. Next, we have the controller manager.
It combines many different controllers. It’s basically a reconciliation loop, wh…