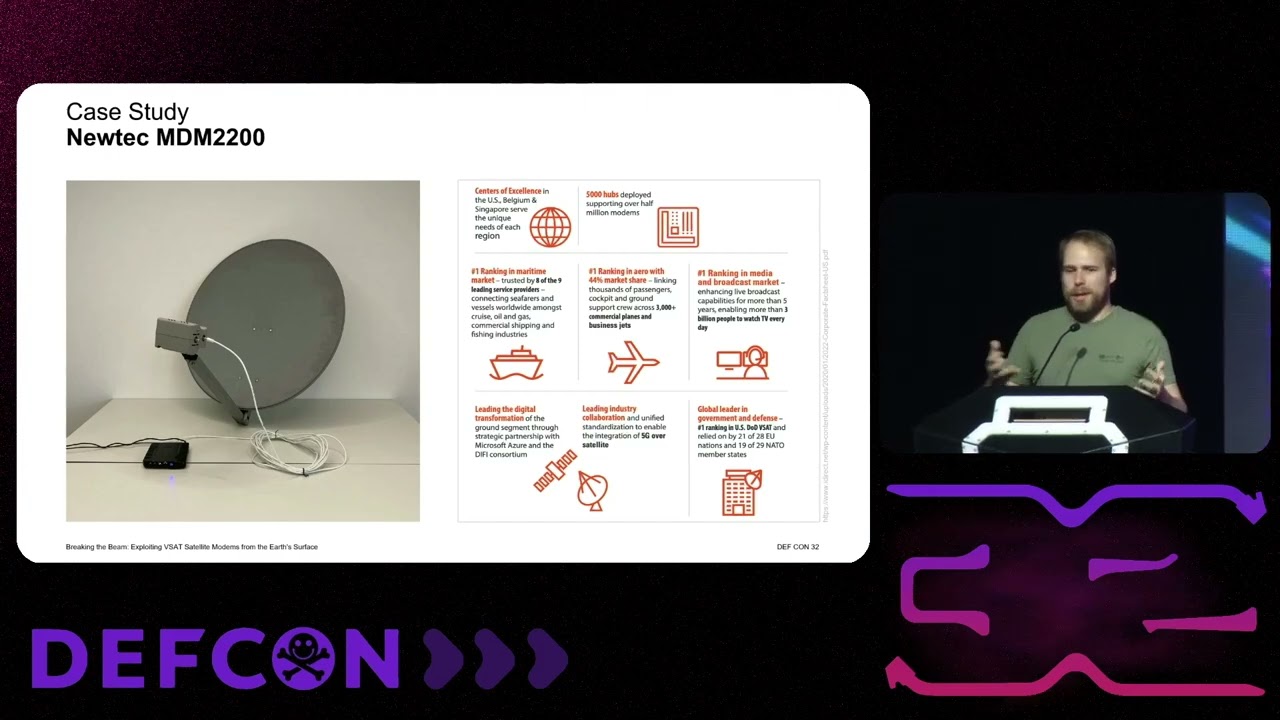
DEF CON 32 - Breaking the Beam:Exploiting VSAT Modems from Earth - Lenders, Willbold, Bisping
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 39:41
Breaking the beam refers to a new wireless attack that exploits vulnerabilities in VASAT (Very Small Aperture Terminal) modems by injecting malicious signals from Earth-based side beams, bypassing traditional security assumptions. This attack enables remote firmware updates, code execution, and denial-of-service, threatening satellite communication integrity. 0:38
Key Takeaways:
• VASAT modems lack data-link security and have unencrypted firmware update signals, enabling remote malicious updates 18:04-18:35.
• A critical buffer overflow vulnerability in the modem’s web interface allows remote code execution, including reverse shell access 20:01-21:00.
• Attackers can inject signals via software-defined radio (SDR) from side angles, breaking the beam and disrupting satellite communication 28:36-33:58.
• The attack targets modems using S3Play protocol (a variant of DVB-RCS), with broad applicability across similar systems 24:00-25:50.
These vulnerabilities demonstrate that VASAT systems are highly susceptible to wireless signal injection, even from non-directive angles, and could be exploited by adversaries with accessible SDR hardware. 38:00-39:30
Sources:
- 0:38 Introduction to the "breaking the beam" attack and its threat model.
- 18:04-18:35 Unencrypted firmware updates and lack of data-link protection.
- 20:01-21:00 Remote code execution via buffer overflow in web interface.
- 28:36-33:58 Wireless s
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
so hello everyone um and Welcome to our presentation on Breaking the beam a new typ of attack at that aims at exploiting vat satellite communication from the Earth but first let me introduce ourself I'm Vincent I'm a cyber security researcher for more than 20 years I've been focusing mostly on the security of wireless networks in my research and currently I'm acting as a director of the Cyber defense campus in Switzerland we have also with us today Johannes he's a PhD student from the University of bom in Germany and is researching uh the software security of space and satellite systems and also with us today is Robin uh he's a graduate student from eth zich and uh has been also working at the Cyber defense campus uh in the context of his master cheses so let me start with what vat uh comm…