Chilly Mac Malware & OAuth Phishing: Detection Tricks, No Treats
Source: YouTube · VMRay · published Oct 23, 2025 · 47:21
VMRay’s October Detection Highlights webinar details critical updates to Virtual Thread Identifiers (VTI) and YARA rules, with a significant focus on enhanced Mac OS threat detection and advanced malware analysis techniques.
Key Takeaways:
• A new VTI targets TOSS modular malware by detecting its efficient IP blacklisting behavior, mapped to the Impact tactic rather than Command and Control. 1:44
• Detection efforts now heavily target Mac OS threats, specifically Atomic Stealer and the notarized ChiliHell backdoor, reflecting a growing trend in macOS malware. 3:15
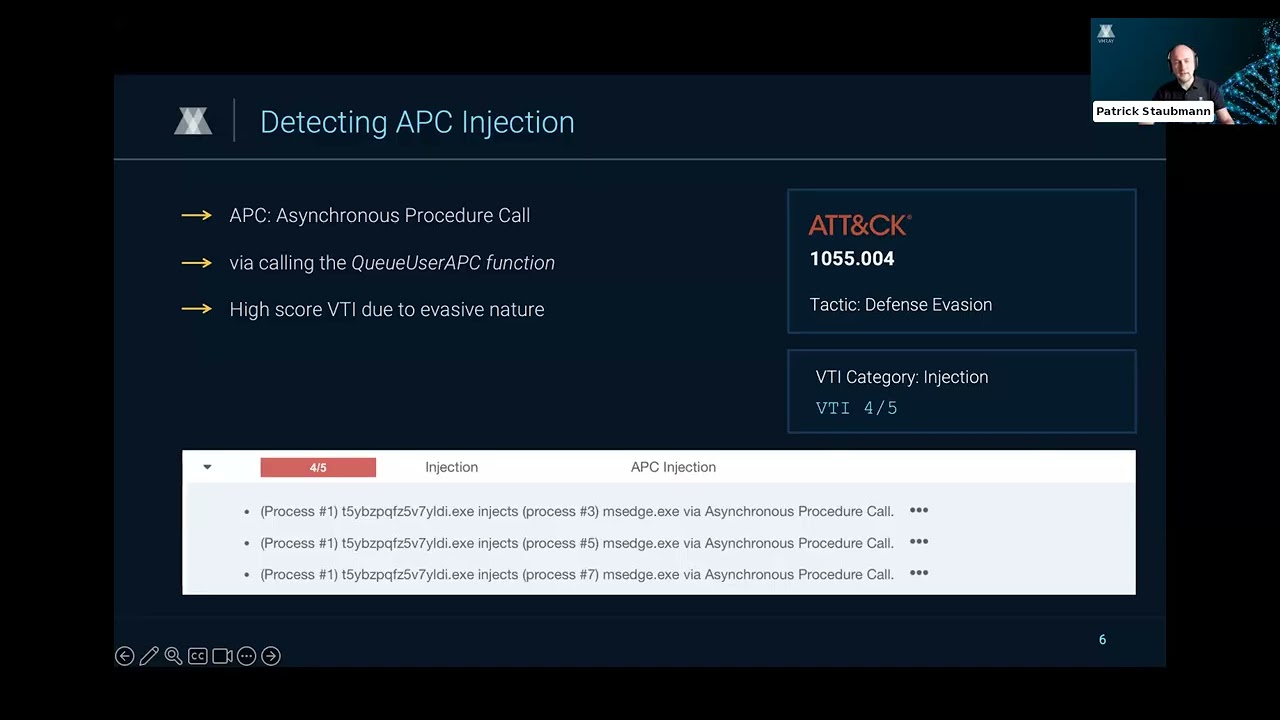
• Patrick Stapman demonstrates SteelC v2’s use of APC injection to stealthily inject code into browser processes, enabling the theft of sensitive web data and cookies. 4:00
These updates provide analysts with deeper visibility into emerging threats, particularly the increasing sophistication of Mac-targeted malware and complex evasion techniques like sleep and APC injection.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Let's wait for a minute for people to join. Then we will get started. All right, I think we can get started. Hey everyone, uh welcome to the October edition of detection highlights webinar series. I'm R2. I do product marketing here at VMRA and I'm joined today by my dear colleague Patrick Stapman team >> thread analysis. Hi Patrick. >> Hi. >> Um so always great to have you. Um so if you're new here every month we share highlights from the labs team the updates uh new VMray thread identifiers. uh we use the acronym VTI and Y rules uh new config extractors and kind of things that help catch new emerging threats faster. Um that said, we only have time to go through the top highlights. So if you're interested in the full change log, definitely check out the monthly blog post f…