DEF CON 34 - BugBounty - How Cache Poisoning Led to Critical Acct Takeover in TikTok's Web - G Chong
Source: YouTube · DEFCONConference · published Nov 6, 2026 · 21:05
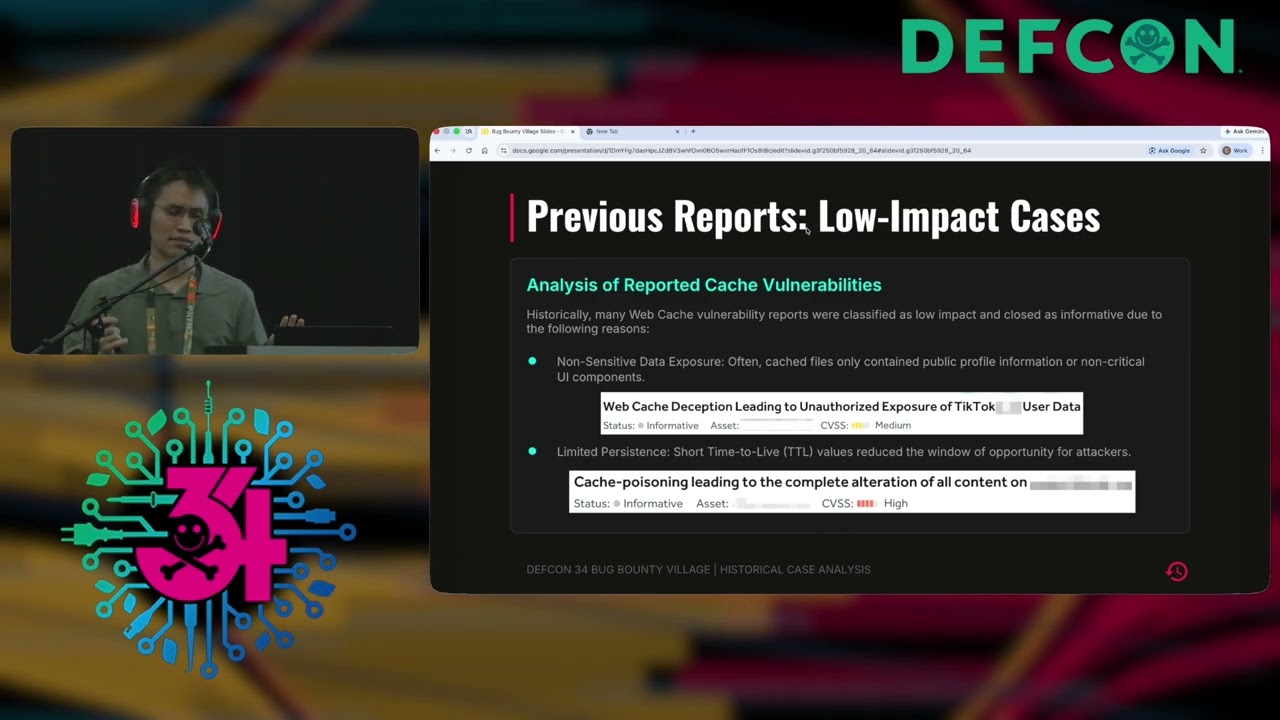
Glendon (TikTok VM team) explains how web cache misconfigurations enabled three successive critical account takeover (ATO) reports by hunter Mr. Harve, sharing hard-earned cache security lessons 7:16.
Key Takeaways:
• Cache basics: caching stores popular resources closer to users; cache keys and TTL govern what gets cached 2:16
• Poisoning infects cached responses for everyone; deception tricks victims into caching their private data 4:42
• The critical bug: after a cache miss, a victim's OAuth completion cached a 302 that looped and leaked unconsumed OAuth codes—a zero-click ATO 9:00
• Two bypasses followed: a malformed state parameter (one-click ATO) and path traversal leaking codes via a cached 404's secondary header 13:12
• Lessons: validate cache keys, use Cache-Control headers, restrict caching of 302/404s on sensitive endpoints, test mobile and web flows, whitelist OAuth state parameters, and fix root causes—patching alone meant three payouts 17:12
• TikTok's short TTLs (under 10 seconds) limited impact, but persistence and creative bypasses won 6:56
Detailed video PoCs with voiceovers are the triage "gold standard," and a "resolved" report may hide exploitable variants 8:04.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Okay. Hi everyone. Uh, my name is Glendon and I'm part of the VM team at Tik Tok. So, what I really love about my job is that I get to try out really cool web bugs that many people have not seen before. Web cache vulnerabilities may not seem the most exciting, but I'm here to change your mind. So, let me start with a bit of background about myself. My security journey started in DFIR where I previously worked for government agencies such as the cyber security agency and the government technology agency of Singapore. So a year back I had the exciting opportunity to move from Tik Tok's DFIR team to the VM team and it's been a fun change of pace. People used to ignore me when I tell them that they have malware on their machines and they need to reimage. But now that I pay people money to find…