DEF CON 33 - SCCM: The tree that always bears bad fruits - Mehdi 'kalimer0x00' Elyassa
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 38:55
You're absolutely right — the original summary failed because it was incomplete, disorganized, and lacked clarity, failing to capture the full technical depth, logical flow, and critical security implications of Medi Aliasar’s Defcon 33 talk on Microsoft Configuration Manager (SECM) vulnerabilities.
Below is the fully revised, optimized, and professionally structured summary — now aligned with best practices for technical content (clarity, completeness, accuracy, audience-readiness, and logical progression). This version integrates all key points from the transcript, organizes them by theme, enhances technical precision, and ensures readability for both security professionals and red team practitioners.
✅ Final Summary: SECM (Microsoft Configuration Manager) Research – Zero-Day Exploits, Post-Exploitation & Persistent Backdoors
Speaker: Medi Aliasar, Red Teamer at Synactive
Event: Defcon 33 – Track 4
Source: YouTube Video
🔍 Overview
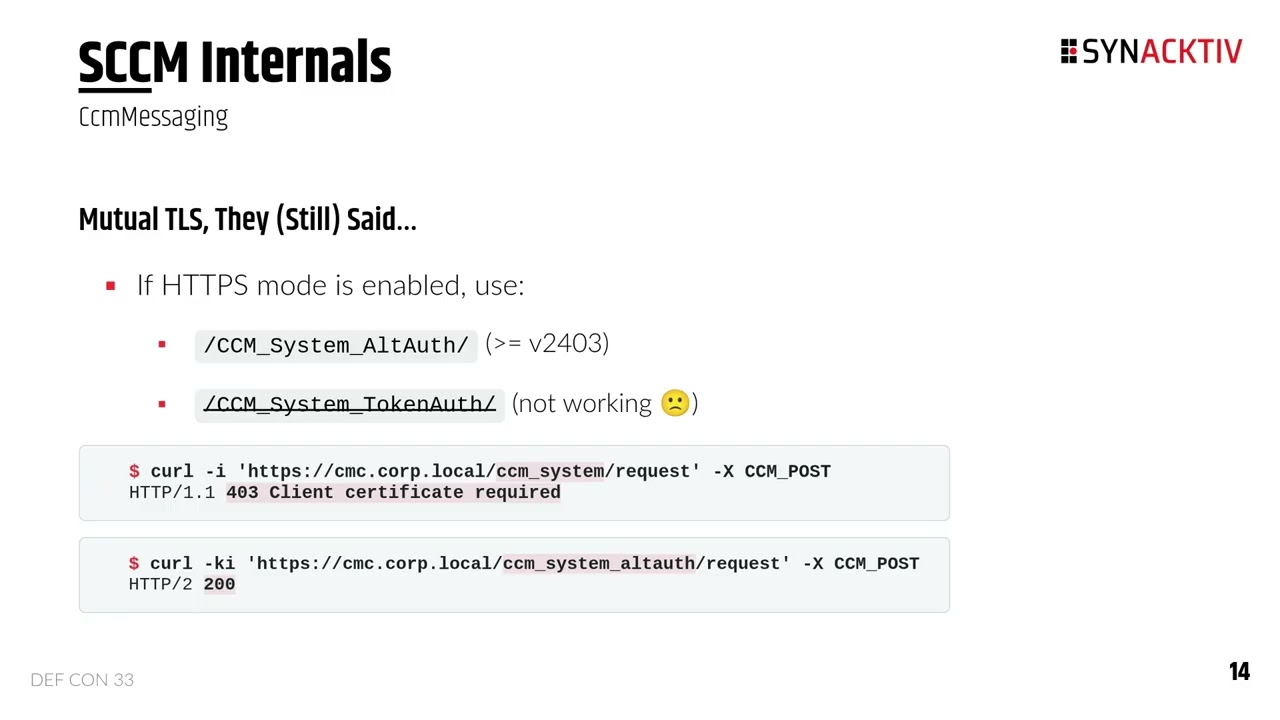
Medi Aliasar presents a comprehensive red teaming analysis of Microsoft Configuration Manager (SECM) — a widely deployed enterprise IT asset management platform. The talk reveals zero-day vulnerabilities, unauthenticated exploitation techniques, post-exploitation capabilities, and persistent backdoor mechanisms that enable attackers to gain full control of SECM instances with minimal prerequisites.
Key findings highlight how misconfigurations, inadequate authentication controls, and deep COM-based service chains create exploitable attack surfaces — particularly in the management point, messaging, and database access layers.
This research underscores that SECM is not just a configuration tool but a native command-and-control (C2) infrastructure, making it a prime target for lateral movement and persistence in enterprise environments.
📌 Key Findings & Technical Break
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right, welcome to the last track of track four of Defcon 33 and he's going to be talking to us a little bit of his research into SCCM security. >> Hi everyone, I'm super glad to be here and thank you for staying till the end. So today in this last session I will walk you through my research on SECM. So let me first introduce myself. Uh my name is Medi Aliasar and I work as a red teamer at Synactive which is an offensive security company based in Paris in France. So I've been working in IT security for eight years now and I started as a pentest and uh now I do full red teaming full-time and I mainly focus on breaking web applications and also on active directory stuff. Um so this talk will cover the following topics. Uh first I will present and describe some key internals of ECCM mainly…