Mythos, Machine-Speed Compromise, and the New Identity Risk
Source: YouTube · SpecterOps · published Nov 18, 2026 · 32:41
The video discusses Anthropic's Claude Mythos model and OpenAI's GPT-5.3/5.4 releases, arguing that AI models are rapidly advancing offensive cyber capabilities—compressing attack timelines and driving exploitation toward 100% feasibility—which forces defenders to adopt an assumed-breach mentality focused on attack path management 0:33-1:04, 9:28-10:08.
Key Takeaways:
• Claude Mythos found 181 working exploits quickly and is described as the first model capable of "machine-speed offensive security," with access restricted as "too dangerous to release publicly" 0:49-0:52, 5:56-6:25.
• In a UK AI Security Institute benchmark using a SpecterOps-built enterprise-style CTF range, Mythos became the first model to complete the full chain end-to-end (~30% of trials), signaling a broader trend of improving cyber capability 3:57-5:08.
• AI compresses the time between initial access and successful exploitation, shrinking defender response windows to unreasonable levels and enabling attacks at scale (thousands of simultaneous agent-driven attempts) 6:33-7:45, 28:38-29:10.
• Vulnerabilities are only half the story: behind every vulnerability is an identity, and the same exploit can have vastly different impact depending on the attack paths emanating from that identity 17:32-19:02.
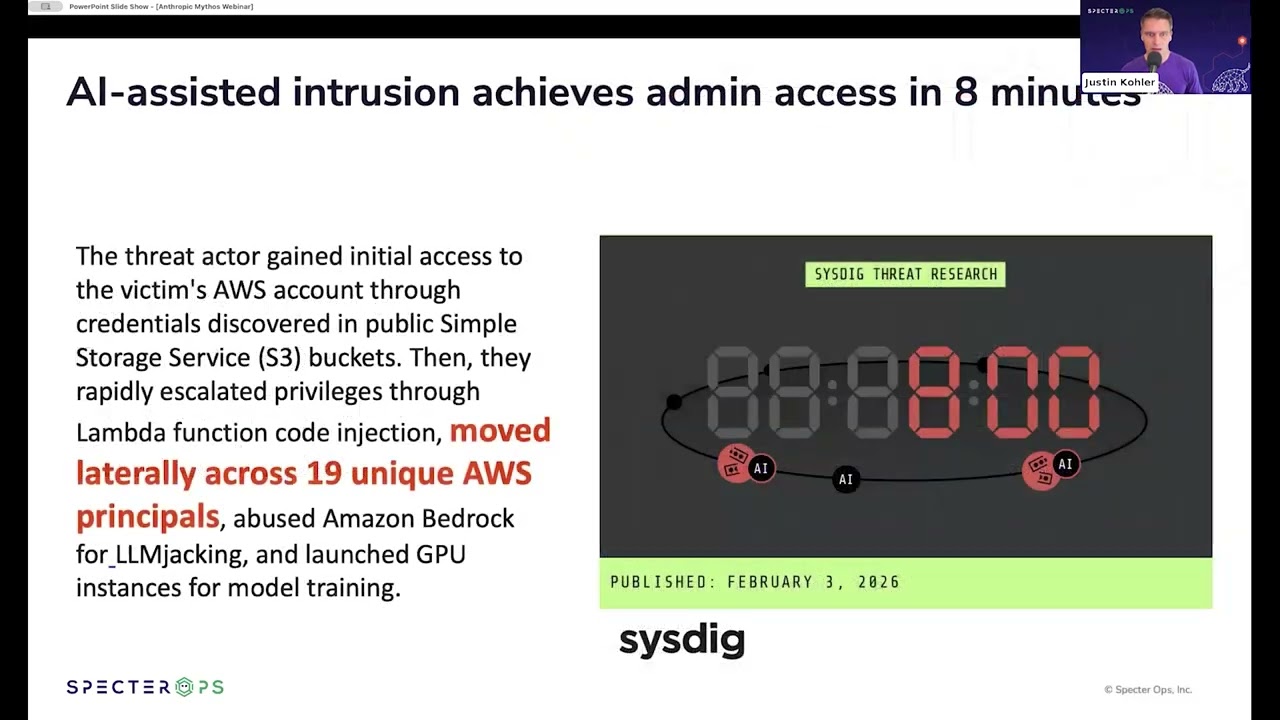
• Real incidents like the Sysdig-reported AWS attack (attackers chaining 19 principals to abuse Bedrock) and the Vercel breach (over-privileged OAuth grants to an AI platform) show attackers exploiting inter-organizational, third-party AI dependencies 12:24-14:16, 22:26-25:01.
• Recommended strategy: assume compromise, map identity relationships, identify critical assets, and proactively trim attack paths—"prevention first, detection always"—prioritizing tier-zero/root/critical assets first 25:57-27:44, 29:14-31:02, 31:52-32:36.
AI-driven attacks will only get faster and cheaper, so defenders should stop fixating on initial access and instead limit blast radius by managing identity attack paths. Whether it's Mythos, Codex, or the next model, this shift is coming regardless of which tool arrives first.
Sources:
- 0:33-1:04 Introduction to Mythos launch and its implications for enterprise security
- 0:49-0:52 Mythos found 181 working exploits in a short time
- 3:57-5:08 UK AISI CTF range results: Mythos completes end-to-end attack chain ~30% of the time
- 5:56-6:25 Mythos claims: machine-speed offensive security, restricted access
- 6:33-7:45 AI compresses attacker timelines, shrinking defender reaction windows
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Well, let's just start with the obvious. I think everybody thinks that this year has been kind of crazy. I have we have this talk or we have this saying on our engineering team of what a week this day has been or what a month this week has been. I think anybody from the beginning of the year just trying to keep up with all the news has been kind of crazy. But yeah, we wanted to dive into this story. There's been a lot of updates and we wanted to give our take on it. >> Yeah, so the main the main kind of impetus of this webinar is the launch of Claude Anthropic's Claude Mythos model and I think there's been a lot of discussion, a lot of kind of fear, uncertainty and doubt about what this could mean for the overarching industry. You see for instance they they came up with 181 working exploit…