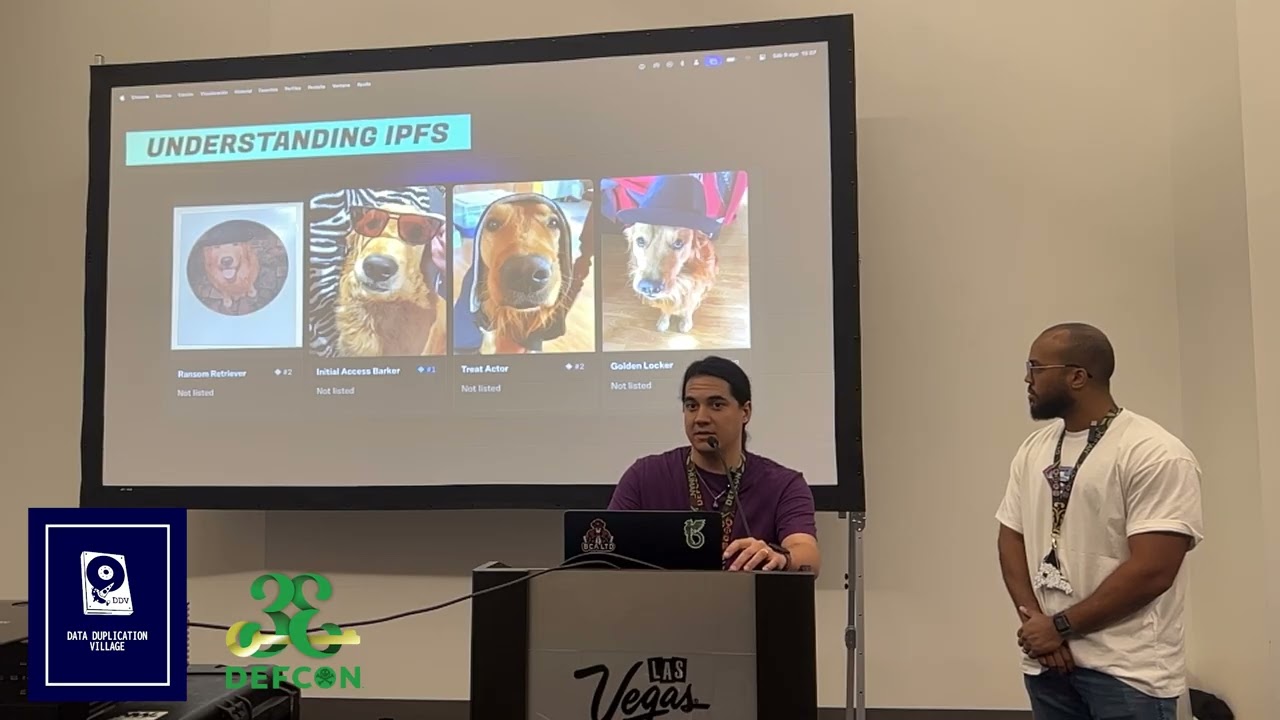
DEF CON 33 - Data Duplication Village - Fungible Threats - Mauro Edritch, Nelson Colon
Source: YouTube · DEFCONConference · published Oct 21, 2025 · 32:03
Security researchers Mu and Nelson demonstrate how threat actors can abuse distributed technologies as resilient command and control (C2) servers that are nearly impossible to take down through conventional methods 0:20.
Key Takeaways:
• IPFS can be exploited by hiding malicious payloads in NFT metadata on platforms like OpenSea, making takedowns extremely difficult due to its distributed nature across multiple nodes 4:27
• Google Calendar event descriptions can contain base64-encoded malicious commands that persist even if the creator's account is suspended, and traffic is rarely blocked by organizations 11:46
• Cloudflare R2 buckets can store and distribute malware while appearing as legitimate Cloudflare traffic, creating a dilemma for security admins who must choose between potential security breaches and blocking essential services 21:47
• CodeX, a decentralized blockchain storage system, allows anonymous hosting of malicious files that are censorship-resistant by design, with no sanitization of uploaded content 27:00
The researchers emphasize that as new distributed technologies emerge, threat actors will immediately seek ways to exploit them, making it essential for developers to implement security boundaries from the outset 30:13.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hey, thanks everybody for coming. Uh we have our our speakers Mu and Nelson here to talk about some threats that they've identified. They gave this talk yesterday and they come back to give the talk again maybe with some additional information. So welcome back to the D. >> Thanks. >> Hello everyone. Thank you for coming to our talk. My name is Mal. My friend here is Nelson. We spoke about this talk yesterday. So thanks for coming to the second edition. Um on this talk we are going to summarize how to abuse certain technologies that are distributed are using in order to distribute files in order to be used as a way to distribute malicious component in a way that it is hard or even sometimes near impossible to take them down at least on an it's almost impossible to take them down by classic …