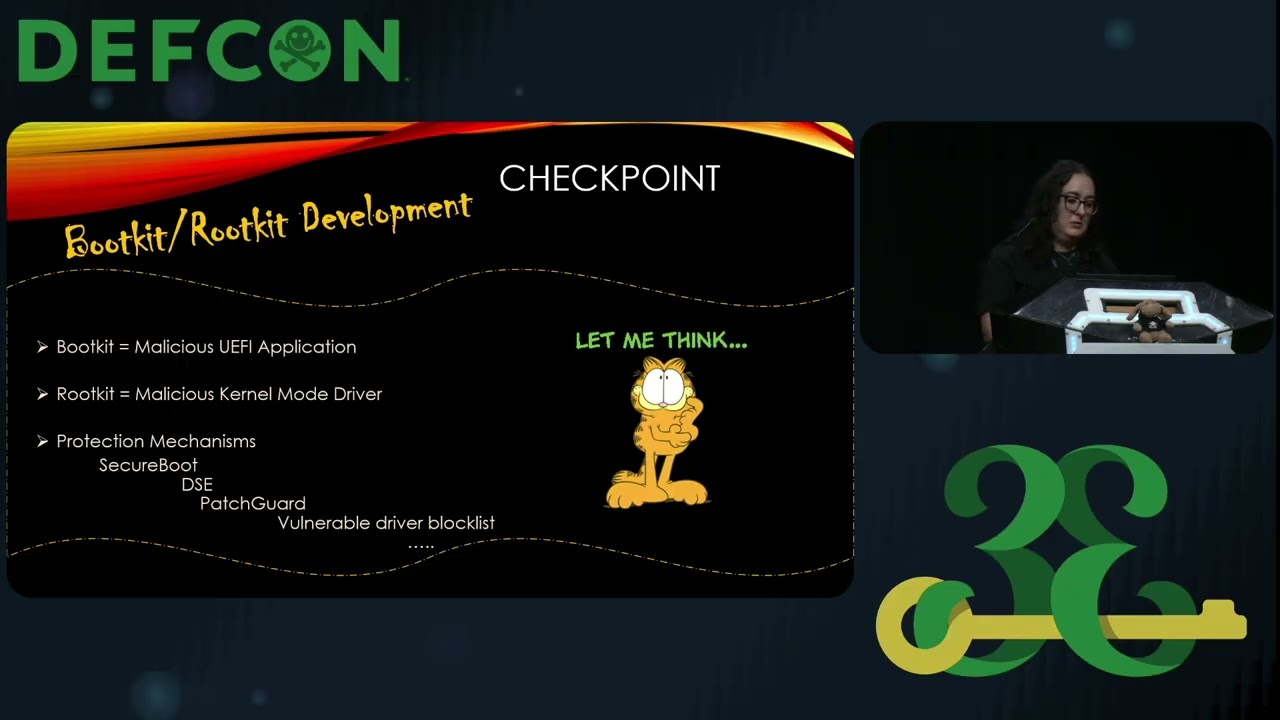
DEF CON 33 - Infecting the Boot to Own the Kernel - Alejandro Vazquez, Maria San Jose
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 39:29
This Defcon 33 presentation 0:04 demonstrates a fully functional bootkit and rootkit released publicly to help security researchers understand these threats.
Key Takeaways:
• The presenters released a complete documented bootkit 0:40 and rootkit with source code, focusing on practical implementation rather than theory 0:28
• A bootkit is a malicious UEFI application 3:54 that hijacks the boot process, while a rootkit is a malicious kernel-mode driver 4:37 that operates at the highest privilege level
• Key protection mechanisms include Secure Boot 7:20 and Driver Signature Enforcement 8:29, which the malware demonstrates bypassing
• The bootkit works by hooking functions during boot stages 10:14 while the rootkit implements six core capabilities including process hiding, network filtering, and kernel-level C2 19:04
• All resources including source code, documentation, and setup scripts are provided through multiple repositories 36:02
The presentation concludes with a live demonstration of the malware running on a physical machine with Secure Boot enabled 33:00.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Um, it's a pleasure for us to be here at Defcon 33 and honestly it's uh exciting just to see so many people here interested in building this malware. So, thank you for coming. I'm not going to ask questions. I suppose you want to develop malware, but whatever. Um, before diving in, we want to make something very clear right from the start so everyone is on the same page. Okay. uh this is not a talk about theoretical bootkit or rootkit development. What we are going to share with you today is a fully functional working piece of malware that we have developed and in a moment we will explain why we have chosen to make it public. So during this talk we will share with you a complete documented boot kit ready for you to use build and study. Alongside that, a rootkit as well that…