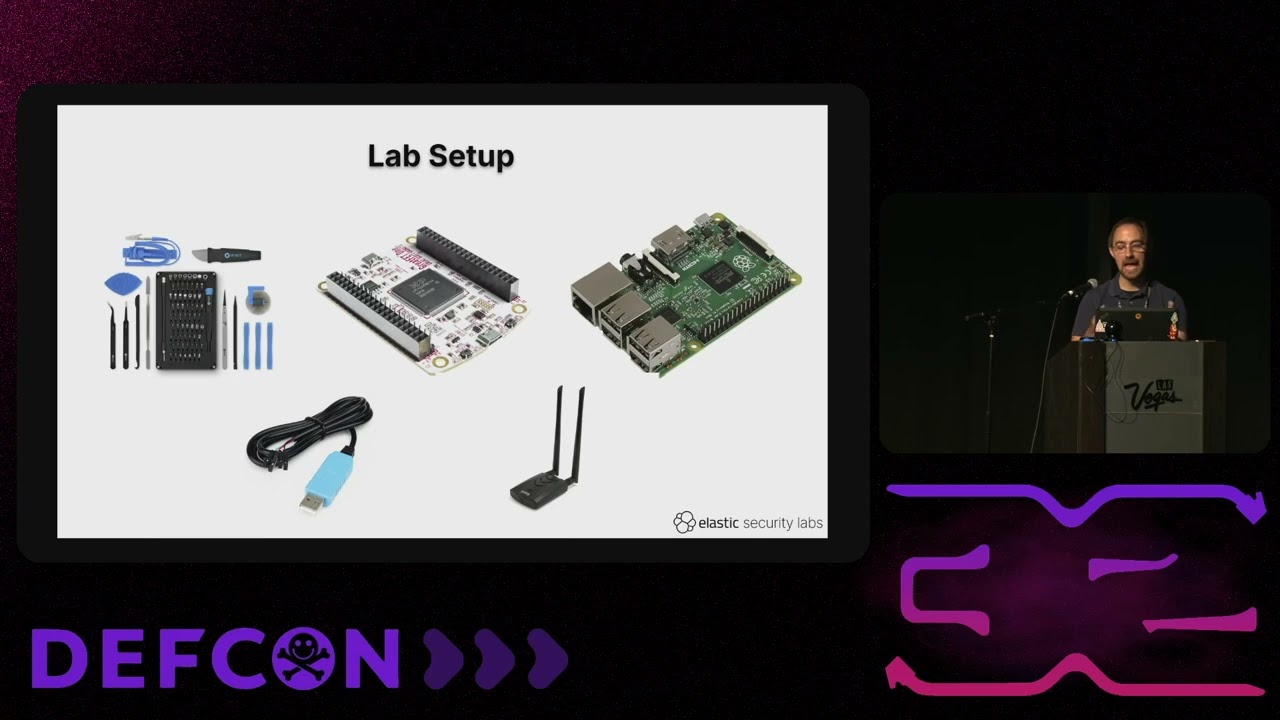
DEF CON 32 - What To Expect When You’re Exploiting: 0Days Baby Monitors & Wi-Fi Cams - Mager, Forte
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 40:04
Wi-Fi cameras, especially low-cost models like the Ons View Q5 and Q6, have critical security flaws that allow unauthorized access, device compromise, and data exposure. A major vulnerability exists in the cloud platform (AJ Cloud), where devices can be accessed without authentication, and peer-to-peer communication is exposed to manipulation.
Key Takeaways:
• Unauthenticated access to the AJ Cloud platform allows attackers to retrieve device credentials and configuration data, including firmware version, SSID, MAC address, and geolocation 18:40-18:52.
• A critical access control flaw enables an attacker to spoof a device ID and gain control over a camera not associated with their account 23:05-23:12.
• The peer-to-peer protocol (PPPP) used for remote access is vulnerable to manipulation, allowing attackers to overwrite the device’s serial number and brick the camera 35:39-36:21.
• Devices have exposed serial access, an SD card slot, and a reset button, enabling physical attacks and firmware manipulation 9:00-9:35.
These vulnerabilities affect not only Ons View and Sonado devices but also other brands like Fimi, due to shared cloud infrastructure. While vendors use basic protections like certificate-based authentication and read-only file systems, the lack of secure boot and unauthenticated cloud access remains a severe risk. Mitigations include network segmentation, blocking outbound traffic, and flashing with a secure OS.
Sources:
- 18:40-18:52 Device configuration logs reveal sensitive data including firmware, SSID, and geolocation.
- 23:05-23:12 Access control flaw allows device ID spoofing to gain unauthorized
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
good morning Defcon uh we are going to be hacking some baby monitors and Wi-Fi cameras today so a little bit about me my name is Mark Meer I'm senior manager of security research at elastic uh my background is primarily in Windows mware research and reverse engineering uh so what do we need to know about uh Wi-Fi cameras and baby monitors today um basically we're going to assume they're the exact same thing because they pretty much have the same feature Set uh they're literally marketed and sold as equivalent devices so uh what we're talking about is the $10 cameras you can find on Amazon uh that require internet connectivity to that specific vendor Cloud platform and there's very basic operations pan tilt Zoom uh things along those lines motion detection whatever but yeah that's the what …