Black Hat Asia 2026 | LLM-Empowered Differential Testing for the Ethereum Infrastructure
Source: YouTube · Black Hat · published Aug 28, 2026 · 39:04
BLUF: This talk presents two academic papers using LLM-assisted differential testing to find bugs in Ethereum client infrastructure (EVM and APIs), an overlooked area where vulnerabilities mean direct financial losses 2:00-4:06.
Key Takeaways:
• Client security is under-researched (~60% of academic work targets smart contracts); real incidents include a Geth shallow-copy bug that forked the chain and a Prism bug that dropped network participation to 75% 4:36-5:18, 7:13-9:33.
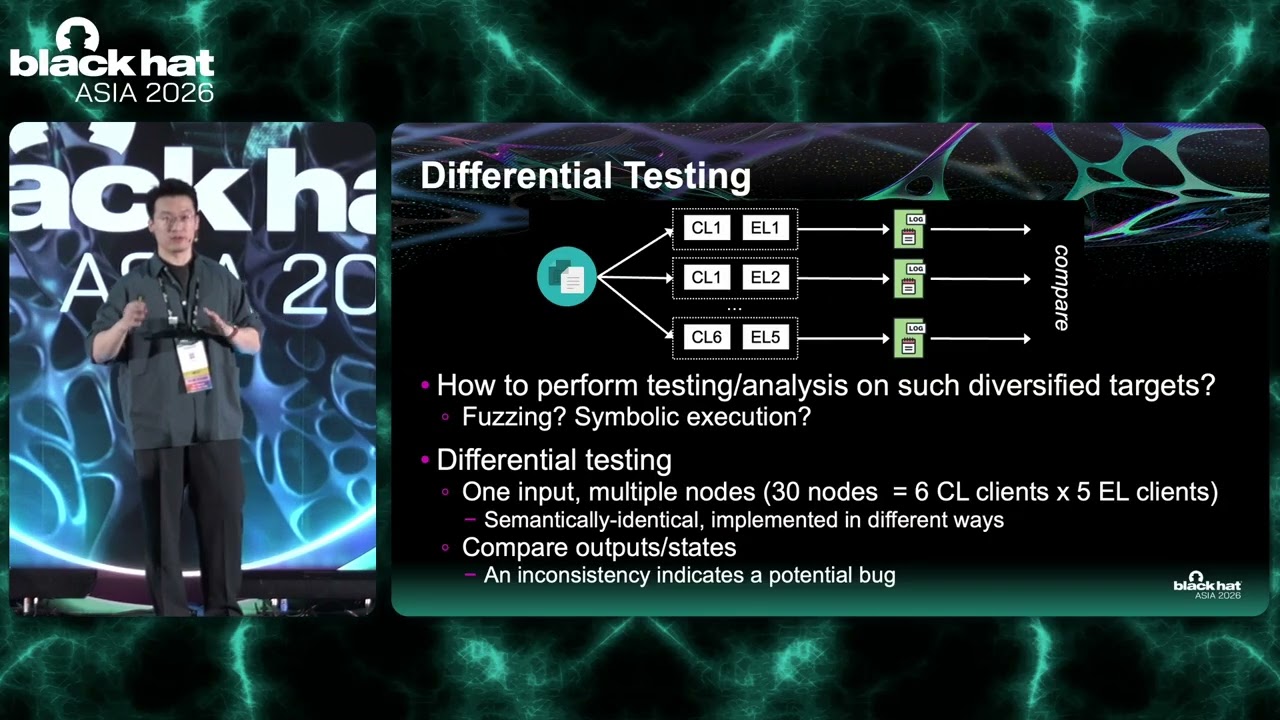
• The approach builds a 30-node local testnet (6 consensus × 5 execution clients), sends identical inputs, and flags cross-client inconsistencies in outputs, gas, and state as candidate bugs 11:57-13:06.
• For EVMs, LLMs generate semantically valid bytecode seeds, augmented via ICFGs; for APIs, spec schemas generate valid/invalid JSON-RPC requests, with LLM-as-judge filtering benign noise 17:29-20:00, 24:54-28:11.
• Results: 98 bugs (26 EVM, 72 API), >85% confirmed/fixed, affecting all 11 mainstream clients—including a Geth PREVRANDAO null-pointer crash, a Besu error-handling bug risking consensus confusion, and two bugs in the beacon API spec itself 29:05-33:59.
The speakers conclude client security deserves equal priority with smart contract security; their open-source approach is simple and effective, with many untested vectors (P2P, gas, state) remaining for future research 35:37-37:19.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone and uh today our topic is about as you can see the fortifying the foundation and uh that is the large language model empowered differential testing for Ethereum infrastructure. So uh before that let me introduce ourself. So we are the team and I'm Yuho and I'm a research assistant professor from polyu and I'm also a security consultant from member group which is a web3 security company and my co-speaker Jimma he is a doctor of engineering from behind university and Junwenson lab and our team also has chacher wu the head of web security and we have some professors from husd be bhan university and jungwensson laboratory so um here is today's agenda And we will go through very detailedly. So first I will go the introduction and then because our talk today contains two papers. S…