Black Hat Asia 2026 | Revealing User Activity on macOS for Apple Silicon
Source: YouTube · Black Hat · published Aug 30, 2026 · 31:05
This talk presents "TiDe," a timerless interrupt side-channel attack against Apple Silicon/macOS that exploits deterministic overwrites of the X18 platform register to detect interrupts, enabling website fingerprinting (93.8% accuracy) and video fingerprinting (78.1% accuracy) 9:57.
Key Takeaways:
• Keystrokes create interrupt timing pairs shaped by keyboard layout, making interrupts a viable side channel 5:04.
• macOS lacks Linux's /proc interrupts interface and prior techniques are x86-specific, requiring a timer-free method 6:13.
• TiDe's "heartbeat" comes from macOS double-map macros overwriting the user-readable X18 register on every interrupt 13:13.
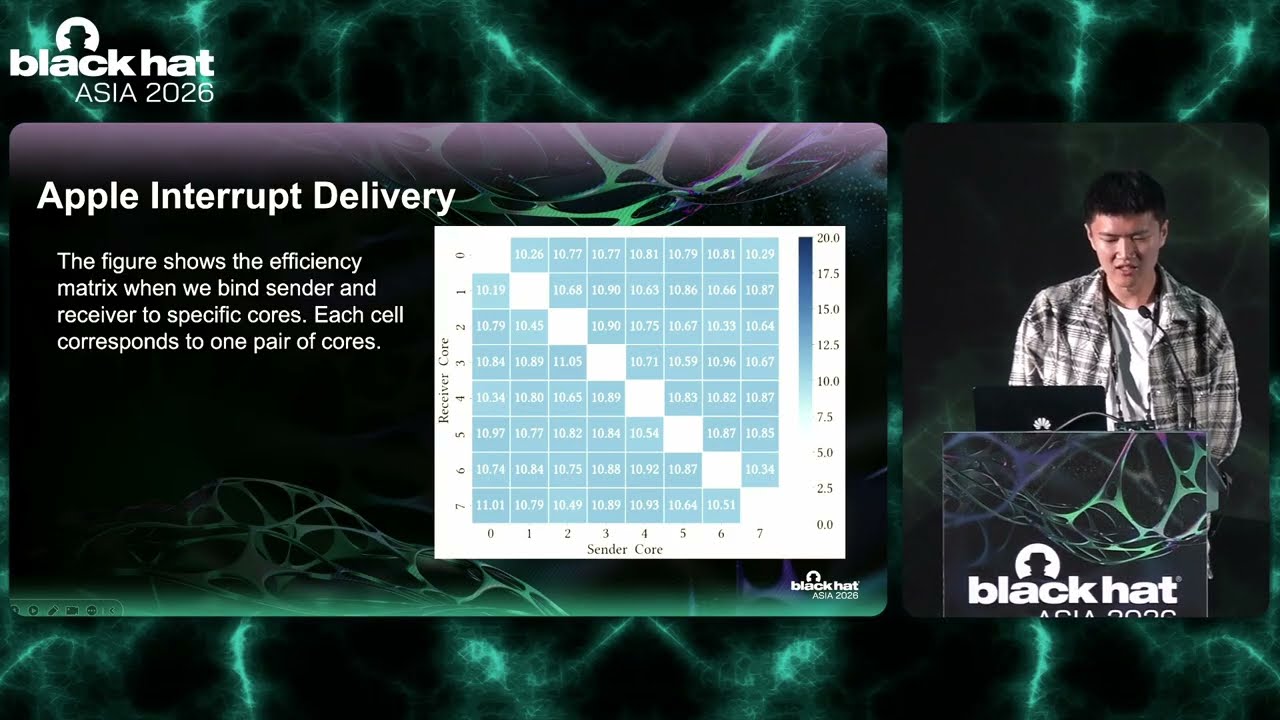
• Apple's interrupt controller distributes shared peripheral interrupts uniformly across active cores, enabling multicore attacks 16:23.
• Using a CNN-LSTM classifier, TiDe achieves 93.8% closed-world and 91.5% open-world website fingerprinting accuracy, plus 78.1% top-1 accuracy on top YouTube videos 23:42.
• The attack works on M1–M5 MacBooks, Mac minis, and iPhone 16 Pro; Apple deemed it out of scope, and fake network interrupts only reduce accuracy to ~60% at ~10% overhead 25:50.
The talk closes with three lessons: timer-based defenses alone are insufficient, closed ecosystems are not automatically secure, and independent security evaluation is essential 29:31.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hi everyone. Thanks for coming to my talk. I'm very honored to be here. Today, I will talk about how to attack the Apple system using interrupt side channels. First of all, let me talk a bit about about myself. I'm Xinlong. Currently a PhD student at Peking University. And I will join Shandong University as an associate professor this July. You can reach me via WeChat or email. And of course, this work was not done was not done alone. I'm very fortunate to work with Zhijang from the University of Western Australia, Tianyu from Tsinghua University, Chenni Shang, my advisor from Peking University, and Trevor Carlson from the University at the National University of Singapore. Let's start directly into the topic. At the first, side channel attacks were mainly about physical devices. Around ar…