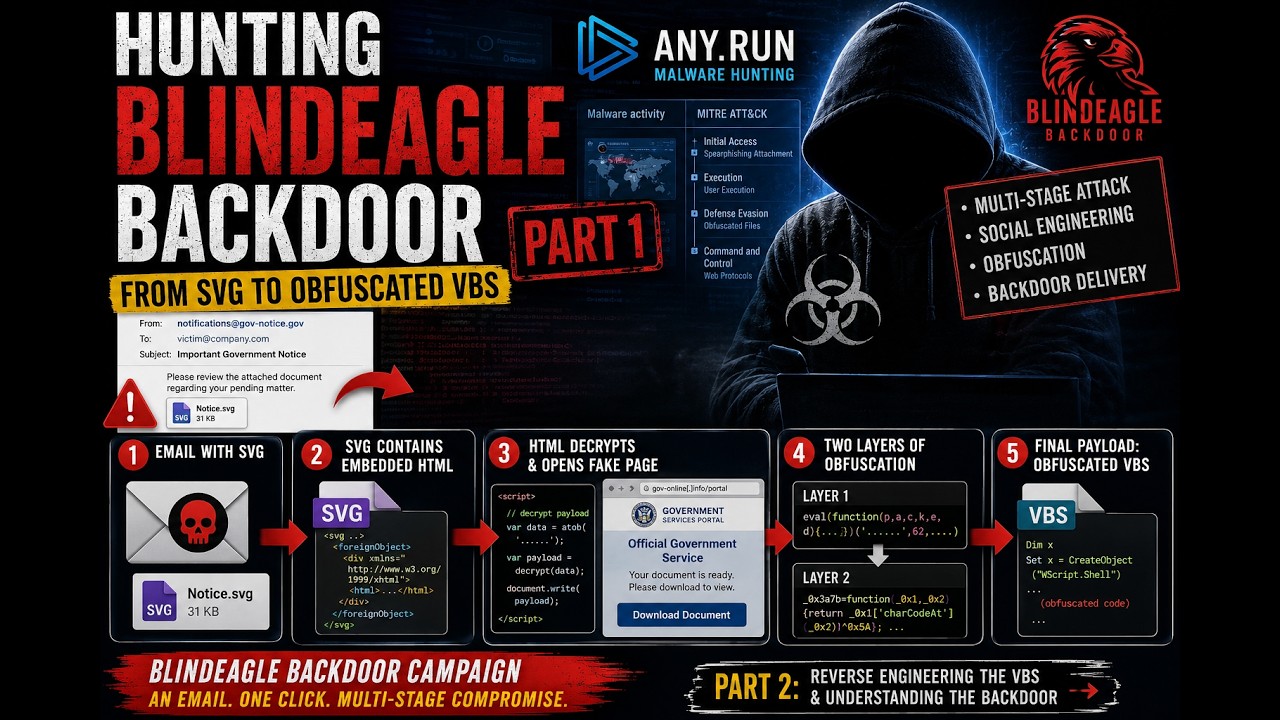
Hunting BlindEagle | From Malicious SVG to Obfuscated VBS Payload Part 1
Source: YouTube · Malware Research Diary · published Aug 15, 2026 · 1:06:53
BLUF: This video documents the reverse engineering of a sophisticated "Blind Eagle" malware campaign targeting Spanish-speaking users, showcasing a multi-layered obfuscation technique involving base64 decoding, array reordering, and XOR encryption to deliver a click-fix payload. 2:03
Key Takeaways:
• The attack begins with an EML file containing an HTML attachment that triggers a zip download, serving as the initial delivery mechanism for the malware 3:02.
• The first layer of obfuscation involves embedding a large encoded string within the HTML, which the analyst decodes from base64 to reveal the next stage of the payload 3:58.
• A critical anti-analysis technique identified is the randomization of data buffers into arrays with specific index mappings, requiring the analyst to reconstruct the original data order using a Python script 13:05.
• The decryption process utilizes complex XOR logic with multiple keys derived from the reorganized data, highlighting the sophistication of the "Blind Eagle" group's infrastructure 17:30.
• After several layers of JavaScript decryption, the final payload is revealed to be a VBScript designed to collect username, password, and configuration data from the victim 44:11.
• The video emphasizes the importance of static analysis and reverse engineering to understand the malware's true functionality, as running it would only show a benign interface 06:43.
Closing Statement:
The analysis reveals a highly structured and multi-stage attack chain designed to evade detection while harvesting sensitive user credentials. This case study underscores the necessity of deep code inspection when dealing with politically motivated threat actors like Blind Eagle.
Sources:
- 0:43 Introduction to the "Blind Eagle" malware family and its target demographic.
- 2:03 Examination of the initial EML file and its embedded HTML attachment.
- 3:58 Decoding the base64 string to reveal the underlying payload structure.
- 13:05 Explanation of the array reordering technique used to obscure the malicious code.
- 17:30 Breakdown of the XOR decryption keys and logic.
- 44:11 Identification of the final VBScript payload and its credential harvesting goals.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone, welcome back. Um, it's been a while, seven days since the last time I analyzed anything. Um, thought today let's um do some huntings on app any run. So to see if there's anything interesting. Um let's see quasa. Yeah. Um so we search for back door. Too many back door blind eagle. I don't think I ever analyzing what is a blind eagle before. So um let's take a look see. So seem to be Indian. Um who do they target? Some type of um Spanish. Um, what's the password in here? The password is that mean? Well, let's take a look. So, so we download is basically an EML file. Um, city hunt the password is um infected to um extract out the file. So let's remove the zip. Um so um EML is a email file format and it's a textbased file so you can open it in vi um to to um review the content …