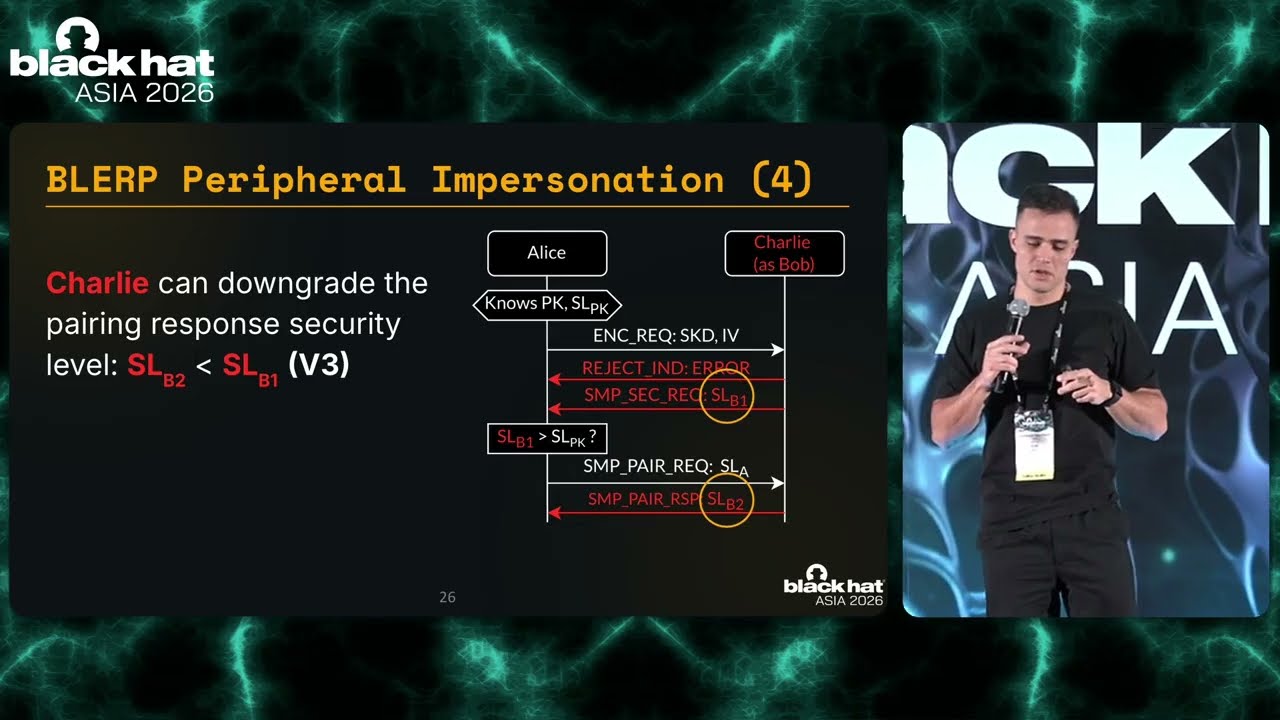
Black Hat Asia 2026 | Exploiting BLE Re-Pairing with the BLERP Attacks
Source: YouTube · Black Hat · published Aug 30, 2026 · 37:45
This talk presents "BLUR" attacks—six protocol vulnerabilities in BLE re-pairing enabling impersonation and man-in-the-middle attacks, demonstrated on 23 devices across 13 vendors 8:51-9:21.
Key Takeaways:
• BLE re-pairing is barely specified (4 mentions in 3,000 pages) and never researched, making it an unexamined critical attack surface 7:04-7:30.
• Attacks exploit missing authentication and no enforcement of security levels, enabling downgrades during re-pairing 16:03-17:20.
• A demo showed peripheral impersonation of a Logitech mouse, controlling the cursor after unauthenticated re-pairing 18:00-20:04.
• Four attacks (central/peripheral impersonation, single/double-channel MitM) included a stealthy entropy downgrade to brute-forceable keys 21:12-22:52.
• Nearly all 23 tested devices were vulnerable; only Windows and Linux resisted by disconnecting on encryption errors 27:37-28:26.
• The Bluetooth SIG dismissed the findings and the standard remains unfixed, though Google, Apple, and Apache NimBLE patched; a CVE (CVSS 8.1) was assigned 33:01-36:03.
These protocol flaws affect billions of BLE devices regardless of hardware or OS; the toolkit and mitigations are open sourced on GitHub.
Sources:
- 7:04-7:30 Under-specified re-pairing attack surface
- 16:03-17:20 Missing security-level enforcement
- 18:00-20:04 Peripheral impersonation demo
- 27:37-28:26 Evaluation across 23 devices
- 33:01-36:03 Disclosure outcomes and CVE
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Thank you everybody and today our talk will be about exploiting the B repairing with the blurp attacks. Uh my name is Tomaso Saketi. I'm PhD student at URICOM and I work on wireless and protocol security. And this talk will be uh hosted together with my supervisor Daniel Antoni which I will give the award now. >> Hi. Hi to everybody. Uh thanks for joining our talk. My name is Daniel Antonio. I'm an assistant professor at UROM a research center and university located in southern part of France. and I do research in system security and privacy and um this is the talk outline. We will start with a quick introduction about BE. Then we will see the blur vulnerabilities and attacks, some attack demos, a toolkit that we developed and open source implementing the attacks, some experimental results…