DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 38:16
SQL injection isn't dead—attackers can exploit binary database protocols through integer overflows and truncation bugs 2:40.
Key Takeaways:
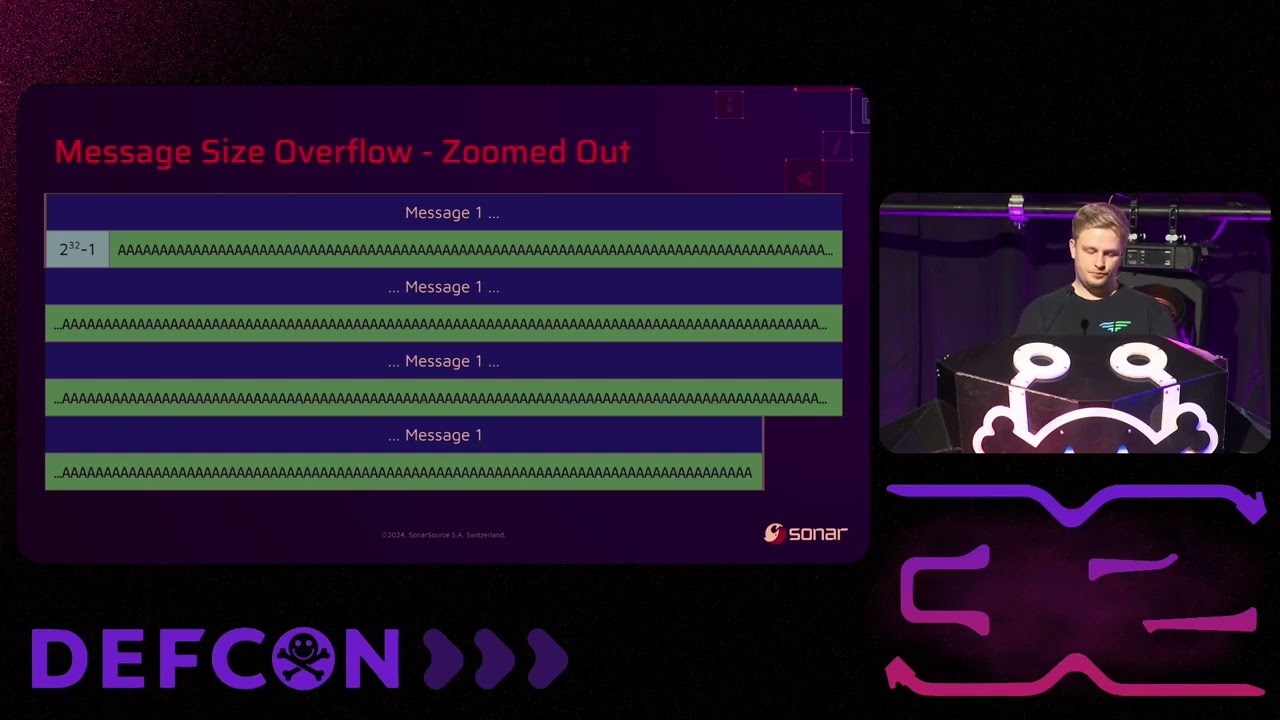
• PostgreSQL and MongoDB client libraries suffer from integer overflow truncation in 4-byte length fields, enabling SQL injection via oversized payloads 7:00.
• Attackers can inject full SQL statements (e.g., insert admin users) by crafting large payloads that trigger parsing errors and message desyncs 9:40.
• Exploits are feasible in real-world apps like Harbor and Grafana, especially when input size limits are disabled or bypassed via compression or SSRF 28:00.
• Language differences matter: Go, Python, and Rust allow large payloads; Java and JavaScript have limitations due to integer overflow behaviors 31:00.
This vulnerability demonstrates that SQL injection remains a real threat, even in applications using modern, secure coding practices—attackers simply go deeper into the protocol layer.
Sources:
- 2:40 Discussion of integer overflow in binary protocols and its relevance.
- 7:00 Technical breakdown of PostgreSQL truncation vulnerability.
- 9:40 Demonstration of SQL injection via message desync in PostgreSQL.
- 28:00 Real-world exploit scenarios including SSRF and compression bypass.
- 31:00 Language-specific behavior of integer overflows and payload handling.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
welcome everybody to SQL injection isn't dead smuggling queries at the protocol level or how I like to call it SQL injection lower decks because usually with SQL injection you're at the high level like at the bridge where the captain and the high ranking officers are and they're speaking their query language and their business language but today we're going to do go down to the lower decks where the mechanics are and where they shift around the bits and bites so to hook you at the beginning I have a small teaser this code snippit is a small HTTP request Handler written in go and it just takes a user ID from the body and uses it in a prepared statement to select the user and if you think everything's fine here there's no way for skl injection then you should stay because I'm going to prove …