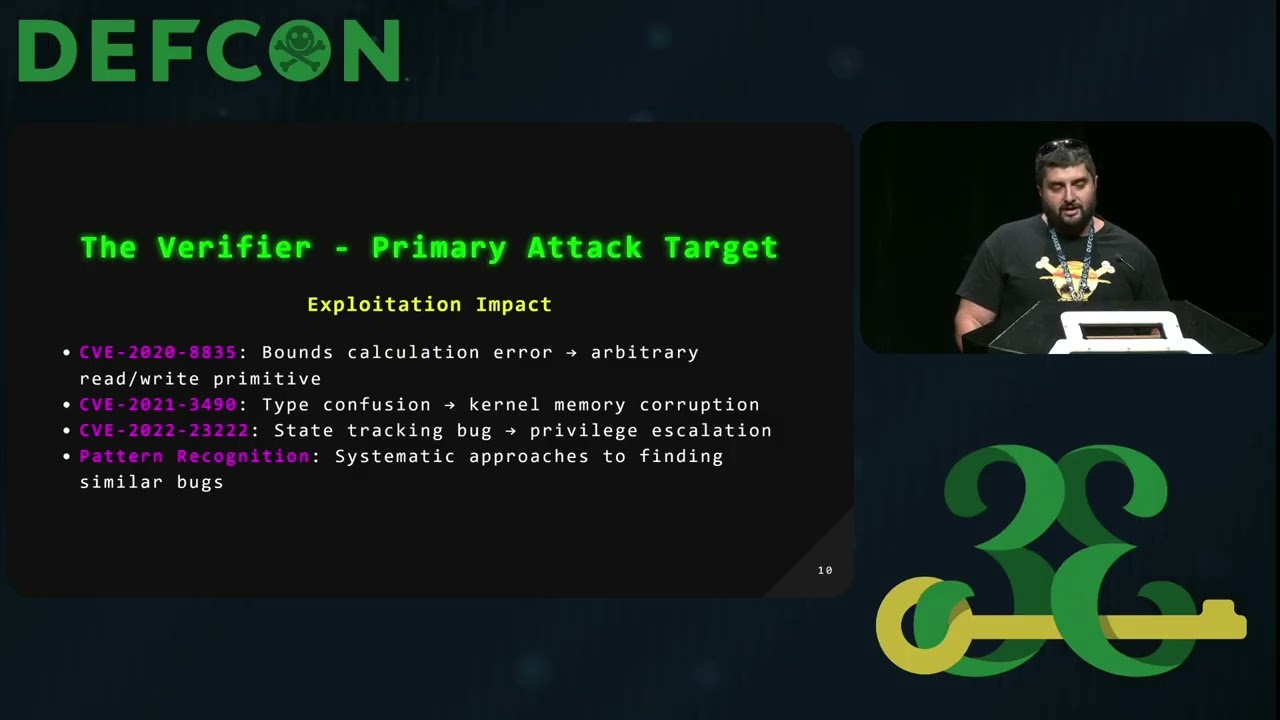
DEF CON 33 - Finding and Exploiting Kernel Vulnerabilities in the eBPF Subsystem - Agostino Panico
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 36:03
The presentation demonstrates how eBPF, despite being considered a secure sandbox, can be exploited to create kernel attack vectors through systematic analysis 0:50-0:53. eBPF has evolved from a simple packet filter into a complete virtual machine running with ring zero privileges, creating a massive and growing attack surface 1:08-1:12.
Key Takeaways:
• eBPF's attack surface is extensive across the verifier, JIT compilation, eBPF maps, and helper functions 5:21-5:25
• Traditional fuzzing fails against eBPF because the verifier blocks 99.99% of randomly generated programs 13:42-13:56
• Leviathan framework uses state-aware fuzzing to target specific vulnerability classes in the verifier 16:02-16:06
• Exploitation techniques include bound calculation vulnerabilities and type confusion attacks 31:00-31:04
• Defenders need better monitoring, auditing, and real-time detection for eBPF systems 31:54-31:56
The Leviathan framework, which will be open-sourced, enables reliable exploitation chains and has already discovered dozens of eBPF vulnerabilities 35:35-35:40.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Good morning, Defcon. I'm Vanish and I hope you are awake and you didn't party too much yesterday. Um, and I'm here just to ruin your fate in Linux in a subsystem in a Linux system that usually you think it's secure. Um, when most people think about ABPF, they think observability, they think networking, I think ring zero playground. Today we are going to systematically fuds and analyze ABPF subsystems and show you and I'm going to show you exactly how to turn the world most trusted sandbox into your personal kernel vector. That's the idea. It is what we are going to accomplish in the next 45 minutes almost. First, I'll show you why ABPF's attack surface is absolutely massive and it's getting worse for every kernel update. Second, we'll dive into state aware fuzzing, the technique that actu…