DEF CON 3 3 - Exploiting Vulns in EV Charging Comms - Jan Berens, Marcell Szakály, Sebastian Köhler
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 55:09
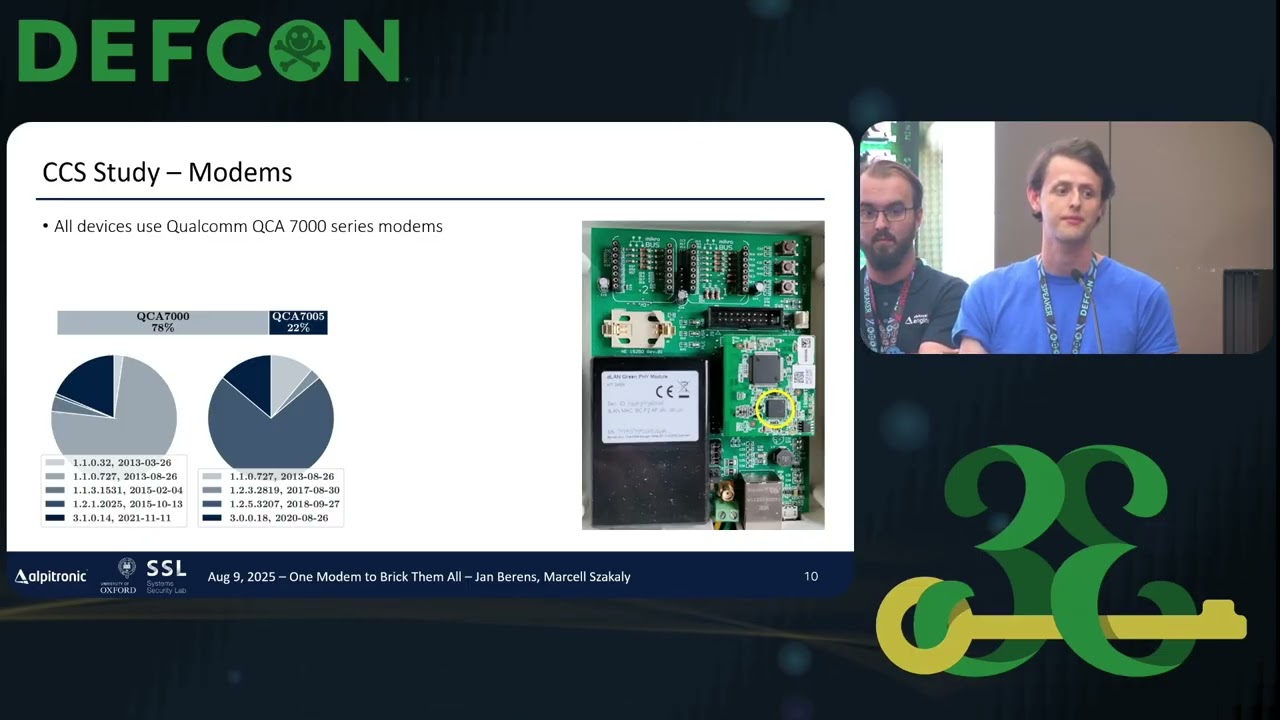
The video reveals serious security vulnerabilities in EV charging power line communication modems 0:03-0:08. Researchers found that virtually all chargers use just two types of modem chips (QCA7000 and QCA705) with over 60% having firmware older than 10 years 8:47-9:12.
Key Takeaways:
• Researchers built an EV emulator to test 397 chargers across multiple countries 7:26-7:31
• Discovered the "paper buster attack" allowing rogue devices to write to charger configurations 15:15-15:24
• Found a "security bit" that can block attacks but many chargers don't enable it 19:18-19:26
• Demonstrated attacks via the ground connection potentially allowing denial-of-service 28:44-28:52
The research shows how critical infrastructure lacks security updates even when vulnerabilities are known 10:12-10:14.
Sources:
- 0:03-0:08 Introduction to EV charger modem security research
- 8:47-9:12 Discovery of only two modem chips used in chargers
- 7:26-7:31 EV emulator testing across multiple countries
- 15:15-15:24 Paper buster attack vulnerability
- 19:18-19:26 Security bit discovery
- 28:44-28:52 Ground connection attack demonstration
- 10:12-10:14 Lack of security updates in charger firmware
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right, I I guess we should get started, right? So, welcome to our talk. Uh, we are going to be looking at kind of hacking some EV chargers and more specifically the kind of communication in the modems they actually use. So, yeah, it should be a fun one and we're excited to share this research with you. First of all, who are we? Yeah. So, my name is Yan Barren. Um, I work as a red teamer at Alpatronic, one of the largest charger manufacturers in the world. And yeah, and in my free time I volunteer at different conferences like here at Defcon as a goon uh and do my own uh research but most of it can't be publicized unfortunately. Right. And my name is Marcel. I'm a PhD student at the system security lab at the University of Oxford and I'm doing my PhD on the security of EV charging. So I…