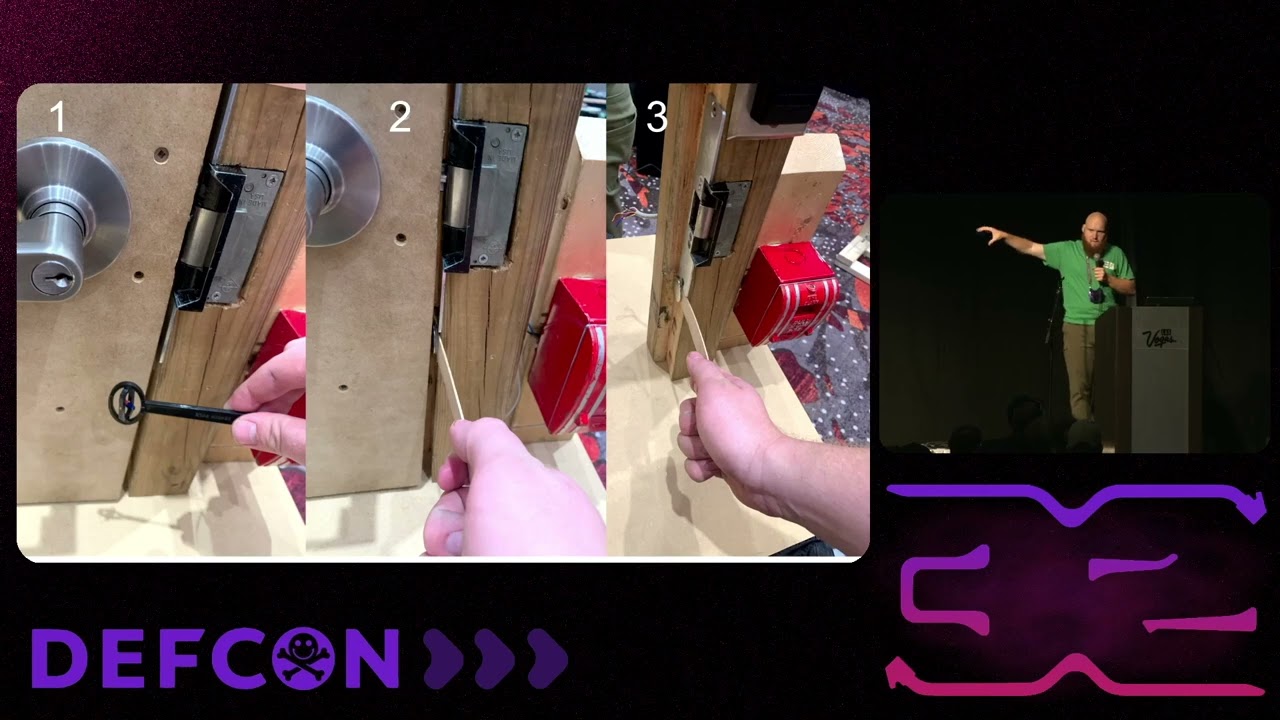
DEF CON 32 - Bypass 101- Bill Graydon
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 22:28
This talk focuses on identifying and reporting basic physical security failures rather than advanced exploits, as these "stupid [__]" vulnerabilities pose the most significant real-world threats 0:30.
Key Takeaways:
• Simple misconfigurations like improperly wired accessibility buttons can completely bypass door security systems 2:15
• Latch bypass vulnerabilities allow anyone with basic tools to open locked doors by manipulating the latch mechanism 4:38
• Most access control alarm systems don't function as intended, with door forced alarms typically getting logged but never triggering responses 15:05
• Camera surveillance often provides little value due to poor positioning, inadequate resolution, or improper lighting 18:06
Employees should prioritize reporting these basic security failures rather than advanced exploits to get taken seriously by management 21:11.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
welcome can everyone hear me all right everyone see the screen except for what is not loading so now is the part of the talk where you wholeheartedly Boo the speaker for not downloading his own slides locally before relying on the Defcon Wi-Fi to give the talk so let's let's hear it big old big old Boo for my lack of preparedness I [ __ ] it up already so this is actually a little bit appropriate though given a lot of what I'm going to talk about because what you if you were here for the talk an hour ago when we with physical security Village gave the bypass 101 talk we were talking about all the elite hacks that you can do to hack into physical systems and get them to behave in ways that they're not supposed to a lot of what this talk is going to end up converging on is not doing Advanced…