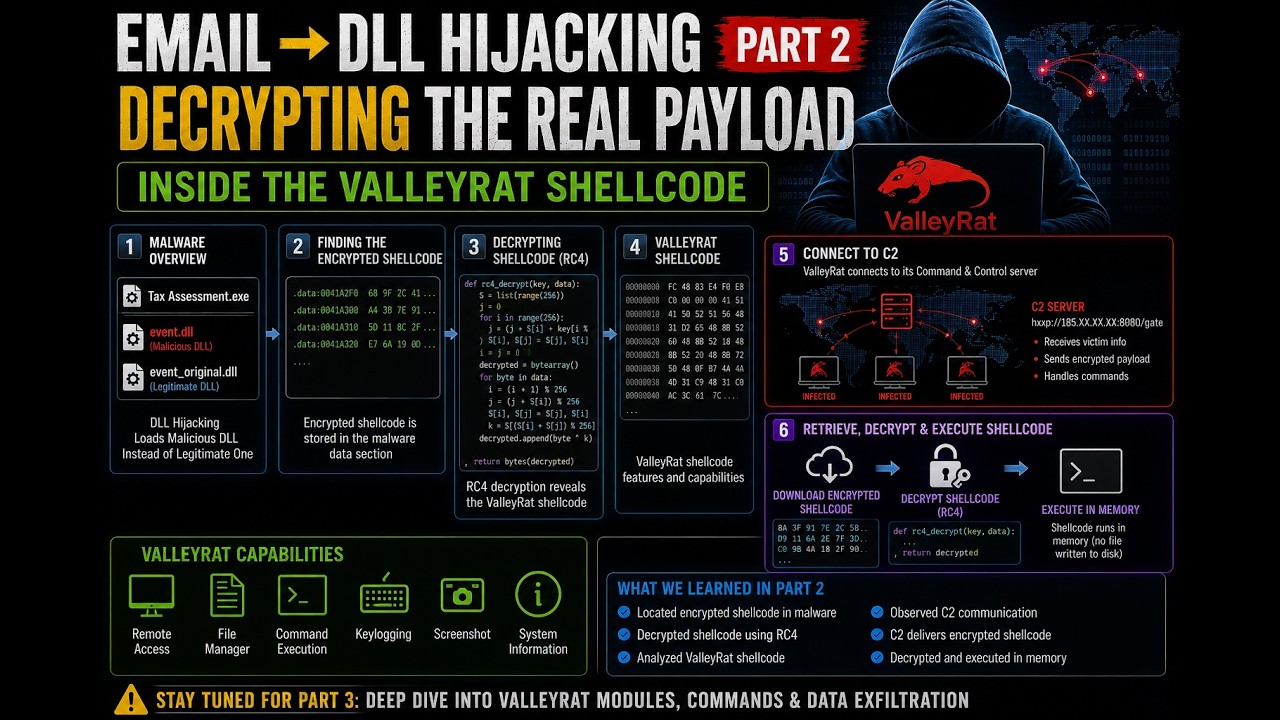
From Phishing Email to DLL Hijacking Malware | Threat Hunting & Reverse Engineering Part 2
Source: YouTube · Malware Research Diary · published Jun 27, 2026 · 1:11:04
This video analyzes a multi-stage malware campaign targeting Indian companies through a fake Income Tax Department website, ultimately delivering the ValleyRat backdoor via an ingenious DLL side-loading and payload concealment technique 0:31 22:25.
Key Takeaways:
• The attack begins with a phishing email that directs victims to a fake taxation site, which downloads a VHDX disk image file containing three files: a legitimate Microsoft executable (TextAssessment.exe), a malicious DLL (event.dll), and its original clean version 0:50 2:00.
• The malware uses DLL side-loading, where the malicious event.dll proxies all calls to the original DLL so the legitimate software functions normally, while simultaneously executing malicious code in the background 2:15 4:22.
• To evade antivirus detection, the attackers append encrypted shellcode directly to the end of the legitimate TextAssessment.exe binary, a section scanners typically ignore 9:45 16:02.
• The malicious DLL searches the legitimate executable for a specific signature ("DECODE"), extracts the appended payload, and decrypts it using RC4 before injecting it into a new process via VirtualAllocEx and CreateRemoteThread 19:49 20:42.
• The final payload is identified as ValleyRat, a known Chinese backdoor that uses API hashing to dynamically resolve functions and communicates with a C2 server in China using raw sockets 22:25 25:39.
The analysis demonstrates a sophisticated blend of social engineering, side-loading, and stealthy payload embedding, with the presenter suggesting the initial DLL code could be used to hunt for similar variants on VirusTotal 1:10:22.
Sources:
- 0:31 Initial discovery of the phishing campaign on AnyRun targeting Indian companies
- 2:15 Explanation of the DLL side-loading and proxying mechanism
- 16:02 Discovery of the encrypted shellcode appended to the end of the legitimate binary
- 20:42 Process injection technique using VirtualAllocEx and CreateRemoteThread
- 22:25 Identification of the final payload as ValleyRat linked to Chinese actors
- 25:39 ValleyRat's use of API hashing and raw socket communication
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello, welcome back to the second part in analyzing malware that I'm targeting India um deliver value rank. So I cheat a little bit um after when we stopped um I analyzed it yesterday um and I wasn't able to record it. So I'm just going to recap and go over the process in analyzing it and um where's the data lay. So um to going back to where we started um we identified we was hunting for a malware on any run and we saw one of this email that sending to um in Indian companies and the malware was um containing the PDF in here um and it land to this taxation um website, right? The income tax department. And once the user clicking on this download file, download button, they download a a image. And what we have is slightly different from this. um is what is a we download a virt um um the Micro…