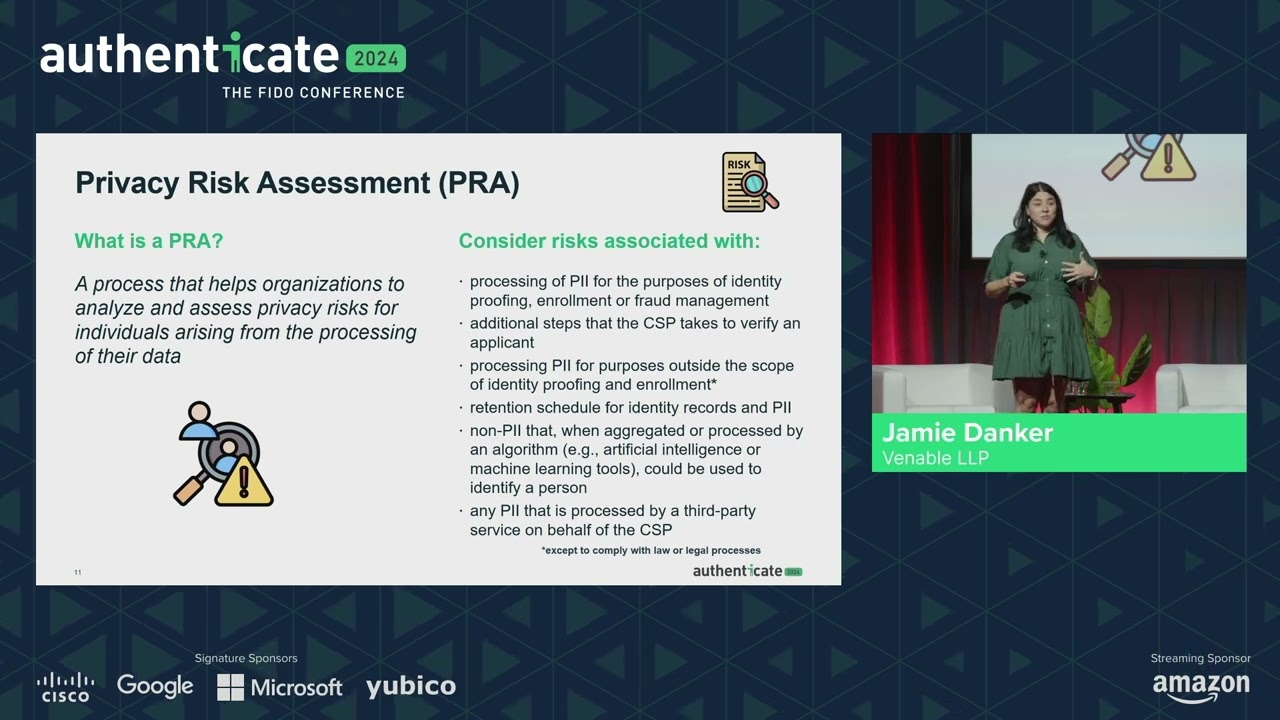
Privacy Considerations for FIDO and Beyond
Source: YouTube · FIDO Alliance · published Feb 6, 2025 · 20:22
BLUF: Jamie Daner outlines critical privacy considerations for PHTO (Privacy, Human, Technology, and Organizations) frameworks, emphasizing the integration of privacy into NIST guidelines and security risk assessments 0:09.
Key Takeaways:
• Daner introduces herself as a Senior Director at Venable with 15 years of civil service experience, highlighting her role as an author of privacy considerations for NIST SP 800-53 Rev 3 0:28.
• The presentation focuses on the intersection of privacy and security, noting that privacy requirements were historically separate but are now integrated into digital identity and security guidelines 0:43.
• She discusses the importance of "perking up" the audience for a concise 20-minute overview of complex privacy concepts 0:15.
Daner aims to provide a foundational understanding of how privacy must be woven into technical and organizational frameworks to ensure compliance and effectiveness.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Compliance & GRC. Commonly maps to: Security and Risk Management, Asset Security. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
it's my pleasure to uh announce Jamie Daner to this my colleague Jamie Daner to the stage she's senior director for privacy services at Venable she's going to be talking about privacy considerations with phto all right W thanks everybody um I hope you're a perky audience um I'm sure we're at the afternoon slump point so if you could just perk up a little bit for 20 minutes um I'd appreciate it um my name is Jamie Daner I'm with Venable um my practice is focused primarily on privacy but I do a lot of uh security risk assessment as well um backround about 15 years in civil service where I worked on um privacy programs both on the audit side of the house um I was an author of the privacy considerations for 863 rev3 that was the first time privacy requirements were included in the NIS digital …