DEF CON 32 - Process Injection Attacks w ROP - Bramwell Brizendine, Shiva Shashank Kusuma
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 22:49
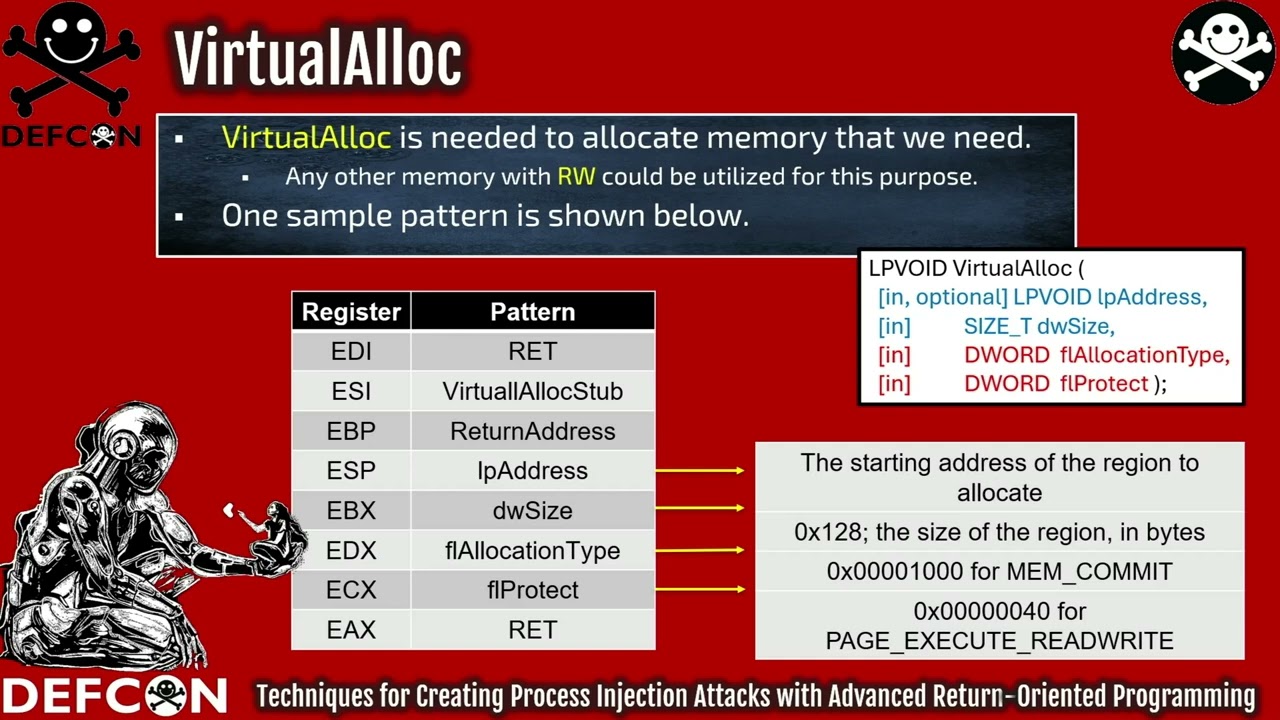
[BLUF] The video presents a novel return-oriented programming (ROP) methodology for process injection on Windows, using ROP chains to dynamically enumerate processes, inject shellcode, and execute it in external processes—without relying on traditional exploit techniques or custom malware. 1:48
Key Takeaways:
• The speaker introduces a robust ROP framework with over 150 unique patterns for Windows APIs and native calls, enabling flexible and reusable process injection techniques 4:57.
• A custom enumerating process function is built via raw assembly in writable memory, using ROP to iterate through processes and identify a target by string match (e.g., "VPlayer") 13:00.
• The ROP chain leverages pushad and movd references to build structures, manage memory, and retrieve critical values like PID and process handles, enabling precise targeting 14:44.
• Shellcode is injected into a target process using process memory APIs, with page permissions changed via virtual protect to allow execution 19:31.
• The complete ROP chain includes 29 gadgets, combining Windows APIs (e.g., LoadLibrary, CreateToolhelp32Snapshot, CreateRemoteThread) to achieve full injection and execution 9:24.
This work provides a scalable, reusable methodology for ROP-based process injection, emphasizing practicality and extensibility over brute-force techniques. 22:38
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
welcome welcome welcome to Defcon my name is Dr bral brisen dy I am the director of the Verona lab which deals with vulnerability research creator of the shell was which allows us to utilize Windows CIS calls and Shell Code I've created the jop rocket and Ro rocket both of which deal with return oriented programming and jump oriented programming and I've also created an NSA funded research project called Sherm which allows us to analyze uh shell code uh I've spoken at many different conferences in the past um and I'm also an assistant professor of cyber security I have a PhD in cyber operations which is a highly technical degree and all of those uh previous projects have um previously been presented at Defcon so check them out my co-speaker is uh shiver Shashank Kus he is a research assist…