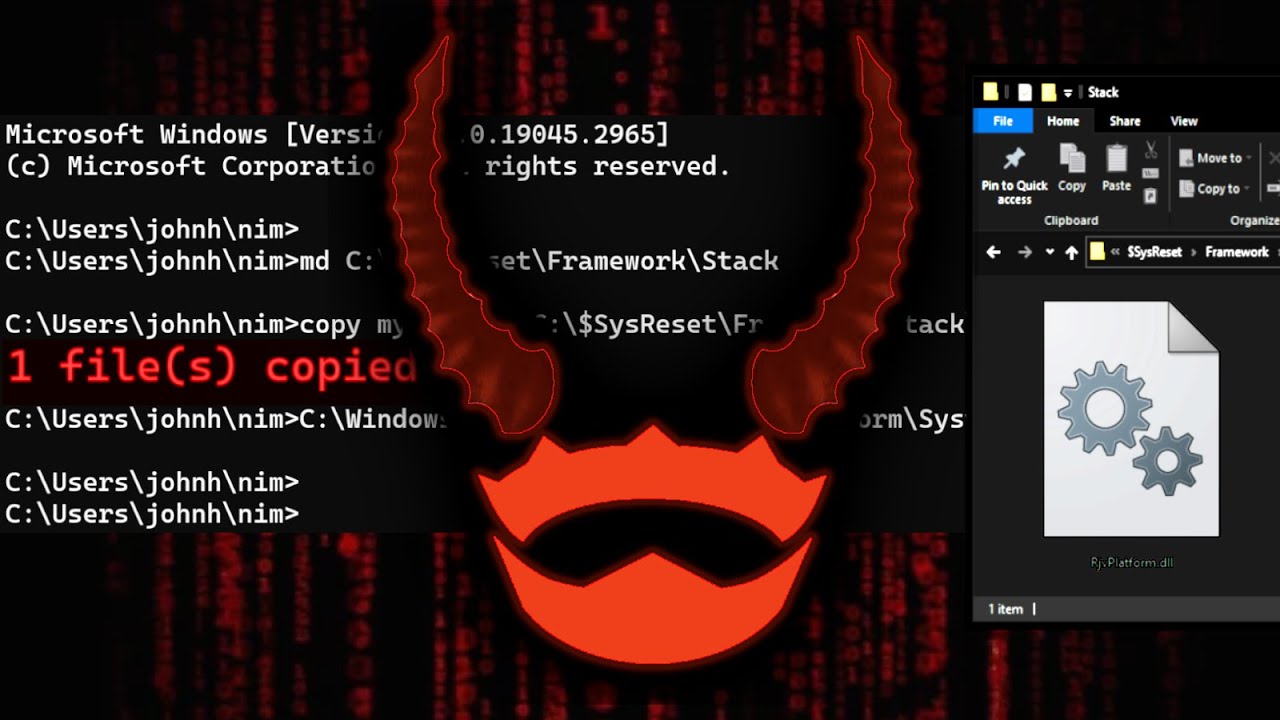
How Hackers Evade Program Allowlists with DLLs
Source: YouTube · John Hammond · published Jun 15, 2023 · 17:28
This video demonstrates a DLL sideloading technique using the Windows systemresetplatform.exe binary, showing how attackers can bypass security controls by exploiting how applications load DLL files 0:01-0:03.
Key Takeaways:
• Defense teams often choose easy solutions with security gaps, while attackers only need to break implementations, not entire security concepts 0:05-0:22
• "Living off the land" techniques use legitimate system tools to carry out attacks, making detection more difficult 0:45-0:49
• Application allow lists that only block .exe files but ignore DLLs create vulnerabilities that can be exploited 1:36-1:46
• The presenter demonstrates creating a malicious DLL with Nim that systemresetplatform.exe loads from C:$ResetFrameworkStack\rjvplatform.dll 13:36-13:50
• DLL allow listing is often neglected due to implementation challenges and user experience concerns 15:49-15:54
This technique highlights the importance of comprehensive security policies that address both executable files and DLLs to prevent such sideloading attacks.
Sources:
- 0:05-0:22 Discussion of security gaps in defensive measures
- 0:45-0:49 Explanation of "living off the land" technique
- 1:36-1:46 Application allow list vulnerabilities
- 13:36-13:50 DLL sideloading demonstration
- 15:49-15:54 Challenges of implementing DLL allow listing
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
the thing about defense is that administrators and key decision makers oftentimes want to go for the easiest most TurnKey solution the path of least resistance and this is a boon for the offense because as a hacker ethical hacker penetration tester red teamer all they have to do is not try to take advantage or dismantle a whole complete secure concept or idea they just need to break the implementation that means that misconfigurations or accidental forgotten or just unknown things gaps and holes in the security posture can open the door for this threat actor or offensive individual to do some more damage and of course that adversary will try to masquerade or blend in or remain stealthy and hidden in the work that they do and one of those common techniques that we talk about in cyber securi…