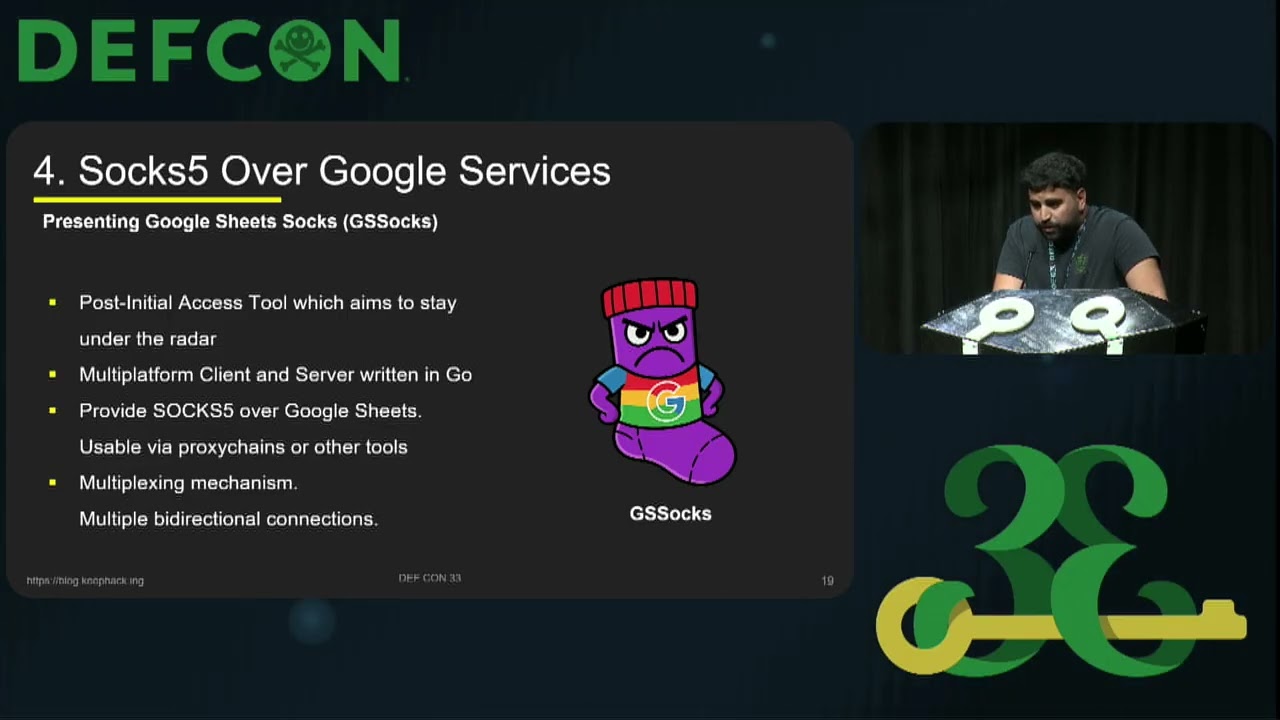
DEF CON 33 - RATs & Socks abusing Google Services - Valerio 'MrSaighnal' Alessandroni
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 15:58
[BLUF] The speaker introduces a new post-exploitation tool, GSOX, that tunnels arbitrary protocols through Google Sheets, enabling covert communication without direct attacker-target connections, building on prior abuse of Google Calendar for command-and-control. 1:55
Key Takeaways:
• GSOX enables protocol tunneling via Google Sheets using a SOCKS5 proxy, allowing execution of pentesting tools like secret dump with reduced latency 12:13.
• The tool avoids direct attacker-target links, making traffic inspection ineffective, as only Google infrastructure connections are observed 14:38.
• Payloads are B64-encoded and limited by Google Sheets’ 5,000-character cell constraint, leading to a 33% overhead and optimization via rotational account systems 11:15.
• Google’s security team previously identified the Google Calendar Rat (GCR) in 2023, and a similar technique was used by ABD41 in April, suggesting real-world exploitation 3:13.
[Closing statement] GSOX enhances the stealth and usability of cloud-based post-exploitation, leveraging Google’s trust while highlighting the challenges and limitations of such abuse.
Sources:
- 1:55 Introduction to GSOX and its protocol tunneling capability.
- 12:13 Performance improvements after payload optimization and rotational account system.
- 14:38 Traffic inspection limitations due to absence of direct connections.
- 11:15 Payload encoding constraints and overhead in Google Sheets.
- 3:13(https://www.youtube.com/watch?v
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everybody. Thanks to be here. Thanks Defcon. So um today uh we are going to talk about uh some way to abuse uh Google cloud services in order to perform u um some action in a context of redeeming operations. Uh first of all uh let uh let me introduce myself. My name is Baler Leandroni. Uh currently I am an offensive security leader at Hawaii Italy. Uh my background is uh based on pentesting and red teaming. So the first topic is uh um research I performed uh in 2023 which is called the Google calendar rat uh that was uh that is a tool uh a post exploitation tool that abuses of u uh Google calendar in order to use it as a common and control infrastructure. Why I I developed this tool? Uh first of all because I wanted to um reduce the time to set up uh common and control infrastructure…