Black Hat Asia 2026 | When 3.5 Billion Strangers Can Exploit Your WhatsApp Devices
Source: YouTube · Black Hat · published Aug 27, 2026 · 36:33
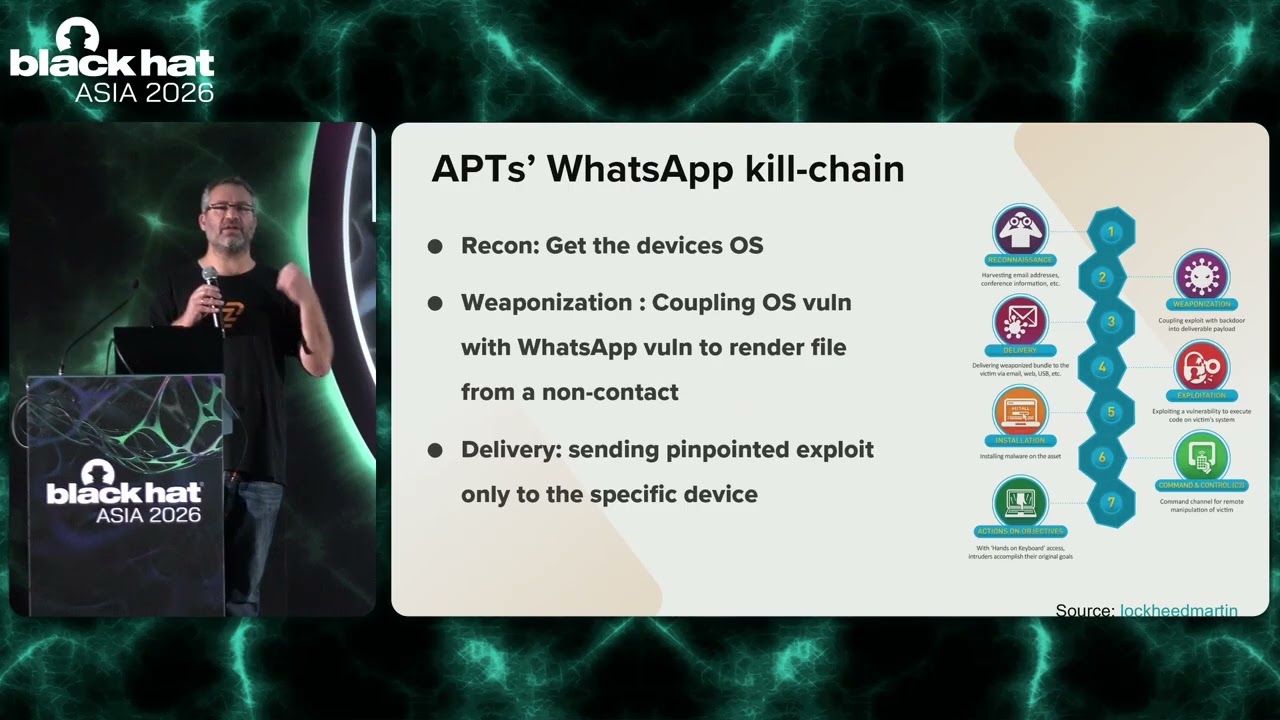
This Black Hat talk by Tal Be'ery shows WhatsApp's E2EE shifts risk from server to client, enabling rogue-client attacks—device enumeration, silent-ping stalking, and OS fingerprinting—forming a complete kill chain for pinpointed malware delivery 0:52.
Key Takeaways:
• E2EE (2016) makes the server a "dumb pipe," shifting attacks to individual endpoints 3:32
• Uploaded public keys are implicit device identifiers; Sesame multi-device makes all 5 trackable 12:12
• A research tool enumerates devices and sends different messages to each, enabling per-device payload delivery 16:52
• "Silent pings" enable online-status stalking with no user control or penalty 19:34
• Clients respond differently to malformed messages (iOS acks deletes, web acks reject-call), enabling OS fingerprinting and precise exploit delivery 25:27
• Meta partially fixed issues and paid a bounty, but gaps remain (e.g., detecting OpenClaw/Baileys agents) 27:34
• Fixes proposed: lockdown mode, message requests, and replacing Sesame with an ambassador-style protocol 33:05
WhatsApp's 2016-era security architecture must evolve to match its 3+ billion-user scale; users have no self-service defense today 32:26.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
very happy to be here. We just saw a 20 minutes long demo of display settings hacking. Uh so I hope we'll be fine. I don't know this is a computer I haven't used. So I hope everything will go well. So what are we going Okay. Okay. So welcome to the talk. Your number is up. Hacking WhatsApp when 3.5 billion people can hack your WhatsApp. And my name is Talberry. I'm the CEO for Zango. We've just been acquired by it Toro and this is my 10th time as Blacket speaker and I'm very excited to reach that mark. So what are we going to talk about today? We'll talk a little bit about WhatsApp security. Just a brief intro then we will focus on a rogue client attacks because there are could be attacks against WhatsApp server but we will talk more about the client raw client attacking each other. Okay. …