DEF CON 32 - Open Sesame: how vulnerable is your stuff in electronic lockers -Dennis Giese, braelynn
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 40:10
The main goal of this talk is to highlight critical security vulnerabilities in electronic locker systems, particularly focusing on firmware exposure, weak authentication, and lack of encryption, which can allow attackers to extract user data, clone keys, and gain unauthorized access to lockers 2:15.
Key Takeaways:
• Locks like Digilock and SAG have weak security due to unencrypted firmware, unprotected eROMs, and lack of cryptographic protection, enabling easy extraction of PINs and RFID IDs 5:31.
• Physical attacks, such as accessing debug pins or motor wiring, are feasible due to poor design and lack of tamper switches, allowing bypasses without complex tools 9:00.
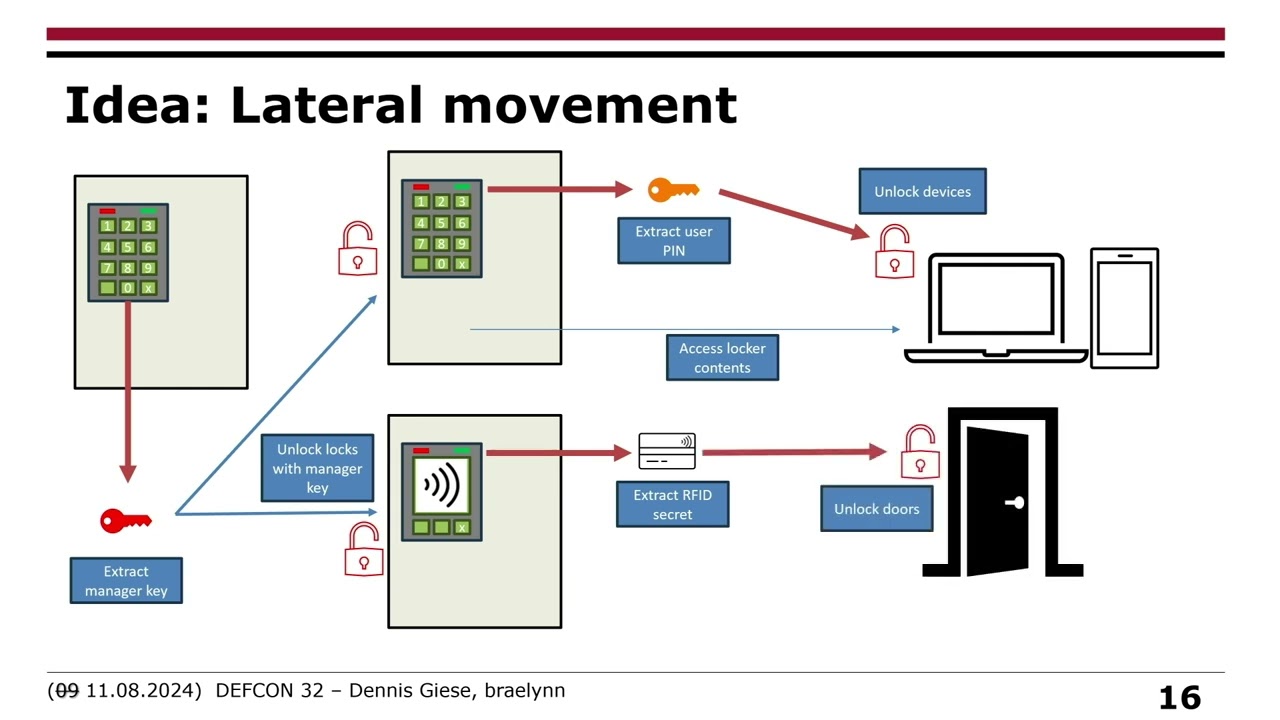
• A single manager key can grant access to all lockers in a system, enabling lateral movement and data theft, especially when PINs or RFID IDs are reused 12:20.
• The absence of secure boot, encryption, or secure storage means audit logs and user data can be tampered with or accessed directly 17:50.
Security in public locker systems is not robust—these devices are not designed for high-security use and are vulnerable to both physical and software attacks 36:16. Users should avoid reusing PINs across devices and treat locker PINs like passwords; the best defense is to use new, secure locks or avoid storing sensitive data in public lockers 37:49.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
[Applause] hello Defcon um thank you for being here on a Saturday morning I know everyone was partying yesterday until 5:00 a.m. properly so I'm glad that you here uh so yeah um now we're talking about um our talk uh open CM or how secur is your stuff in your lockers and this is the main question basically which we will talk through the talk um as you might I might heard there have been some uh issues with the talk in the past so I will kind of address it later so before we start uh with the topic um let me introduce myself real quick so um I'm Dennis I'm a security researcher or also a hardware hacker um and I basically am interested in viess and embedded security and privacy so I take a look at all kind of interesting devices which are around me um primarily this is uh vacuum robots uh b…