How You Can Impersonate Anyone in Active Directory (with Shikata!)
Source: YouTube · John Hammond · published Jun 25, 2025 · 26:29
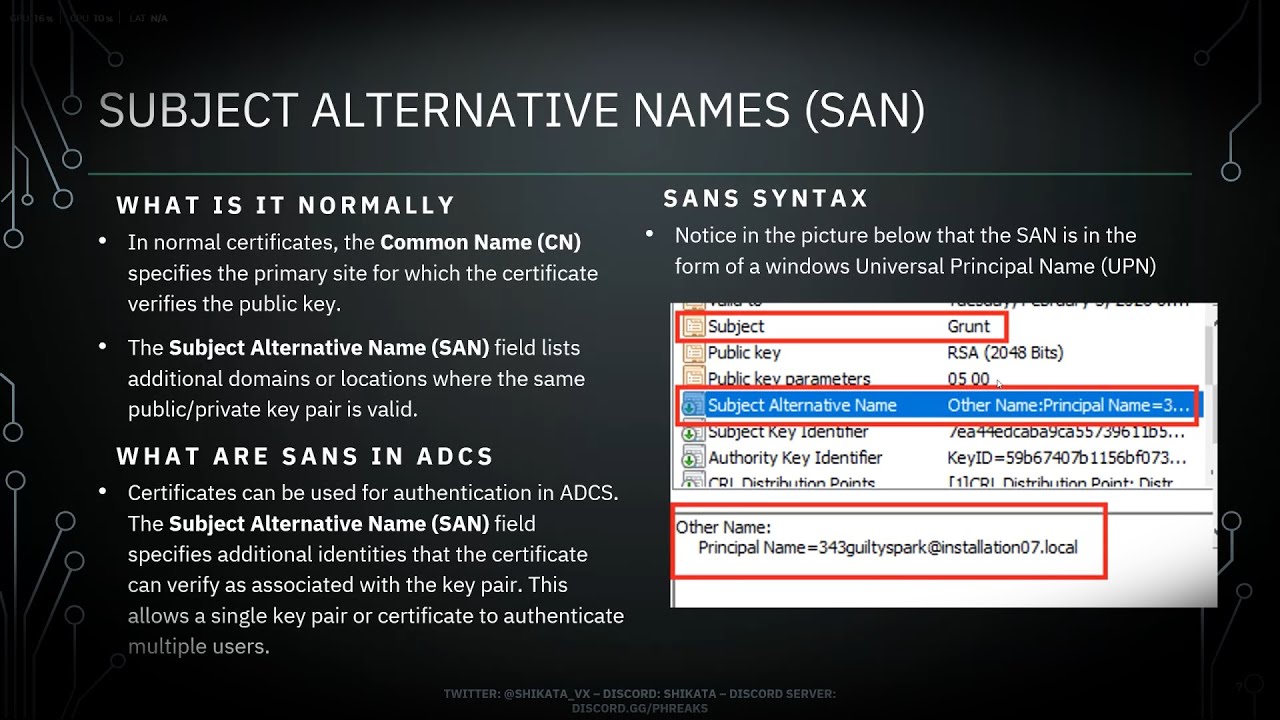
This video demonstrates how ESC1, a common Active Directory Certificate Services vulnerability, allows any authenticated user to escalate privileges by requesting certificates with impersonated Subject Alternative Names 0:38, potentially leading to full domain compromise.
Key Takeaways:
• ESC1 vulnerability occurs when certificate templates allow users to supply subject names in requests, enabling privilege escalation 0:47
• The web server template is vulnerable by default and commonly misconfigured in AD environments 4:28
• Attackers can combine ESC8 with ESC1 to gain initial access and escalate to domain admin 19:30
• The vulnerability allows any authenticated user to request a certificate impersonating another user, including domain admins 19:49
• ESC1 is still commonly found in enterprise environments due to historical misconfigurations 6:00
This vulnerability demonstrates how a simple misconfiguration in certificate templates can lead to complete domain compromise 23:10.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All righty. Hey everyone, thanks so much for jumping in again. Hey, I'm excited to get together with Shakana. We were recording just the other day for some Active Directory certificate service abuse, exploitation, really cool tricks in an AD environment. Hey, I think we got to roll through what was it? Petite Potam the other day, ECS8, kind of starting from zero, starting with nothing, no access in the environment, but then speedrunning and jumping straight to domain access with full control. So, that was really awesome. But I know might not always be the lay of the land in today's day and age. So, hey, whatever you got up your sleeve this time around, Shakata, I'm super excited. What are we digging into? So, today we're going to be digging into what's known as ECS1 or escalation one as it…