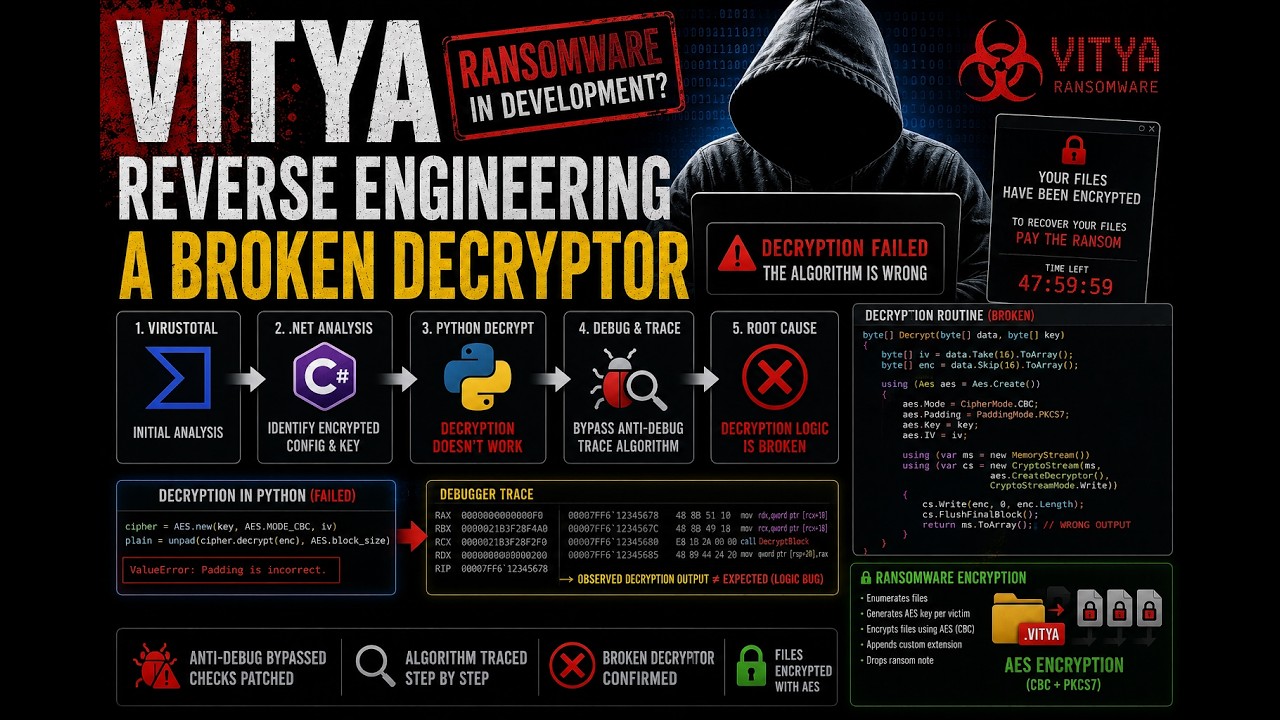
Reverse Engineering Vitya Ransomware | Debugging a Broken XOR Decryption Routine
Source: YouTube · Malware Research Diary · published Aug 4, 2026 · 23:24
This analysis of a suspicious .NET MSI file reveals a ransomware stealer communicating via Telegram, but its implementation is flawed due to an invalid decryption key and weak, predictable encryption that allows for potential reversal.
Key Takeaways:
• The file is an unsigned .NET MSI with a 23/70 VirusTotal detection rate, utilizing AES encryption and Telegram for C2 2:15
• Static analysis reveals hardcoded strings for crypto streams, Telegram tokens, and persistence mechanisms in the registry 2:30
• The malware gathers victim IP addresses and sends them to a Telegram bot, attempting to establish persistence 1:50
• Dynamic analysis shows the malware generates a GUI for ransom notes and encrypts files using a key derived from the username 6:55
• The analyst discovers the Telegram decryption key is invalid, indicating the malware is likely in a testing or development phase 17:40
• The encryption scheme is critically weak because the IV is statically generated and the key is predictable, enabling potential brute-force recovery 20:05
The analysis concludes that while the malware functions as a ransomware stealer, its poor implementation and invalid keys render it ineffective against determined defenders.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to another session in hunting for malware. Um Today I found a variety of different um upload for um Widow malware naming um VTI. And uh let's take a look and see what it is. So, let's check on VirusTotal first. Let's get a hash here. VirusTotal It's a MSI. So, um Okay. It's .NET. It's 23 out of 70. It's pretty high. Um Okay. So, it's mono's. Create time is in early in the year. Um and the submission for this is you know today. Um it's not signed. Okay. There is further behavior. Let's see if there's anything interesting. Um anti [clears throat] obfuscation obfuscated um C2 send data. Okay. Memory is connecting to such a type network. I don't know what that is. Telegram. Um Let's see. So, dropping some persistence likely persistence um and the registry, nothing …